
Blog de Cyera
Merci ! Nous avons bien reçu votre demande !
Malheureusement, un problème est survenu lors de l'envoi du formulaire.

Sep 10, 2026
Cyera on Cyera: Examining Snowflake Access Before Letting Agents Run Free
Leadership éclairé
Sep 9, 2026
AI Will Always Find a Way
Leadership éclairé
Sep 3, 2026
The Lethal Trifecta: Why Your Most Useful Agents Are Your Most Exploitable
Leadership éclairé
Sep 1, 2026
L'identité rencontre les données : définir la couche de confiance IA pour l'entreprise agentique
Nouvelles
Produit
Aug 26, 2026
Agentic Attacks Are No Longer Hypothetical: Four Lessons From the Hugging Face & OpenAI Incident Every Security Leader Should Know
Leadership éclairé
Aug 25, 2026
You classified your data. Now classify your agents
Leadership éclairé


Aug 12, 2026
Do You Know Where Your Agents Are?
Leadership éclairé
Aug 12, 2026
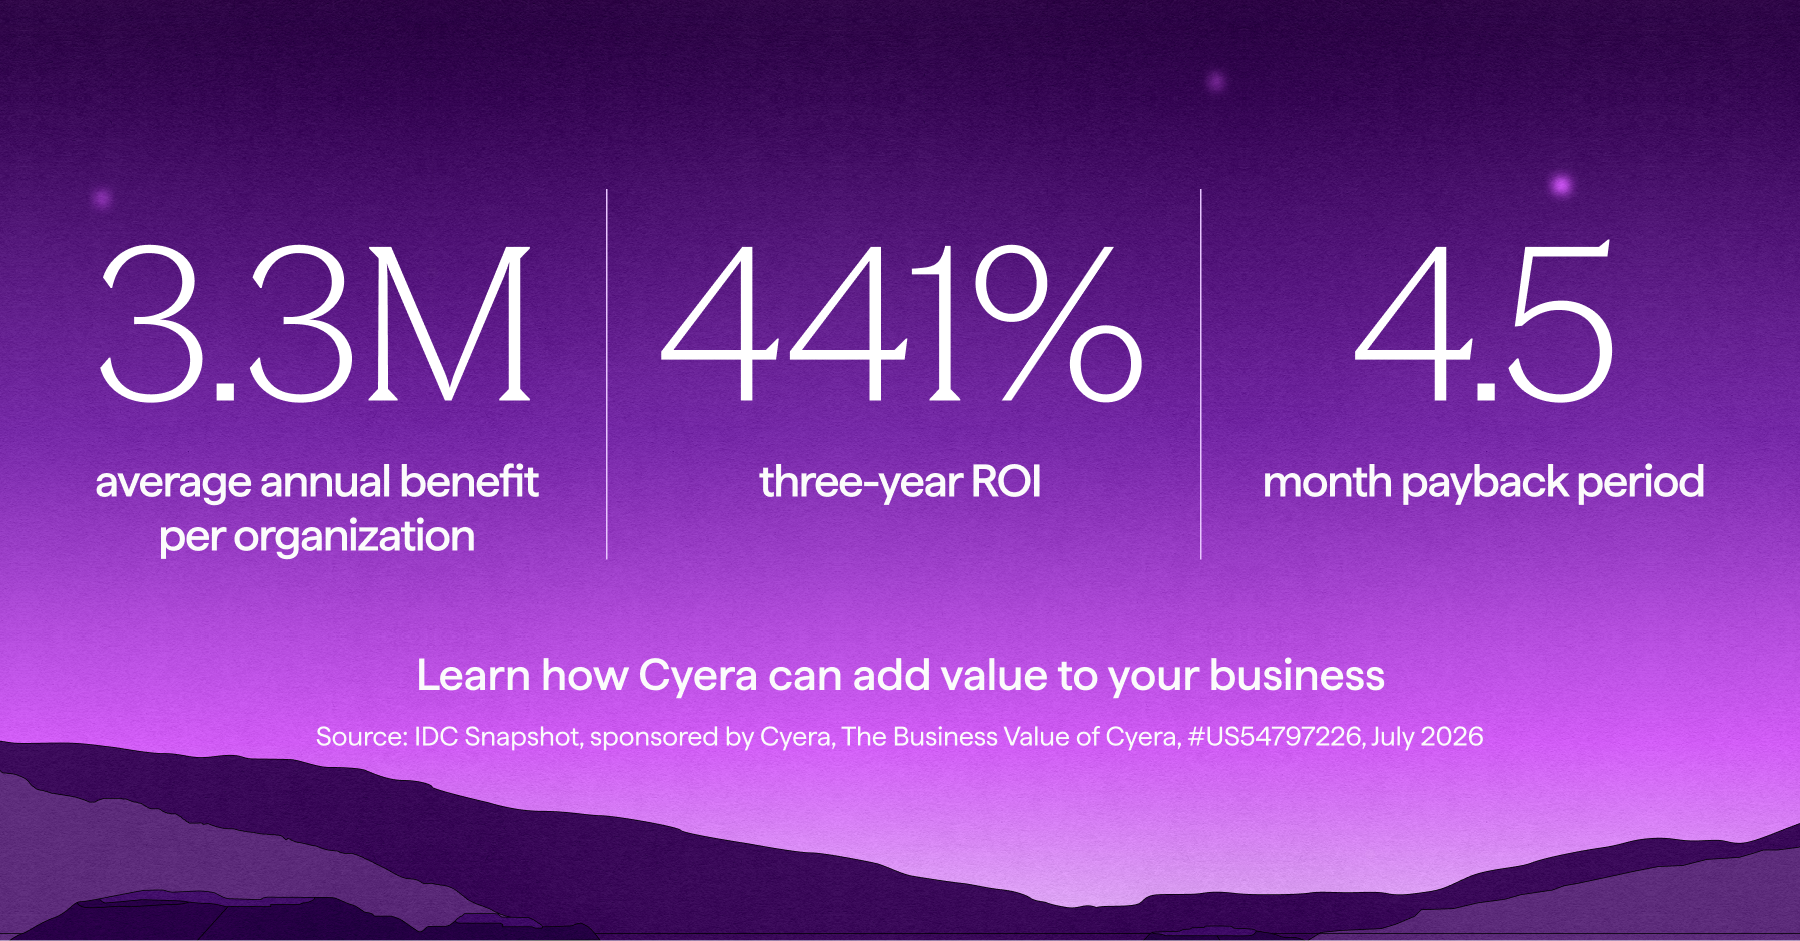
IDC Study: Cyera Customers Cut Data Risk and See 441% ROI
Leadership éclairé
Produit

Aug 10, 2026
What Happens in the Sandbox Doesn’t Stay in the Sandbox
Leadership éclairé

Aug 7, 2026
Local AI Security Fragility: Vulnerabilities Inside the Engine Running Your Local Models
Recherche Cyera
Aug 6, 2026
AI Agent Observability Explained: The Data Blind Spot Most Platforms Miss
Leadership éclairé
Aug 4, 2026
The Helpful Agent Problem Part IV: Key Security Capabilities for Agentic Success
Leadership éclairé

Aug 4, 2026
Cyera + Microsoft Agent 365: Bridge the Gap Between Agent Behavior and Data Access
Produit


Jul 30, 2026
Building the Control Plane to Secure Agentic Endpoints
Produit
Leadership éclairé

Jul 29, 2026
The Helpful Agent Problem Part III: The AI Insider
Leadership éclairé


Jul 27, 2026
The missing link in cyber resilience: Cyera and Cohesity’s bi-directional integration
Produit

Jul 20, 2026
Trusted AI Teammate or Frankenstein’s Monster? A Practitioner’s Blueprint for Safe Enterprise AI Adoption
Leadership éclairé
Jul 15, 2026
Le problème de l'agent serviable, partie I : quand les bonnes intentions se transforment en incidents de sécurité
Leadership éclairé


Jul 7, 2026
L'illusion de la gouvernance MCP : pourquoi il ne suffit pas de gouverner les outils
Leadership éclairé


Jul 1, 2026
Une nouvelle base pour la sécurité des agents : conçue à partir de la couche de données
Produit
Jun 18, 2026
Pourquoi les conseils d'administration associent systématiquement IA et données
Leadership éclairé
Jun 18, 2026
Maîtrisez les prises de contrôle de compte en quelques minutes avec Abnormal AI et Cyera
Produit
Jun 10, 2026
Bâtir la couche de confiance pour l'IA en entreprise
Nouvelles
Entreprise

Jun 5, 2026
Cyera Research découvre six vulnérabilités dans Protobuf.js qui affectent l'infrastructure des systèmes de données et d'IA.
Recherche Cyera
Recherche Cyera
Sep 1, 2026
PostGREShell: The database powering much of the internet had an open door for 12 years
Recherche Cyera
Aug 13, 2026
The Hidden Attack Surface of Agentic AI: Securing AI Agent Integration Platforms
Recherche Cyera
Aug 7, 2026
Breaking Local AI Runtimes: 10 vulnerabilities in the Engine Behind Your Open-Source Models
Recherche Cyera
Aug 7, 2026
Sandcastles, Not Sandboxes: How One Architectural Flaw Exposed Seven Products
Recherche Cyera
Jun 5, 2026
Proto6: The Schema Was Not Supposed to Run
Recherche Cyera
May 28, 2026
Agent-Inflicted Damage: Inside the Real-World Failures of Enterprise AI Systems
Recherche Cyera
May 15, 2026
Four New OpenClaw Vulnerabilities: When AI Agents Become the Attacker's Execution Layer
Recherche Cyera
Apr 29, 2026
SplitSSHell - When a Comma Becomes Root How a Single Character Broke OpenSSH Certificate Authentication
Recherche Cyera
Apr 22, 2026
The Data Taxonomy Illusion: Why Security Teams Are Solving the Wrong Problem
Recherche Cyera
Apr 7, 2026
One Megabyte to Root: How a Size Check Broke Docker’s Last Line of Defense
Recherche Cyera
Mar 26, 2026
LangDrained: 3 Paths to Your Data Through LangChain, the World’s Most Popular AI Framework
Recherche Cyera
Mar 19, 2026
96% of Enterprise Permissions Go Unused. AI Agents Won't Leave Them That Way.
Recherche Cyera
Feb 23, 2026
The Long-Lived Risk of Malicious OAuth Applications: A Practical Threat Hunting Guide for M365
Recherche Cyera
Feb 12, 2026
DESTRUCTURED - Critical Vulnerability in Unstructured.io (CVE-2025–64712)
Recherche Cyera
Feb 5, 2026
Detection Is Fast. Understanding Is Not. Why File-Access Incidents Stall - and How Impact Clarity Changes the Outcome
Recherche Cyera
Jan 26, 2026
Cellbreak: Grist’s Pyodide Sandbox Escape and the Data-at-Risk Blast Radius
Recherche Cyera
Jan 13, 2026
N8Scape (Pyodide sandbox escape): 9.9 Critical Post-Auth RCE in n8n (CVE-2025-68668)
Recherche Cyera
Dec 23, 2025
Escaping the Guest: How Custom LLM Workflows Uncovered Critical VMSVGA Vulnerabilities
Recherche Cyera
Dec 22, 2025
Why DSPM Has Moved From Buzzword to Board‑Level Mandate - and How Our New Guide Can Help
Recherche Cyera
Dec 5, 2025
The One Account That Breaks Everything: How Identity Outliers Create Explosive Risk
Recherche Cyera
Dec 2, 2025
Access Is the New Exposure: Why Knowing Who Can Reach Your Data Matters More Than Where It Lives
Recherche Cyera
Nov 25, 2025
Seeing the Forest: Why File-Level Classification Is the Missing Layer in Data Security
Recherche Cyera
Nov 20, 2025
Atlas and the Future of the Enterprise Browser
Recherche Cyera
Sep 29, 2025
Smarter at Scale: Why AI-Native Classification Techniques Outperform Exhaustive Scanning

Aucun résultat
Nous n'avons pas trouvé ce que vous cherchiez. Essayez de modifier les filtres.

