Cyera Identity
Securing access in the agentic enterprise.
Your AI program moves at the speed of your identity governance
+500%
growth in non-human identities across the Fortune 500, in six months.
40%
of enterprises will demote or decommission their AI agents because of governance gaps.
9/10
of agentic actions have no observable intent.
Context that drives action,
enforced at every point.
From non-human identity governance to real-time enforcement.
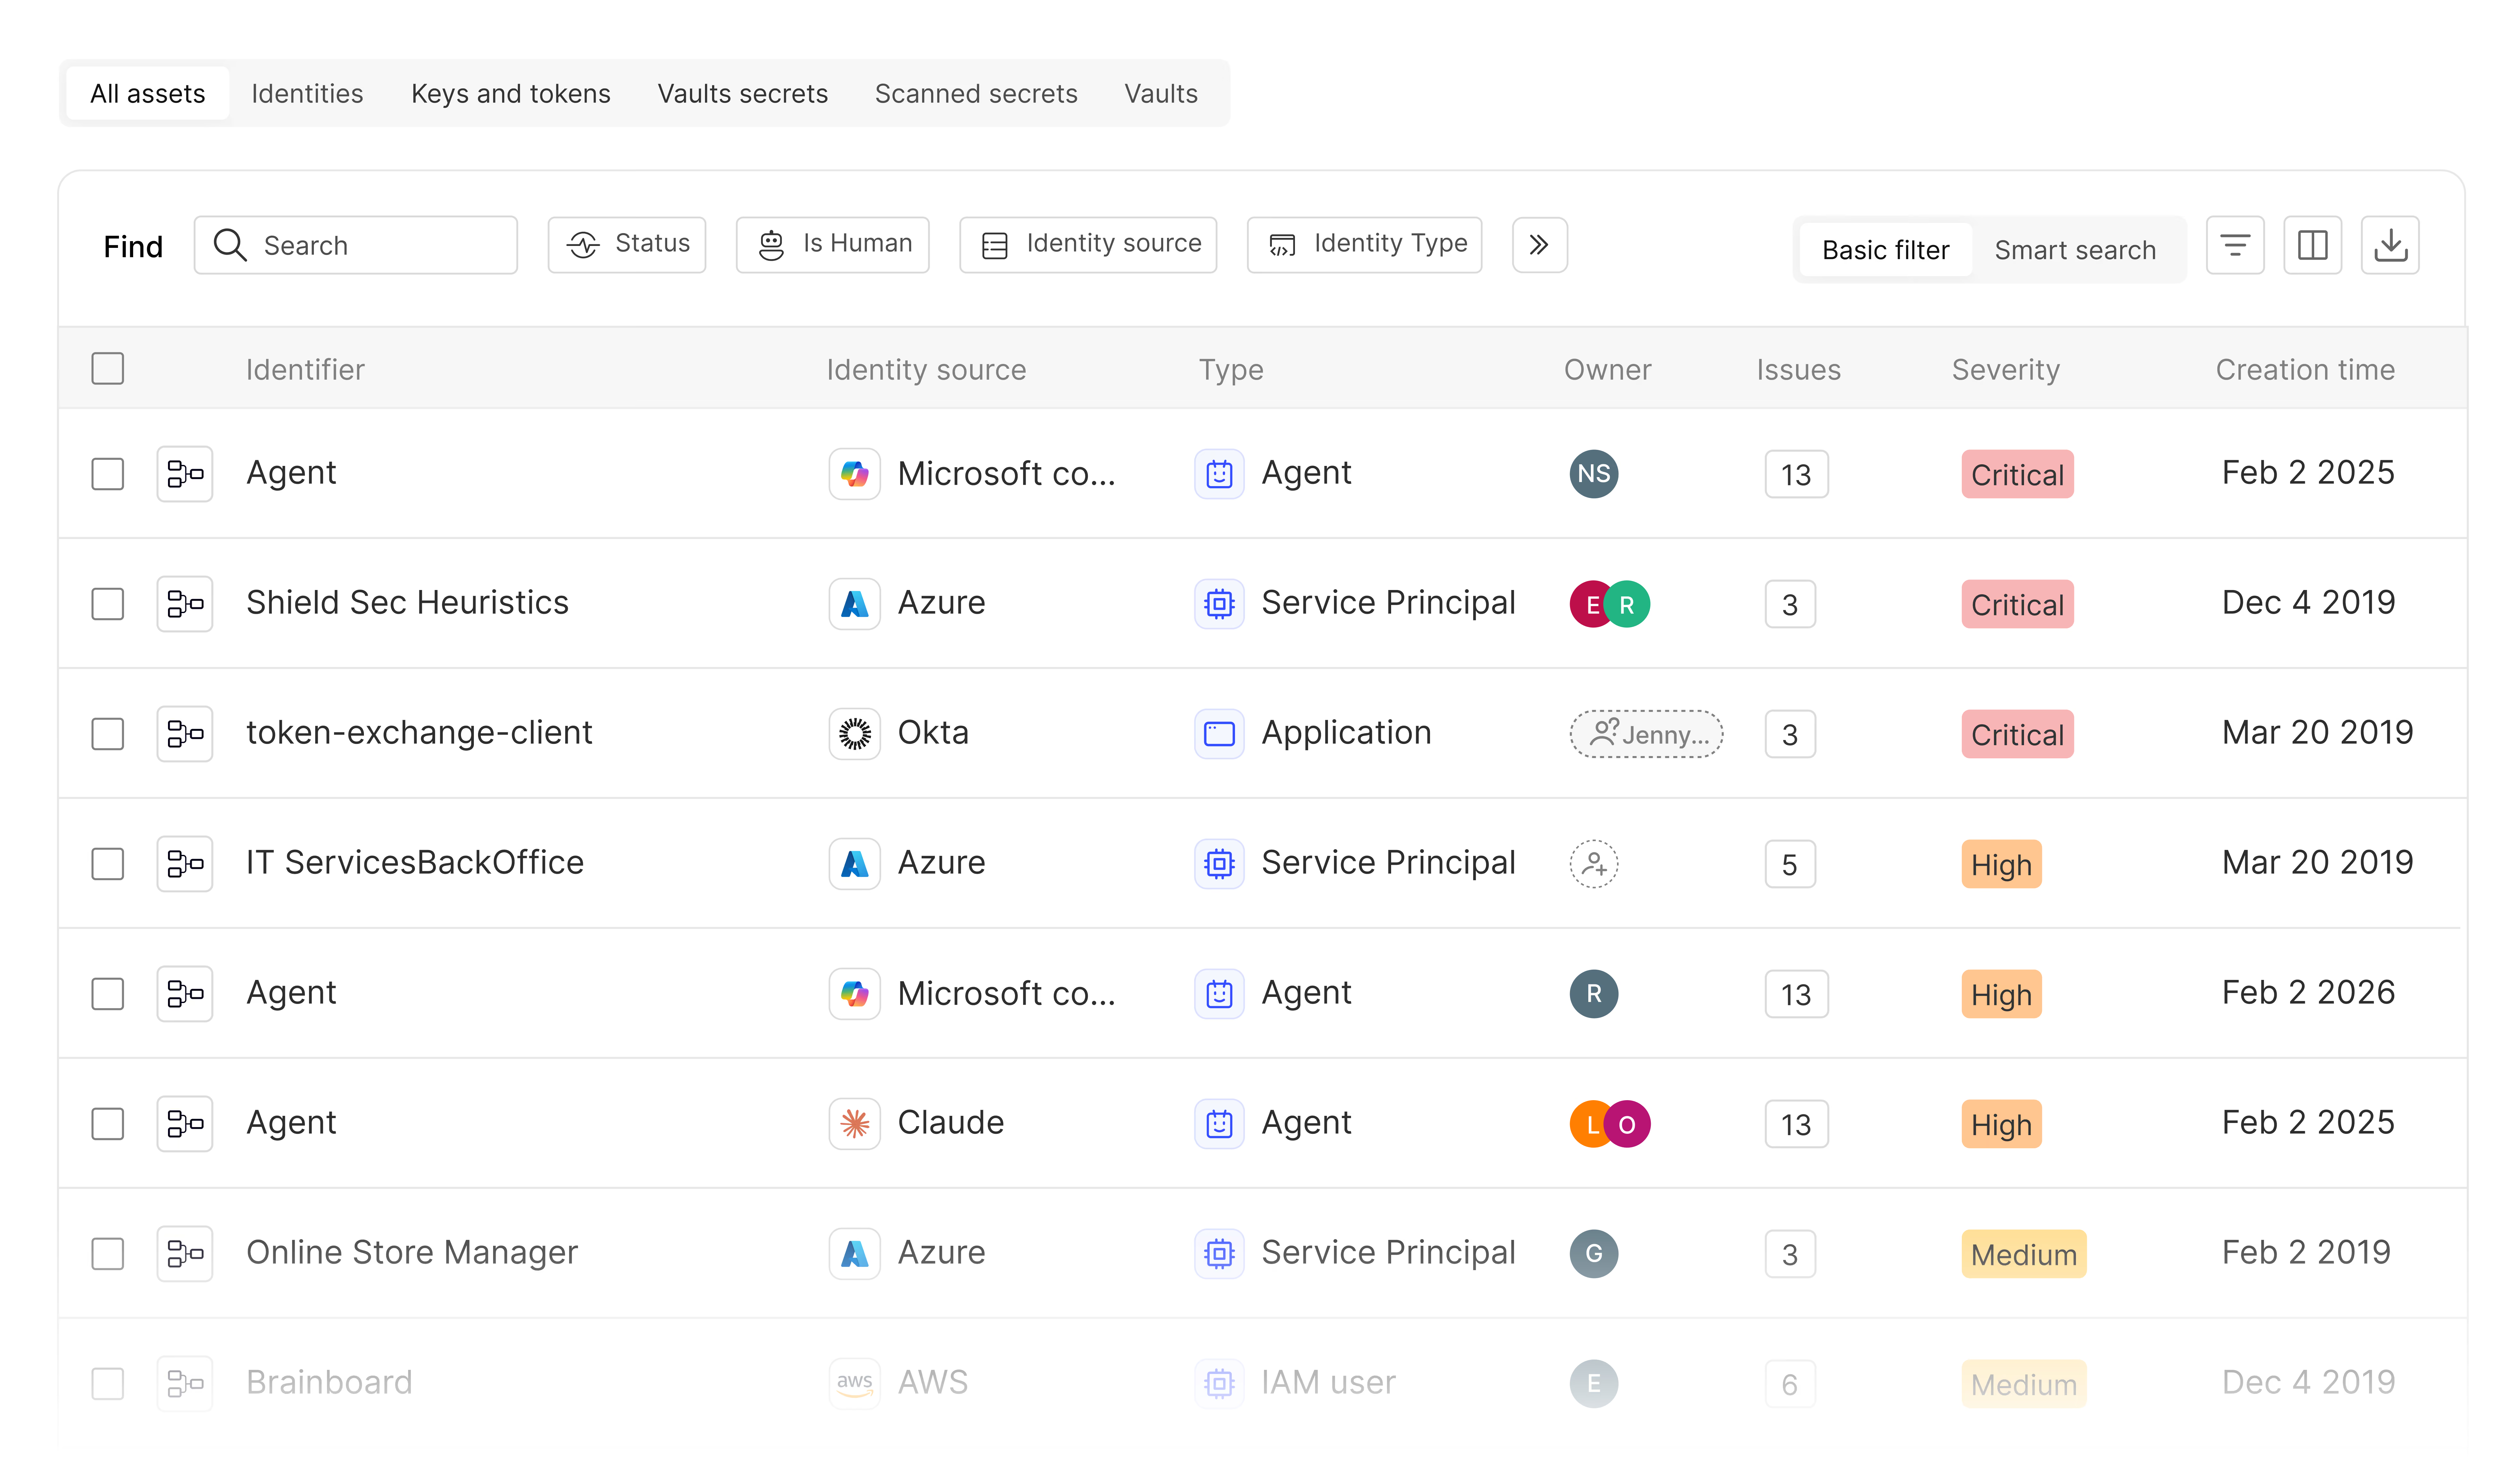
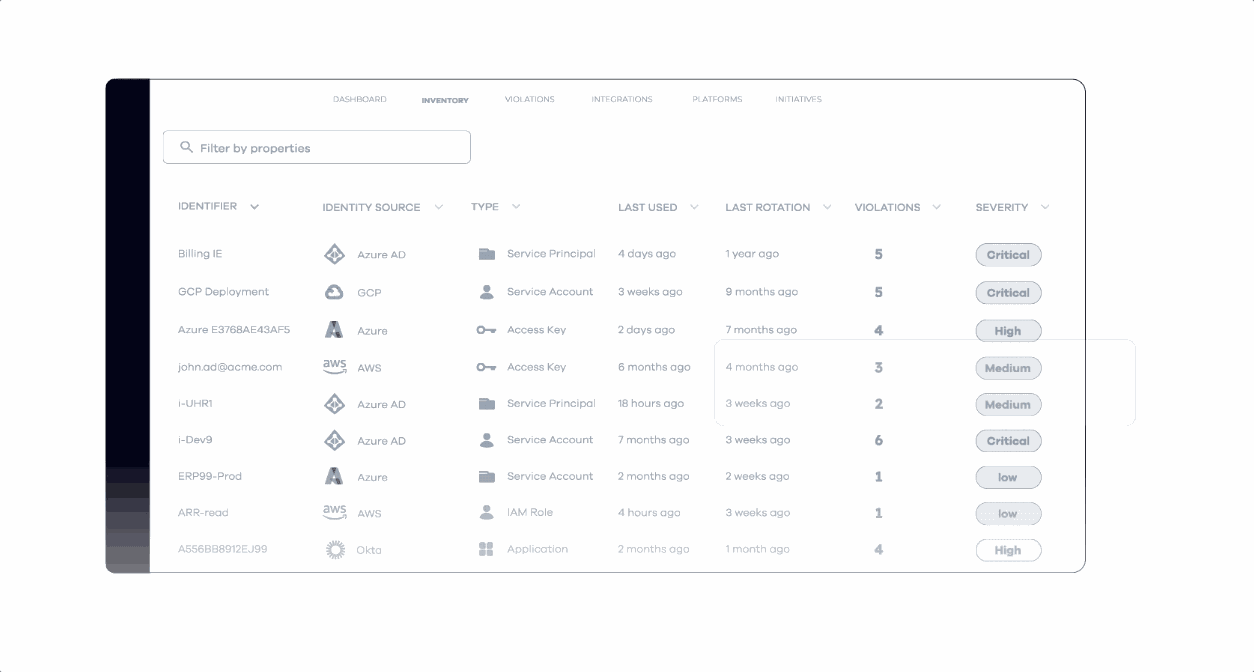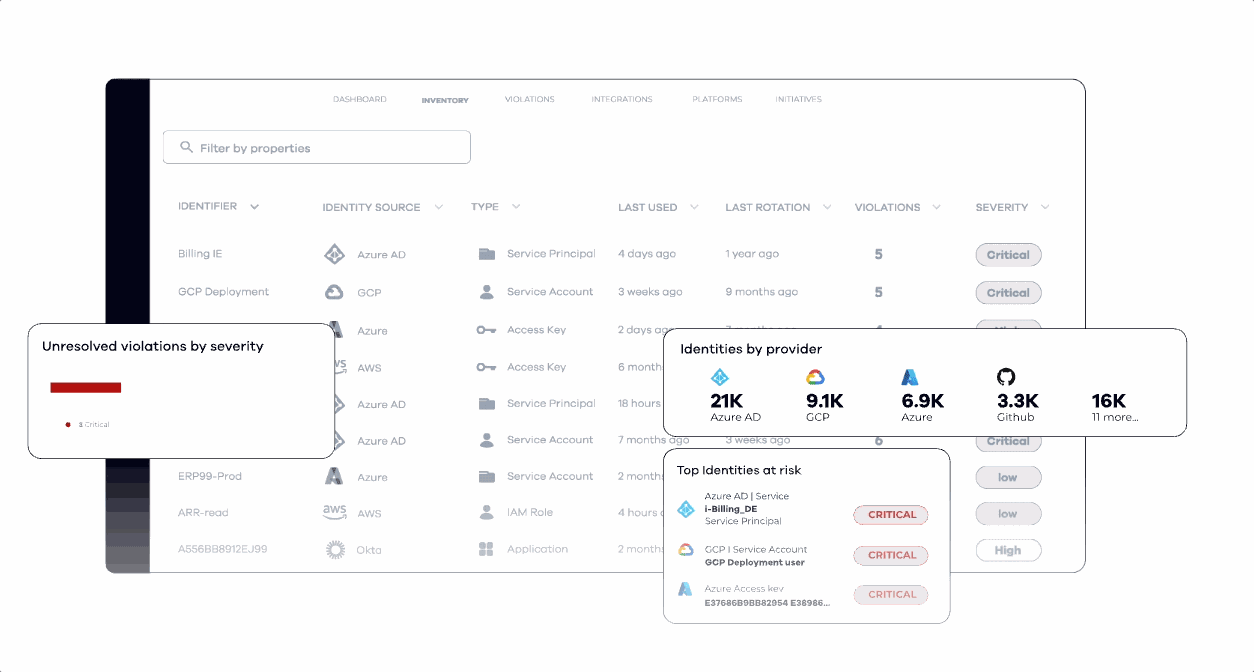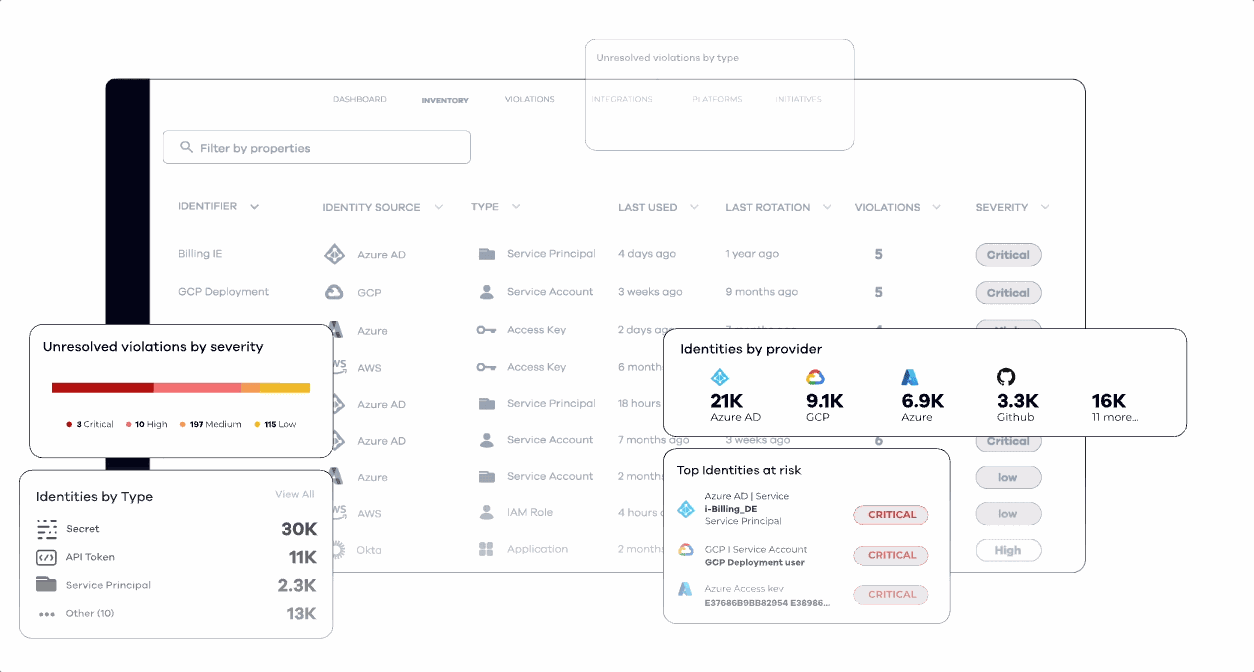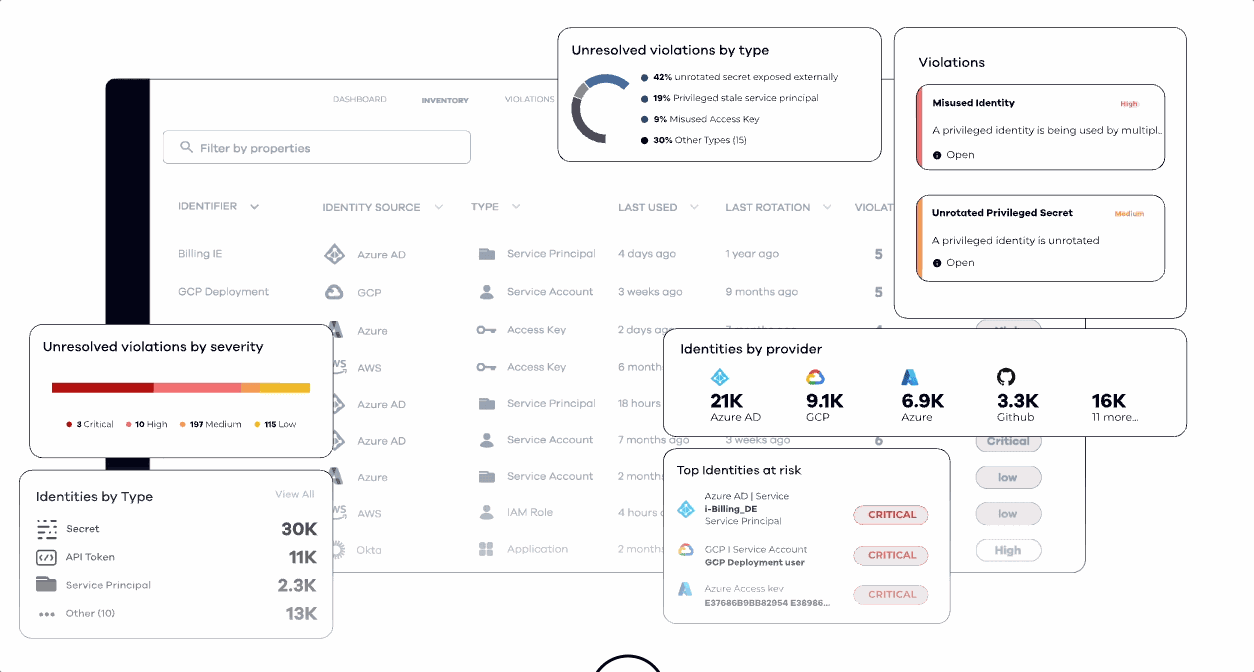
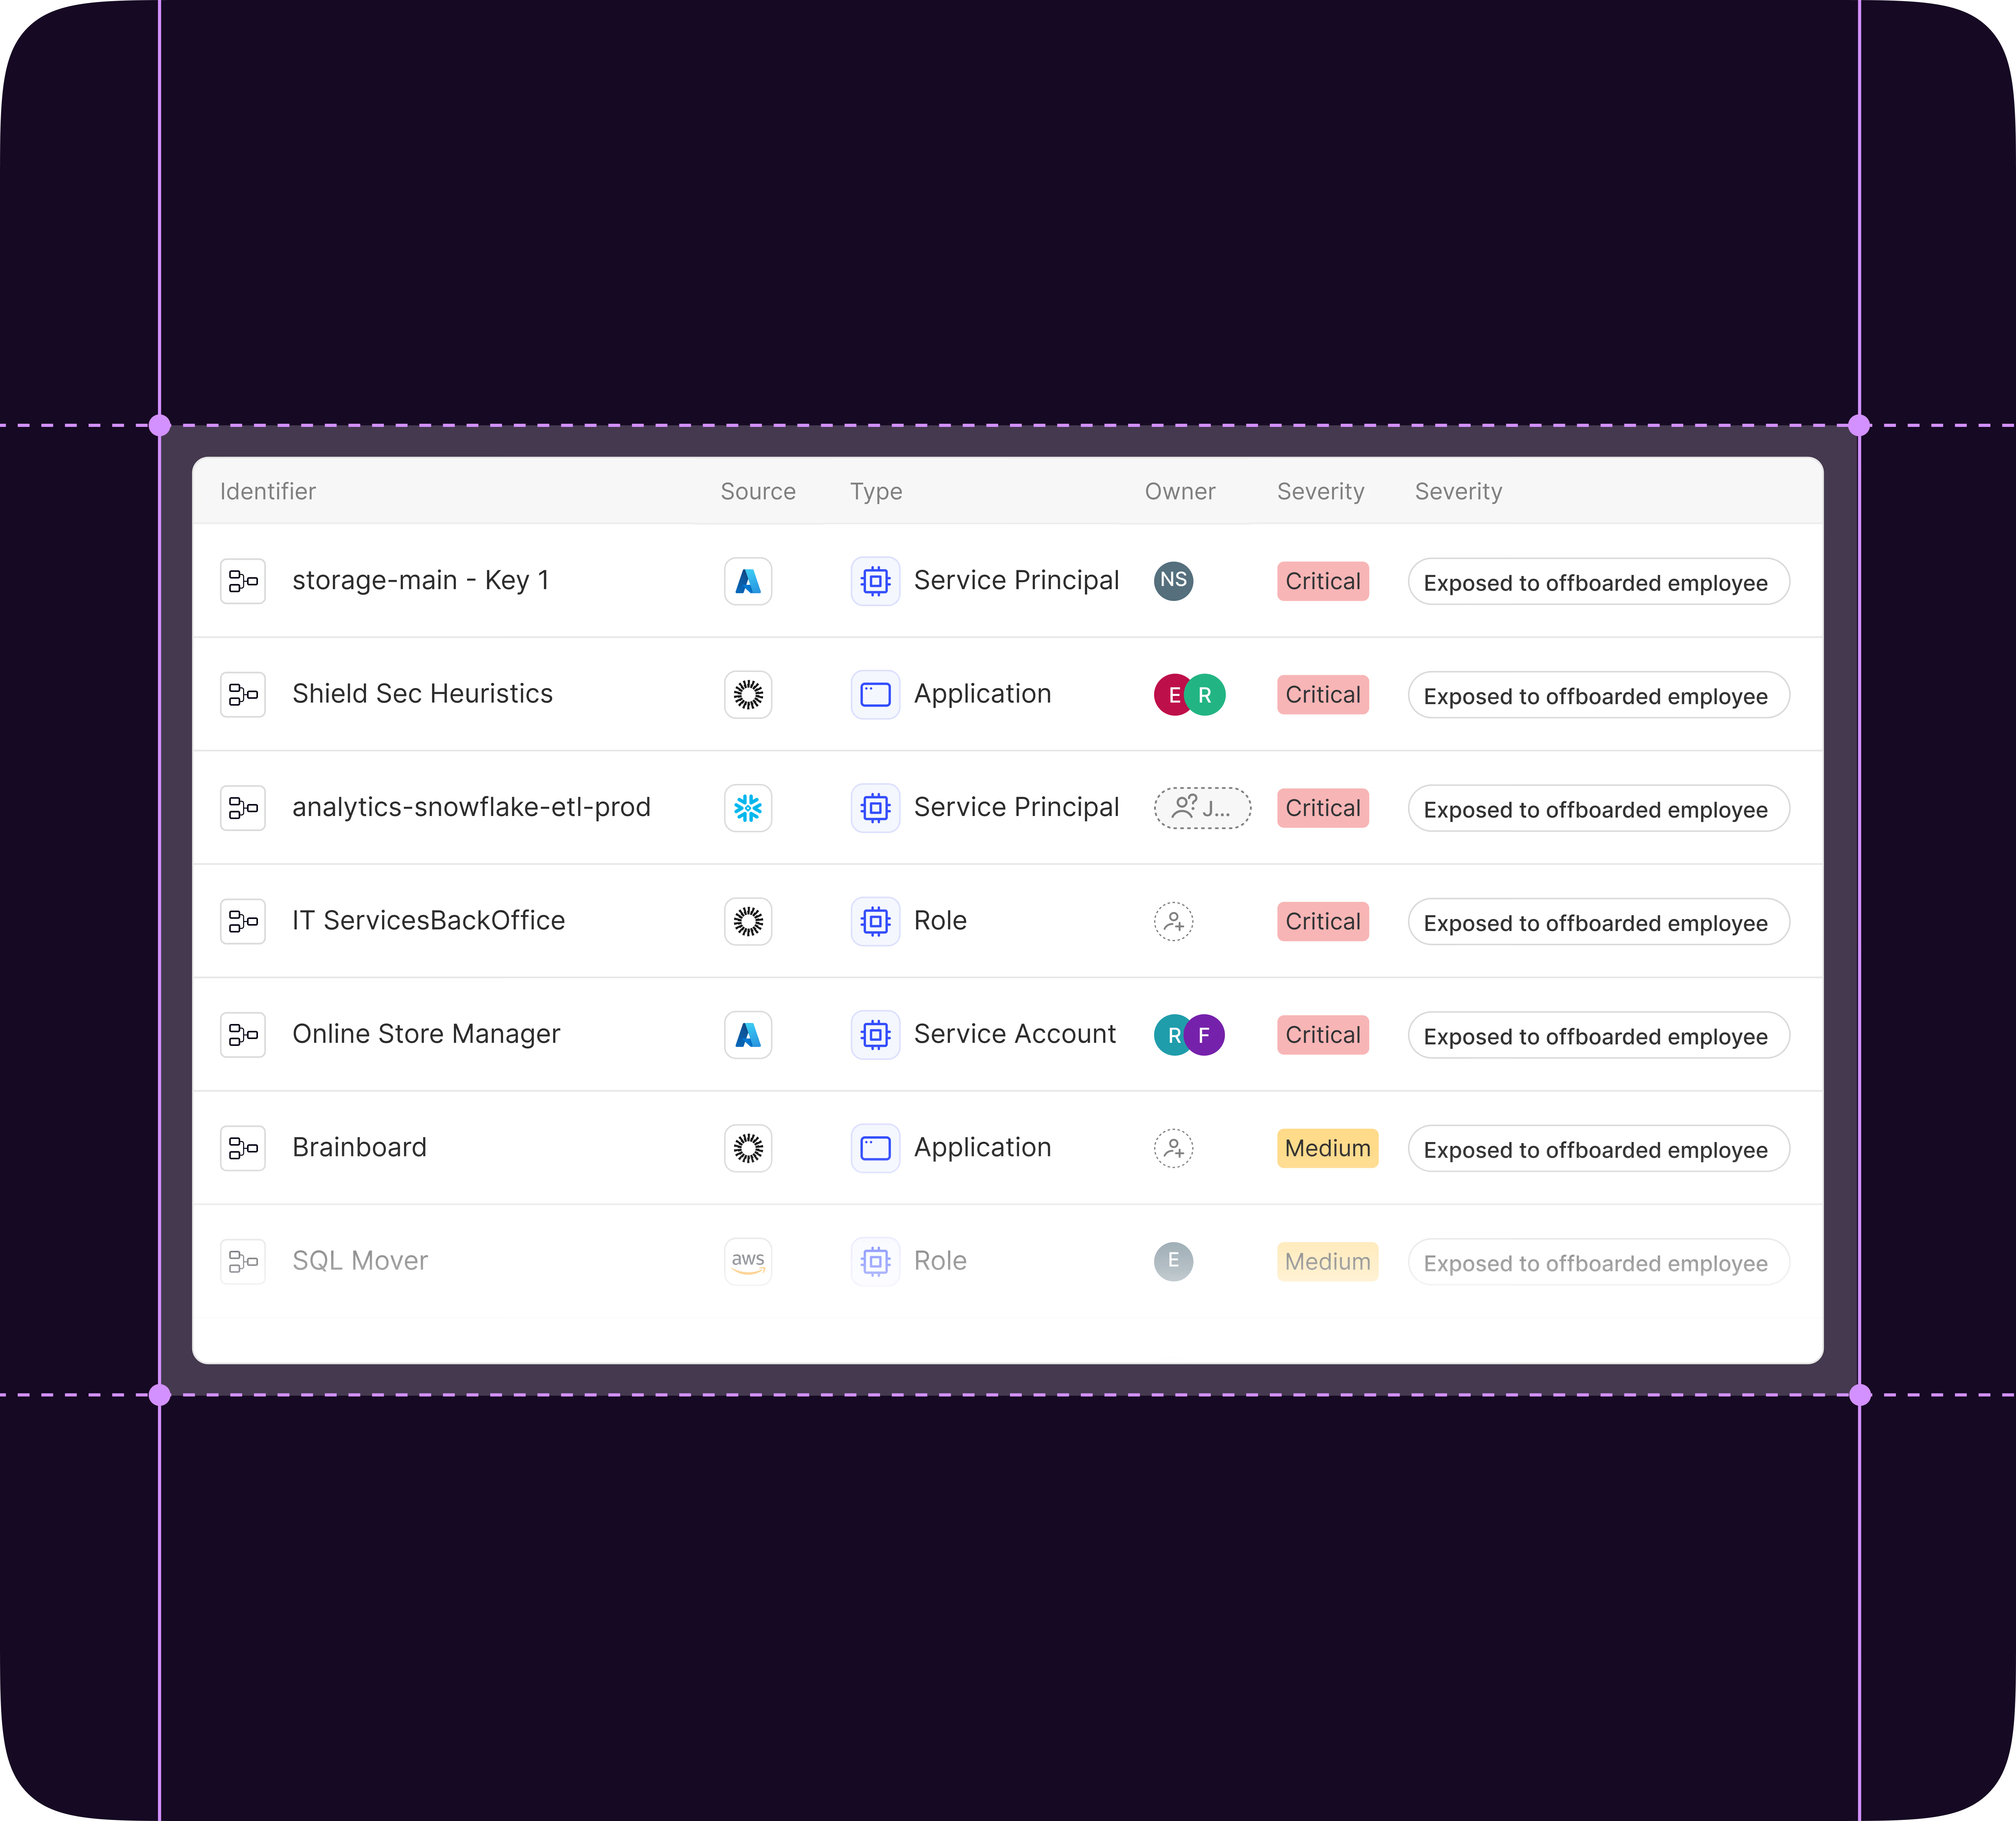
See every non-human identity and AI agent, and tie together usage, owner, risk, and the data it can reach. Govern every identity by policy, enforce agent access in real time, and hand your auditors the proof.
Lottie File version (below)
From non-human identity governance to real-time enforcement. Every AI agent, service account, and machine identity, controlled and enforced under a single policy and mapped to the data it reaches.
Chaque alerte est pré-analysée et prête à être traitée
Ne perdez plus de temps avec les faux positifs. Recevez des alertes fiables et hiérarchisées, accompagnées de l'analyse contextuelle dont vos équipes ont besoin pour appréhender l'ensemble des risques internes. Passez de l'investigation à l'action en quelques minutes.
Des politiques prêtes à l'emploi
Ne passez plus à côté d'une exfiltration de données critique. Les politiques s'écrivent, se testent et s'ajustent automatiquement pour combler les failles de couverture à mesure que de nouveaux modèles de comportement apparaissent. Votre protection s'adapte et se renforce au fil du temps, sans aucune intervention manuelle.
Observez-le au repos, stoppez-le en mouvement
Transformez la classification approfondie des banques de données et la connaissance des identités en prévention proactive avant que les données ne transitent par e-mail, le cloud ou l'IA. La synergie entre DSPM et DLP.
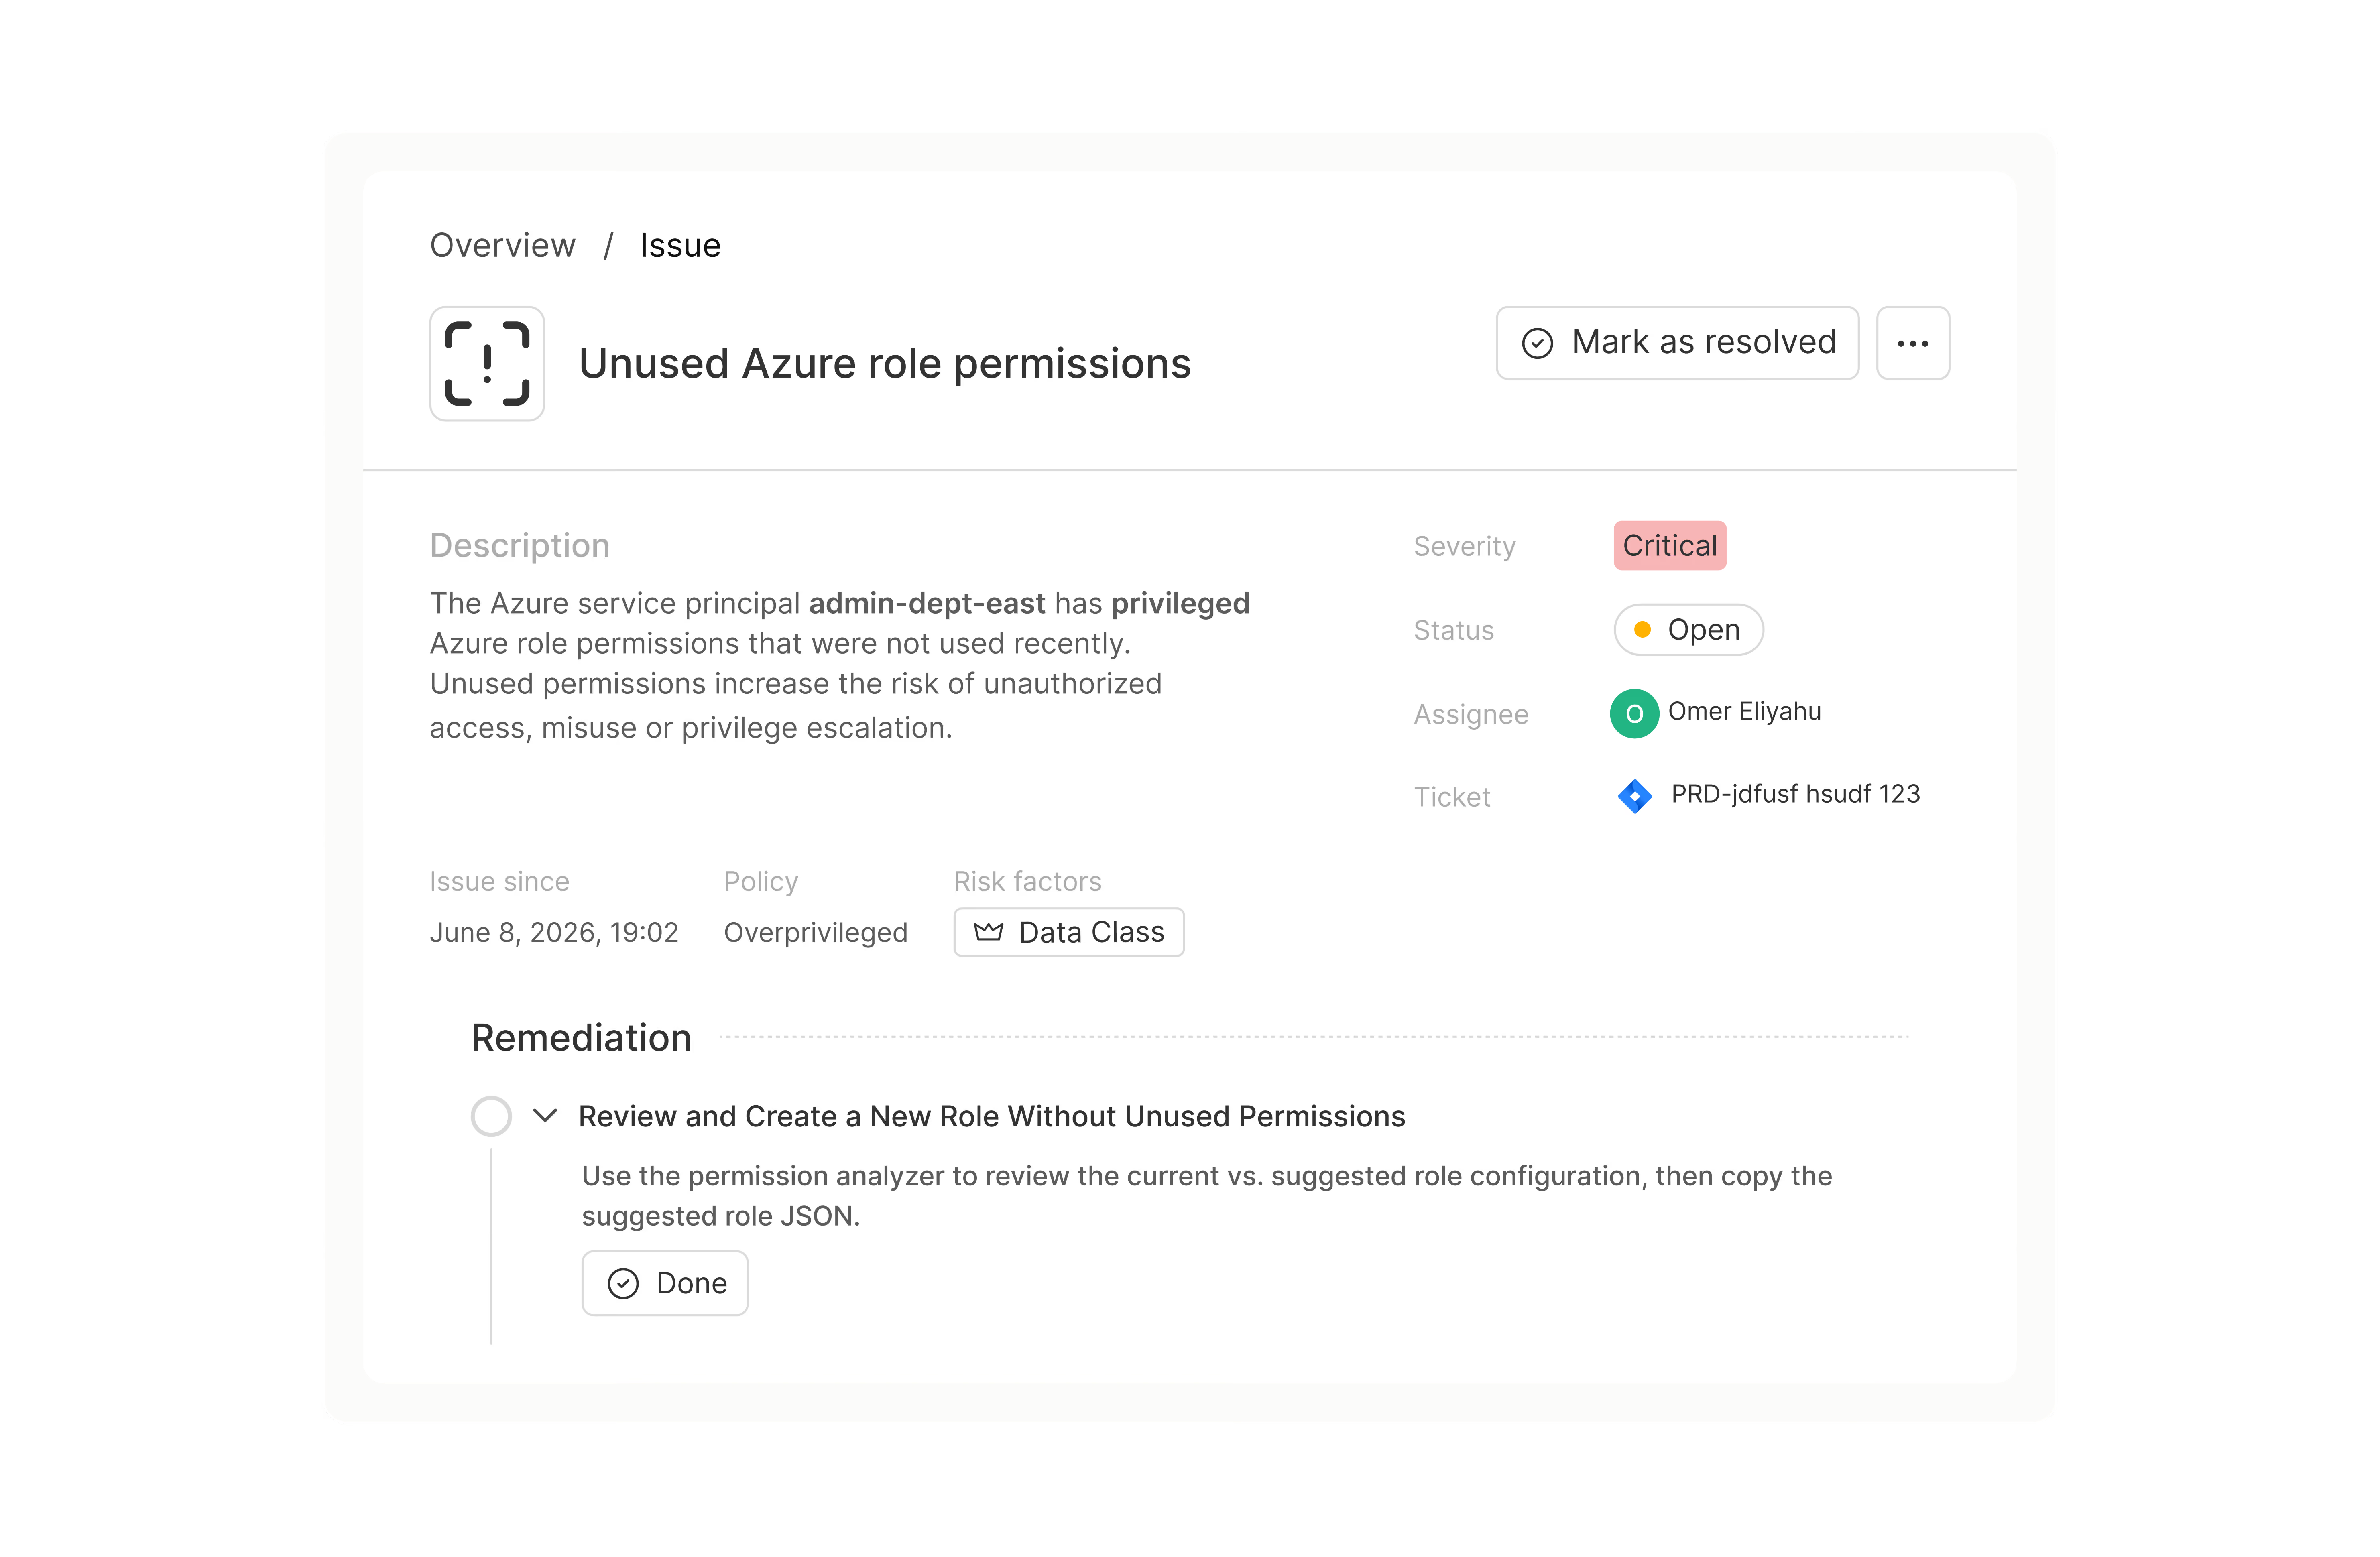
Fix identity risk without breaking production
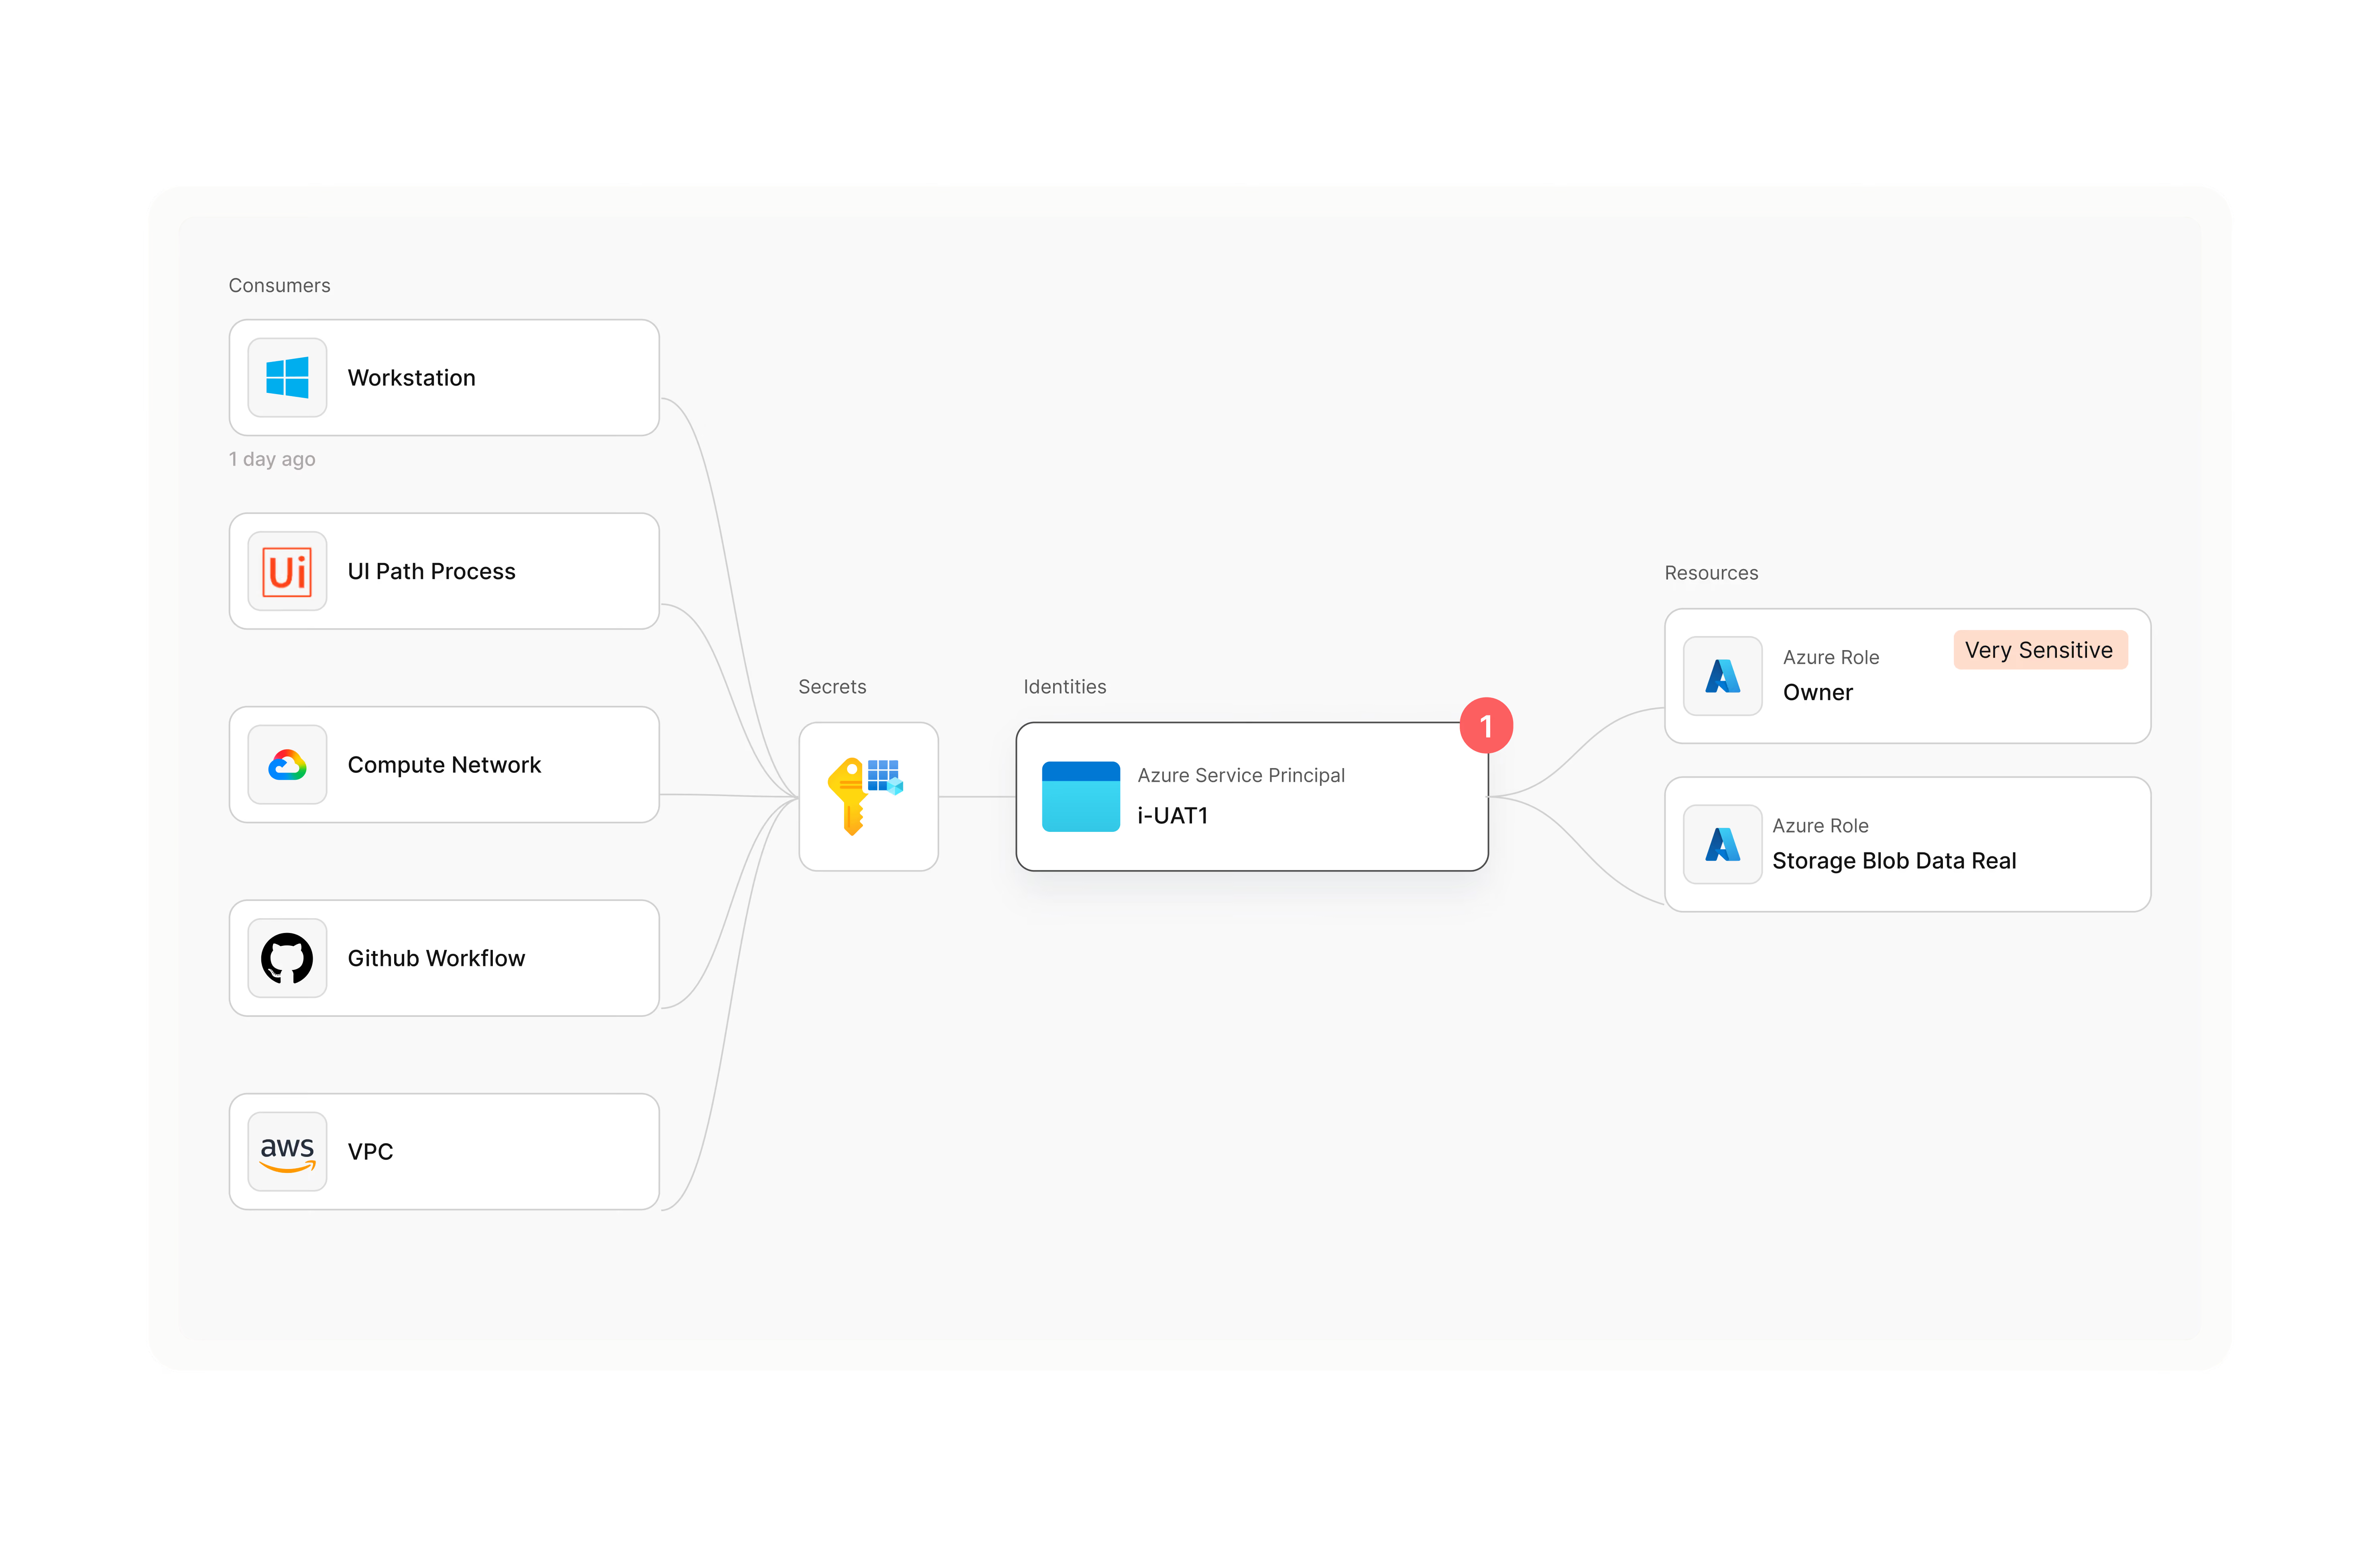
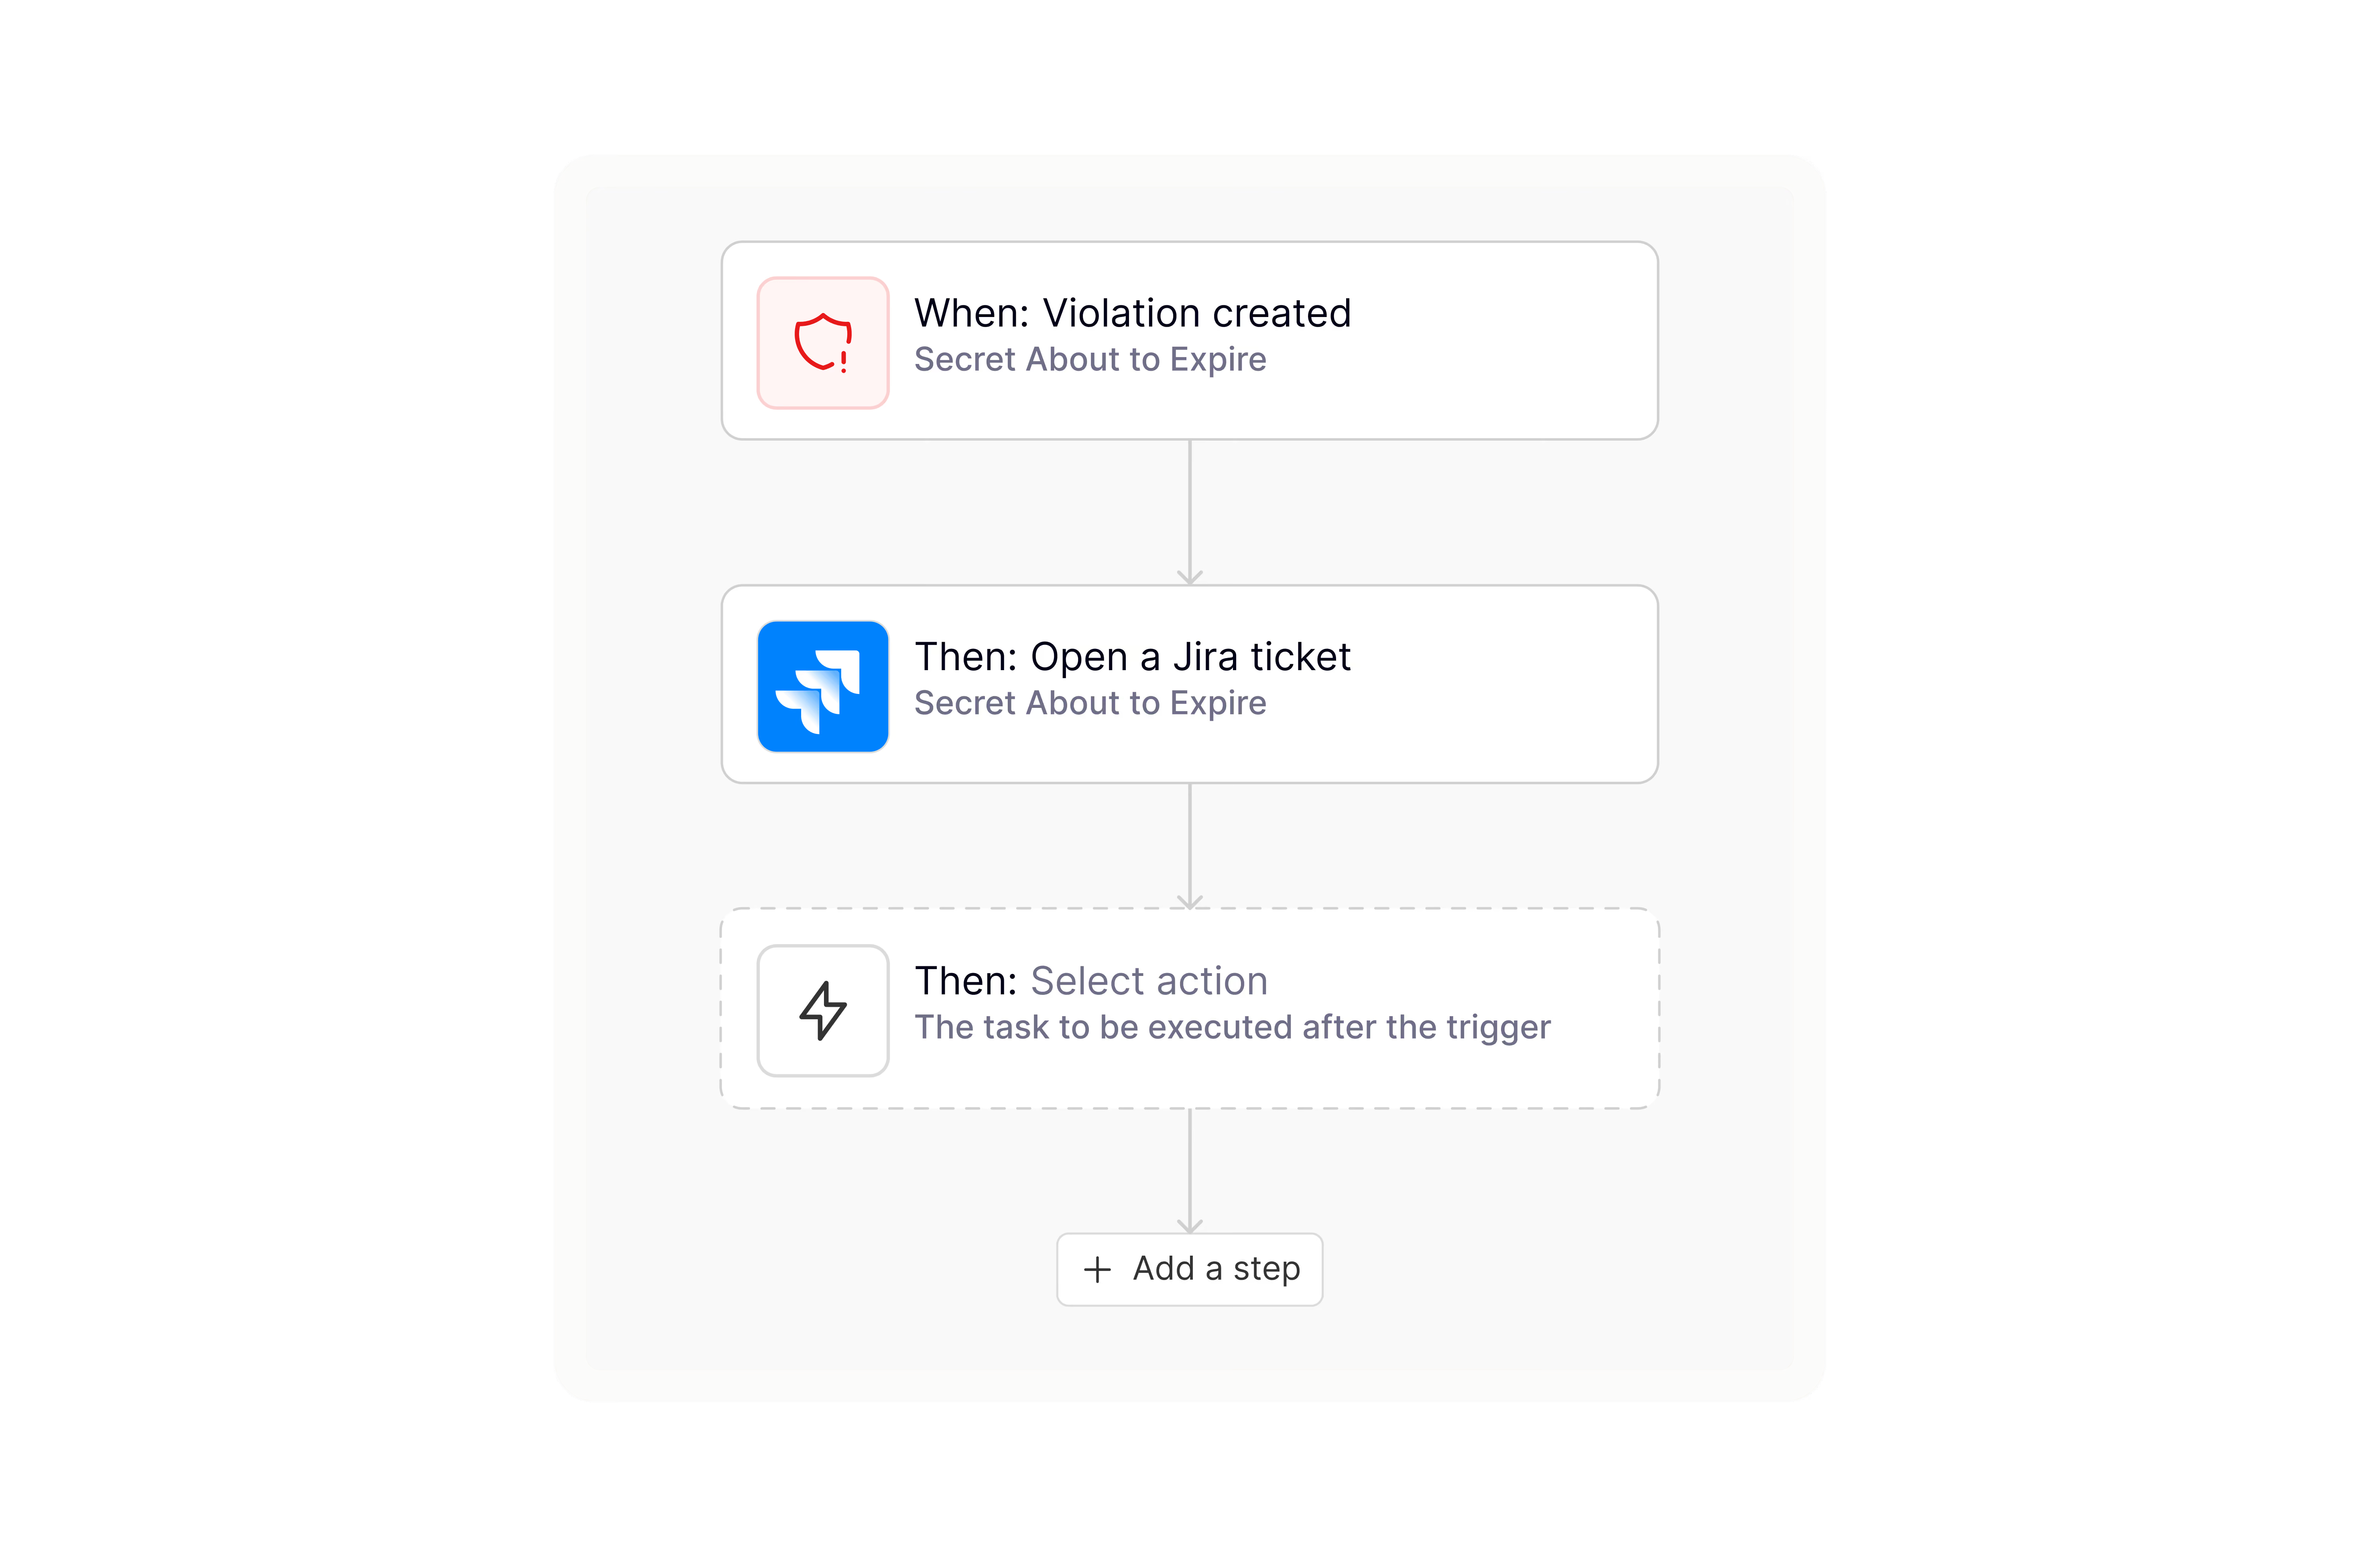
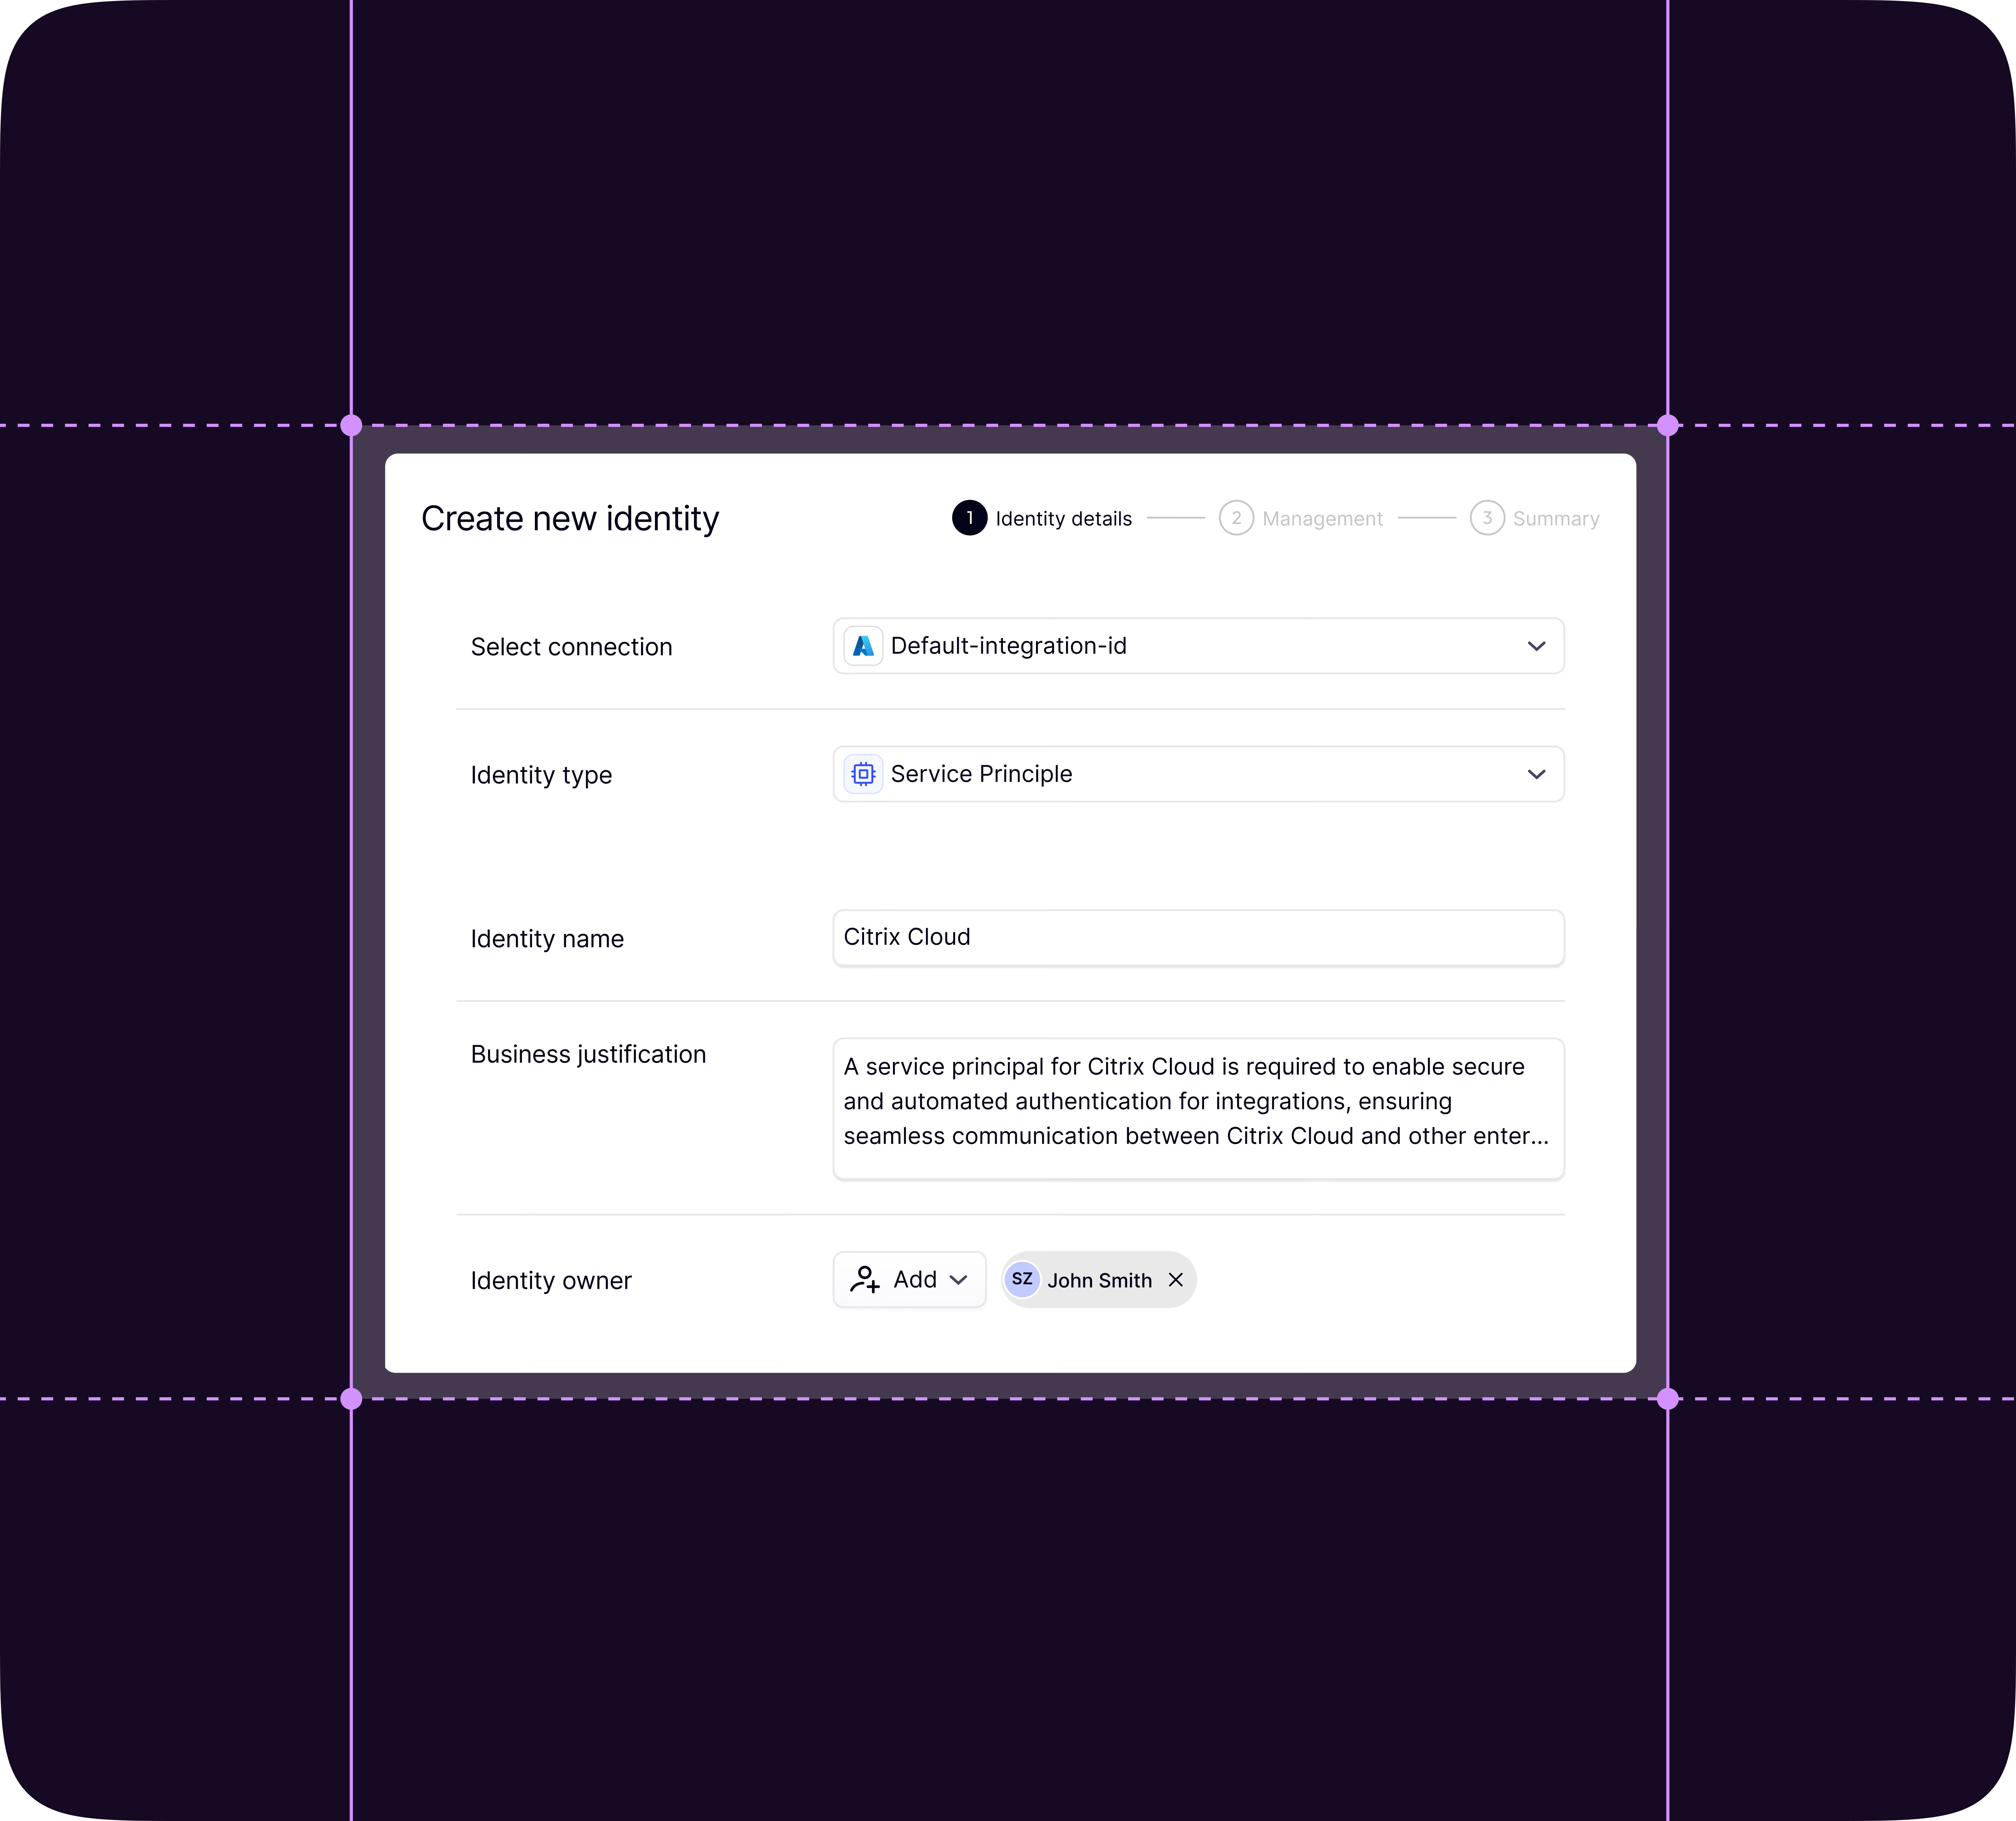
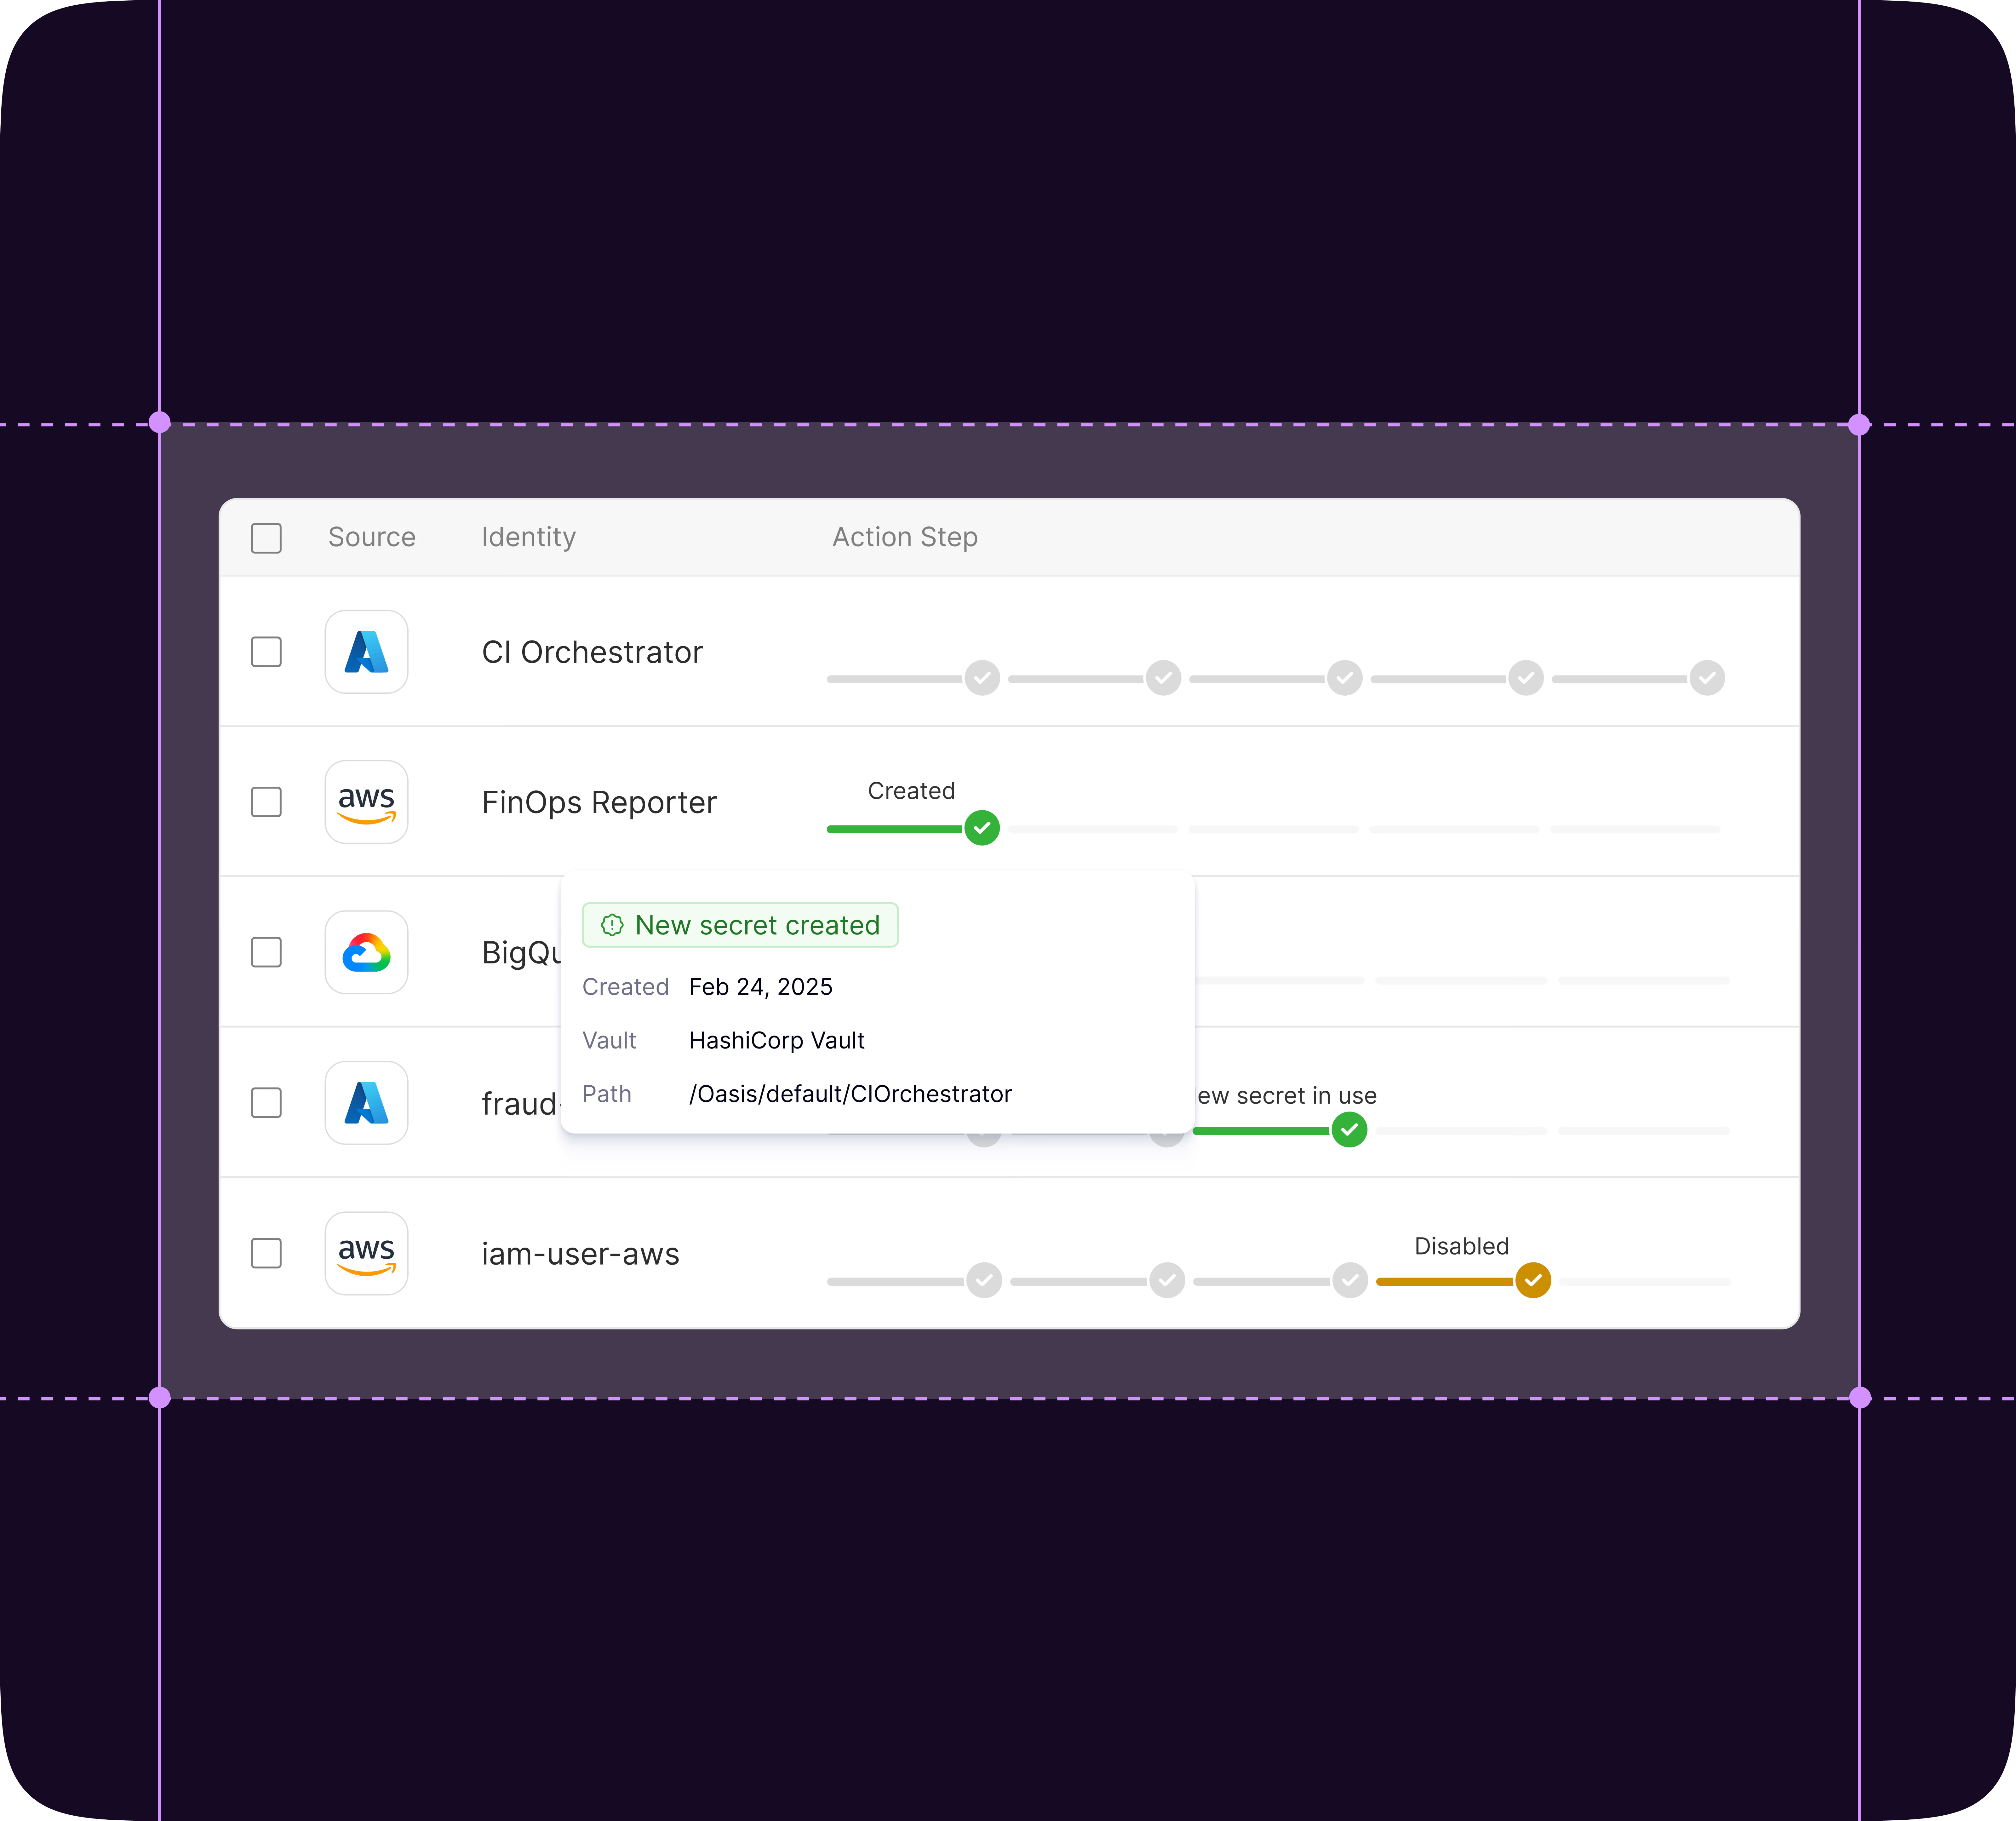
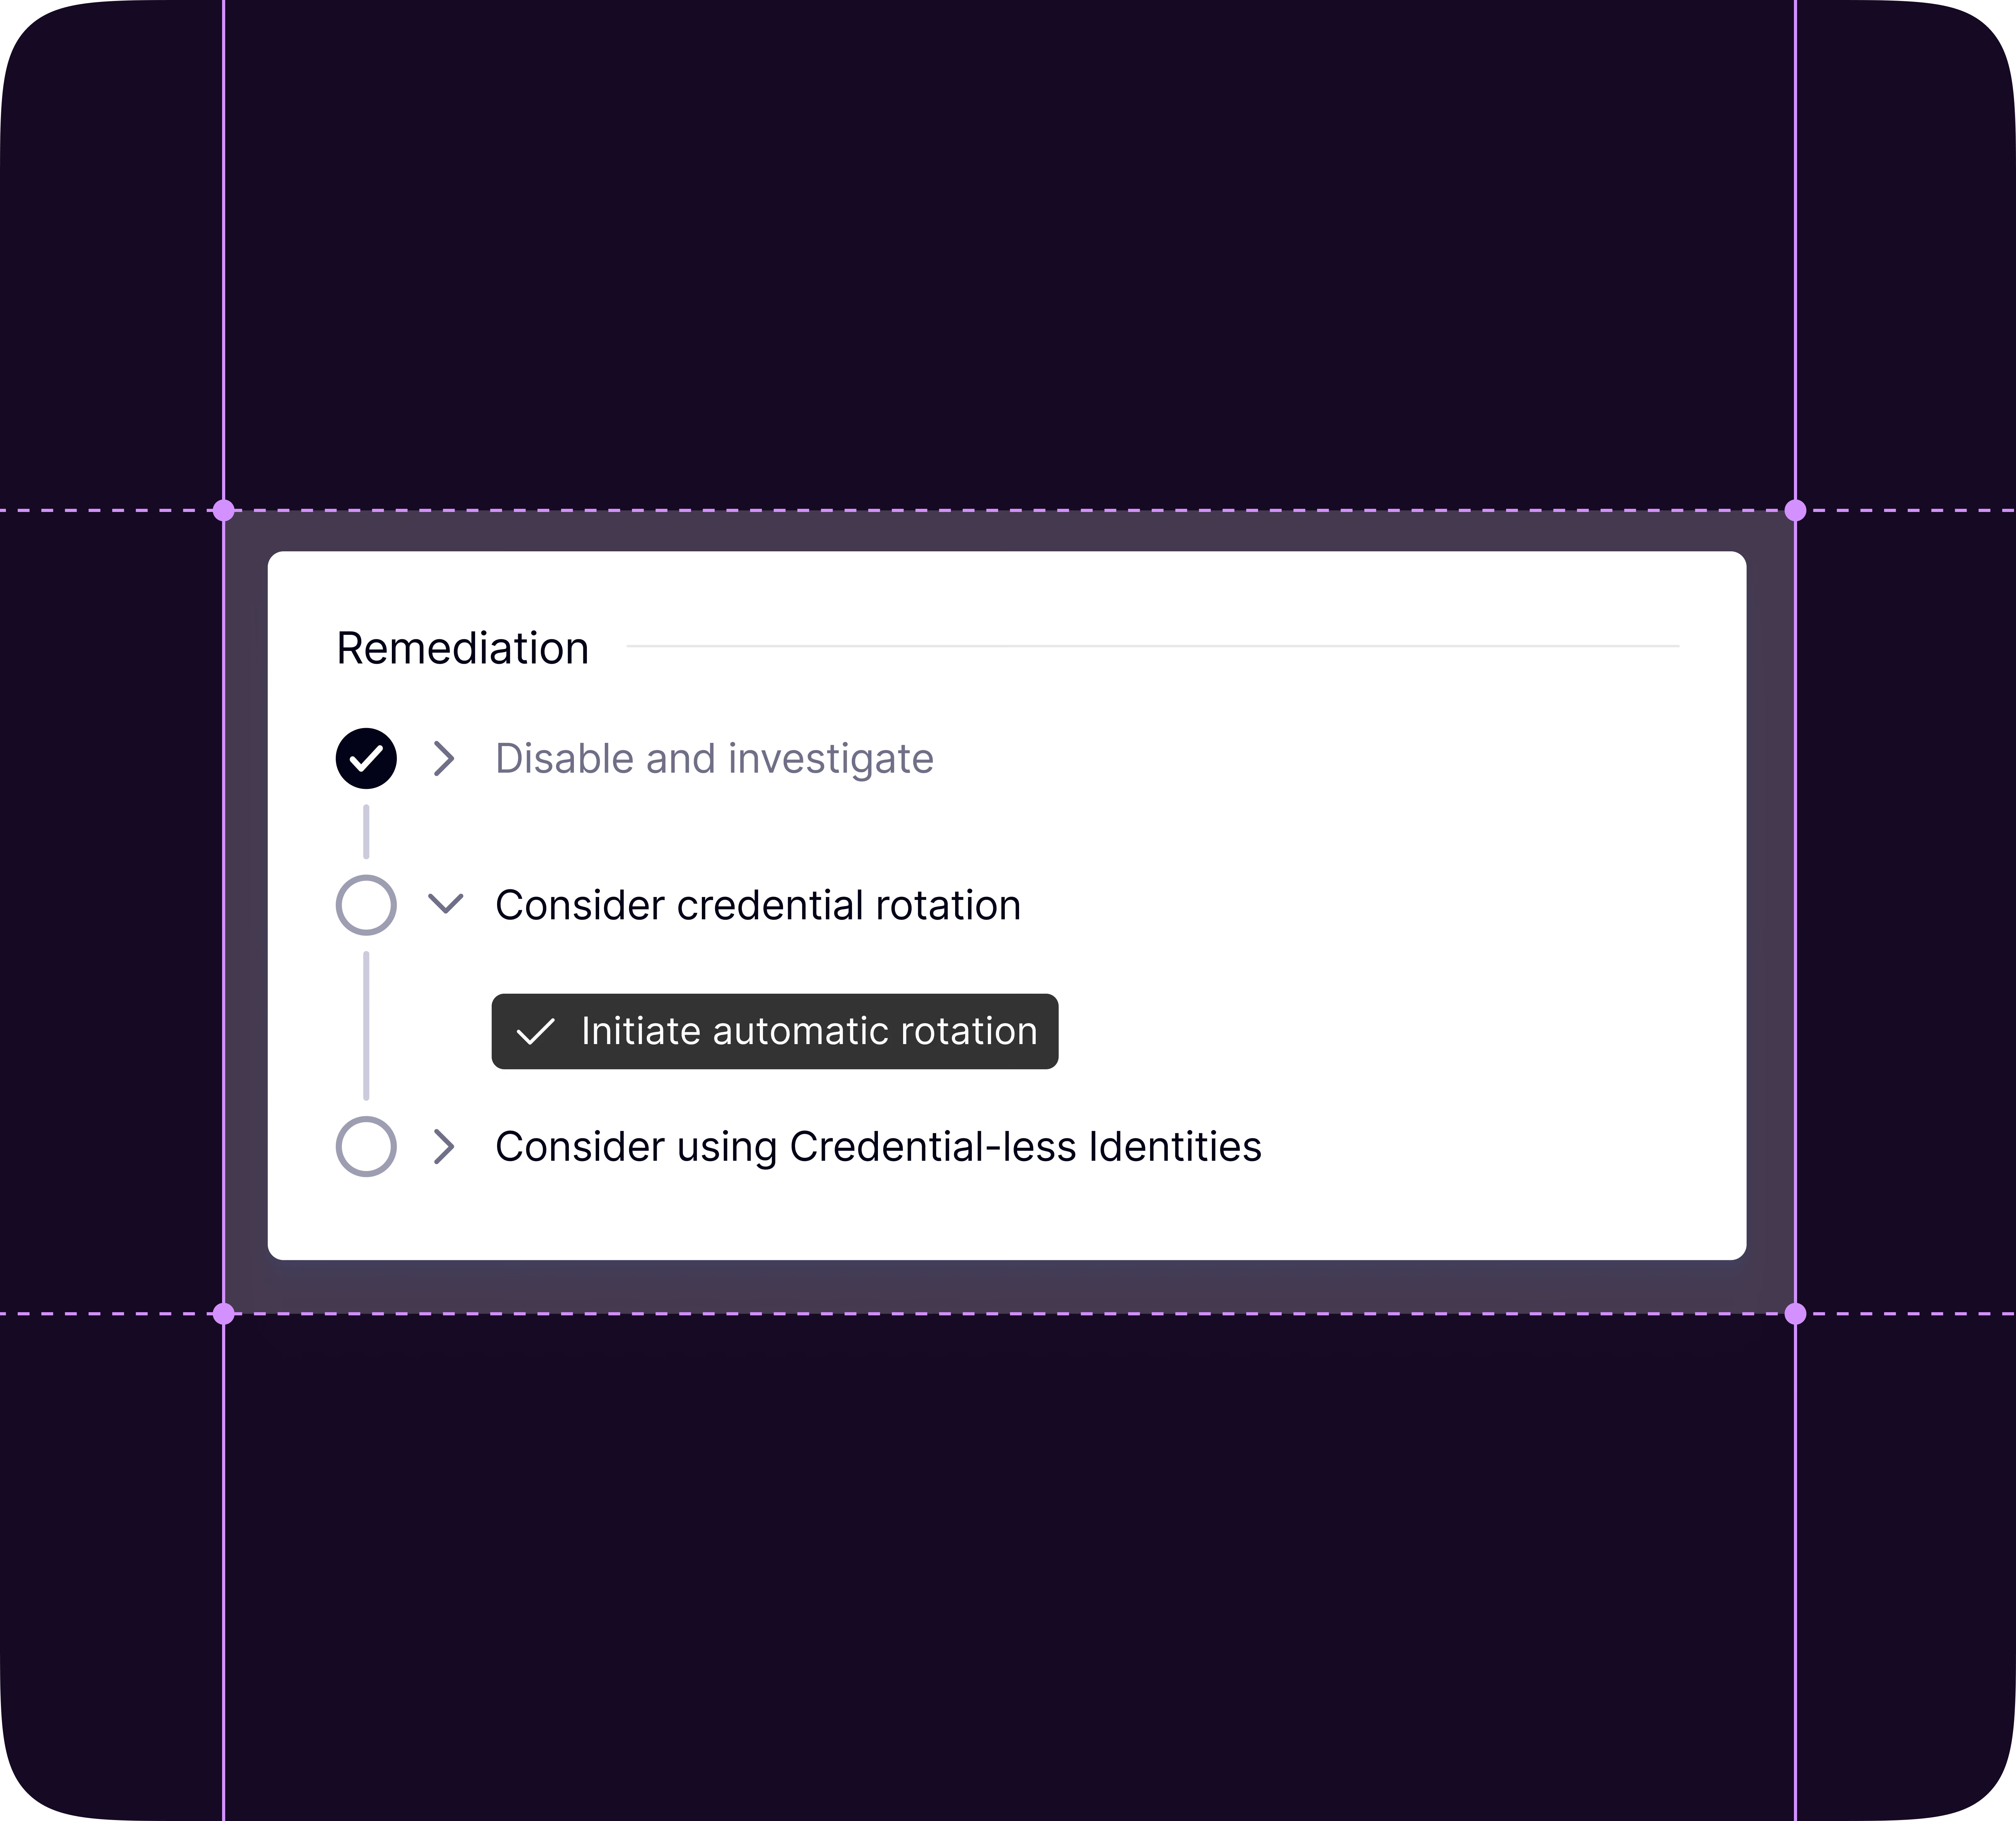
Evaluate every identity against your security policies and rank each gap by privilege, exposure, and the data at stake. Resolve issues with a guided step, a script, or one click, for one identity or hundreds, knowing what depends on it before anything changes. Disable first, restore if needed, and delete only after a grace period.
Govern non-human identities and
agentic access at scale
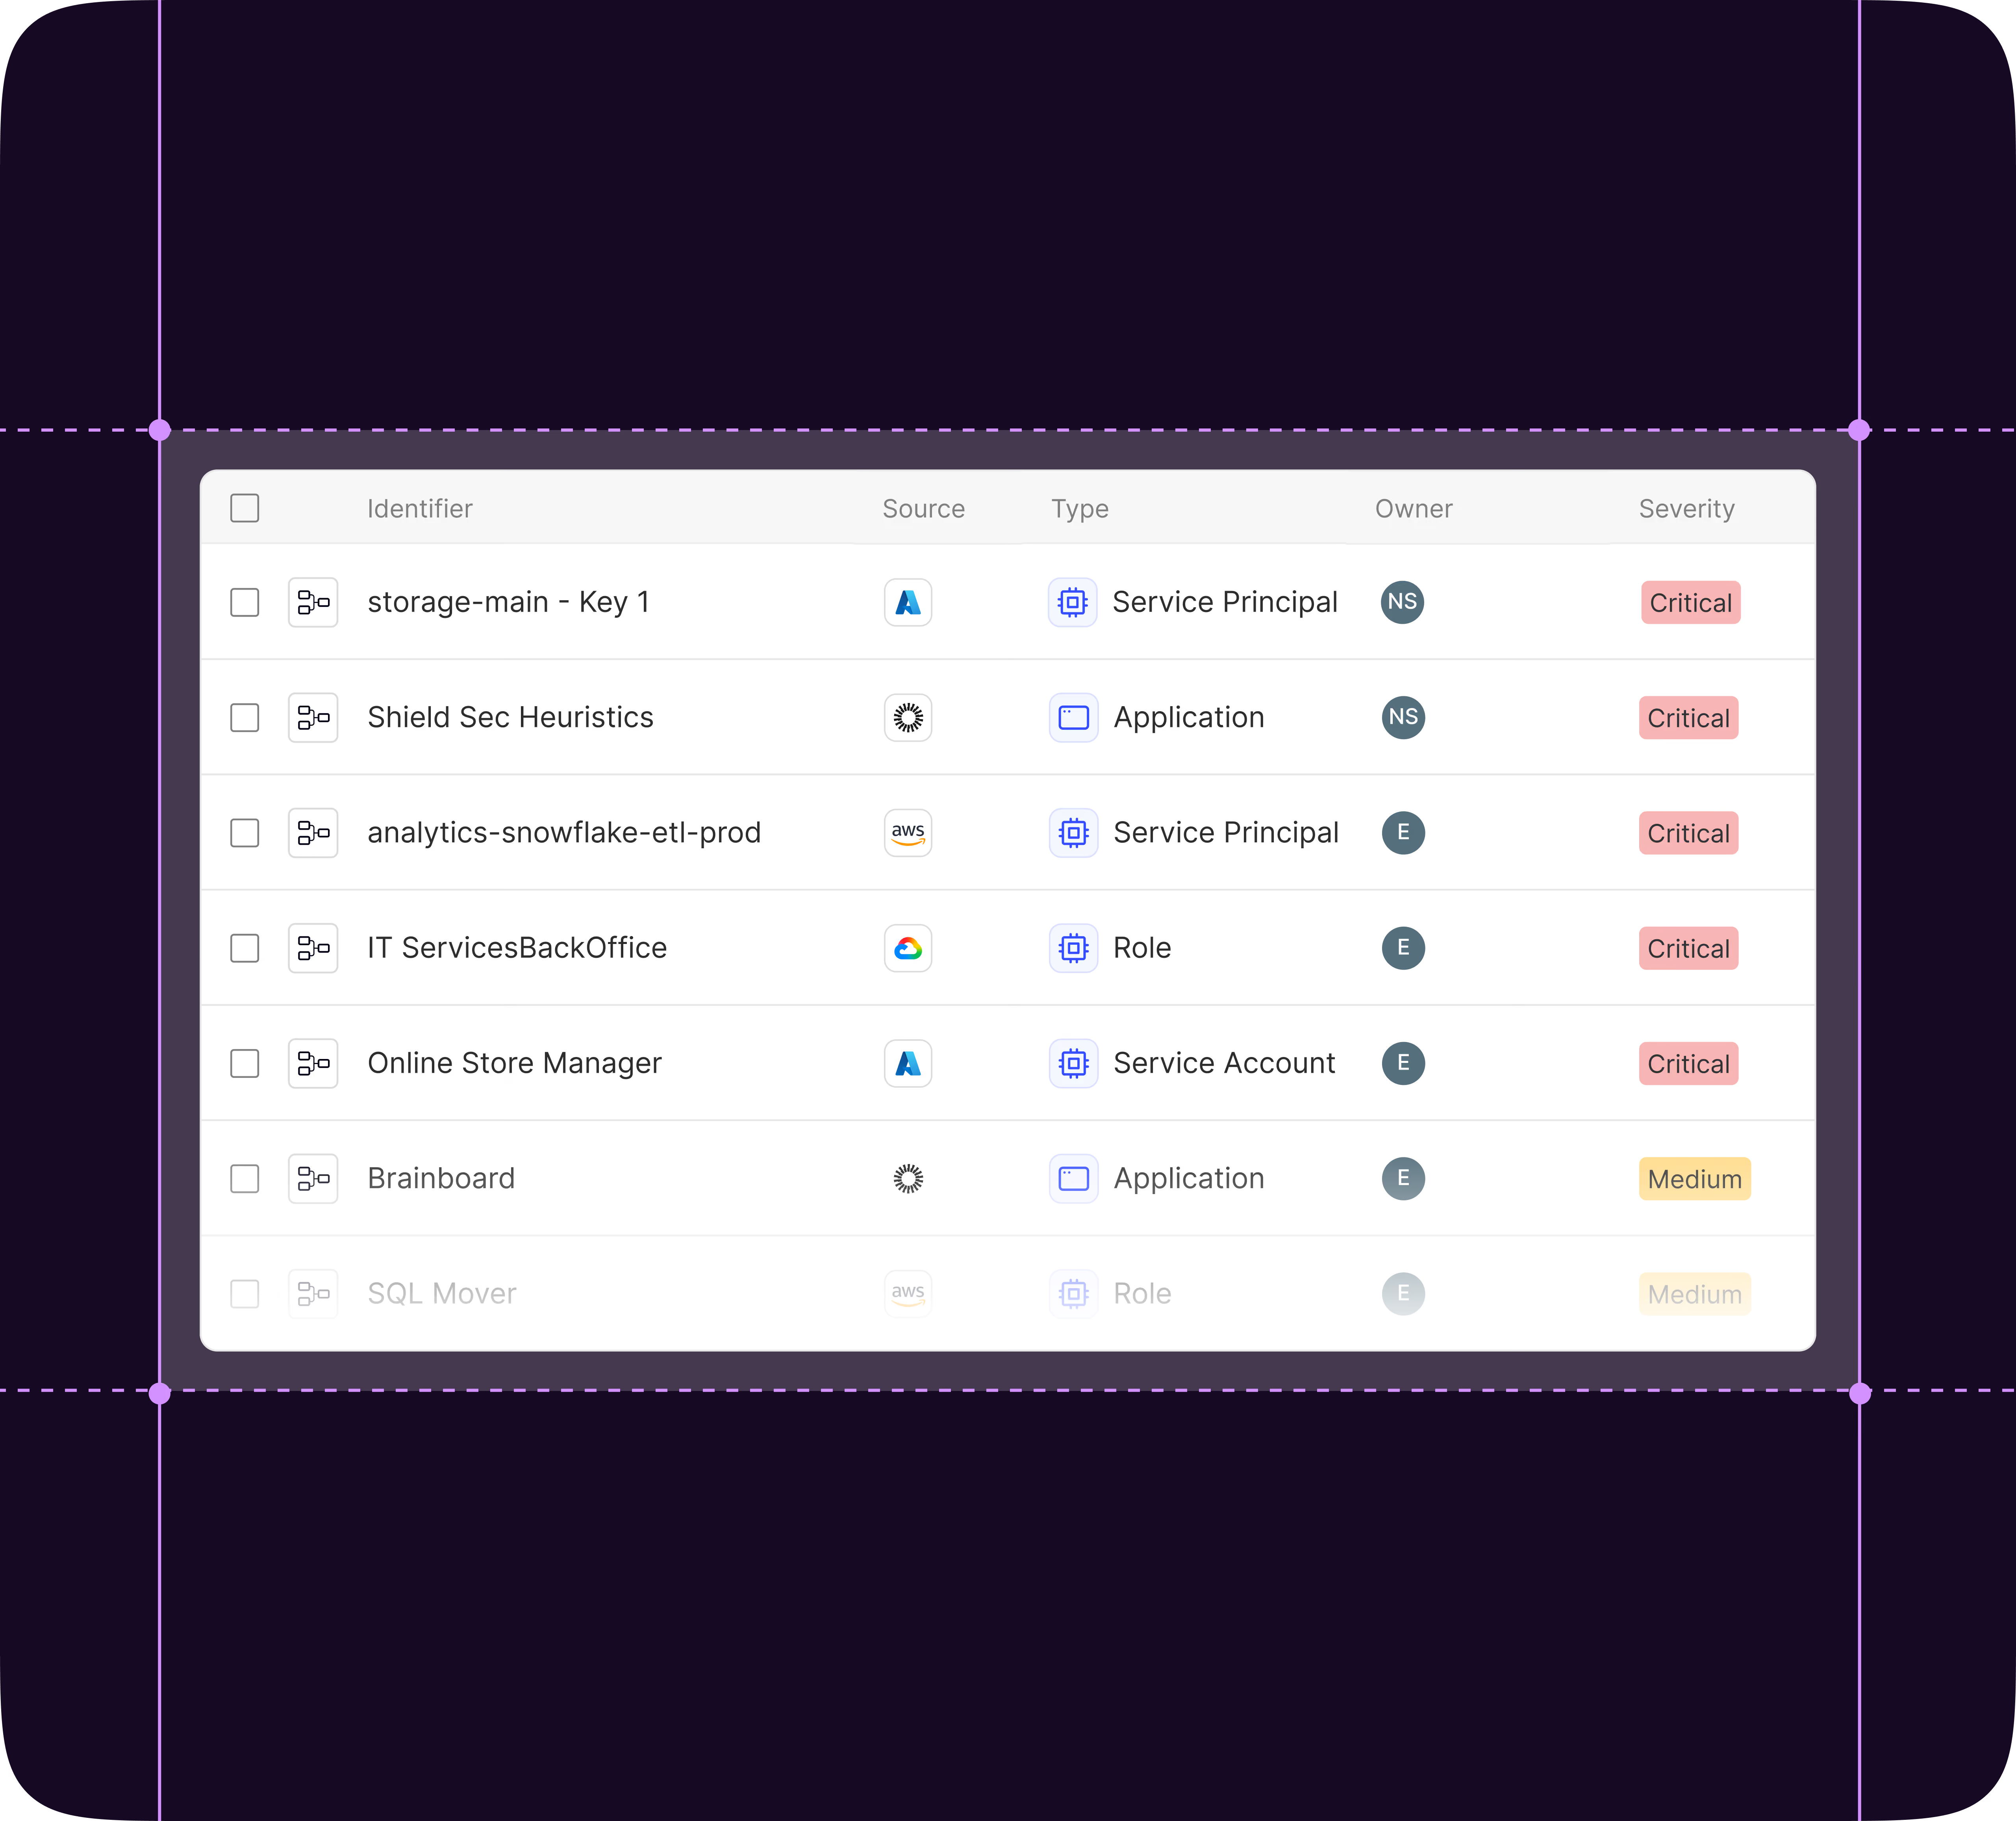
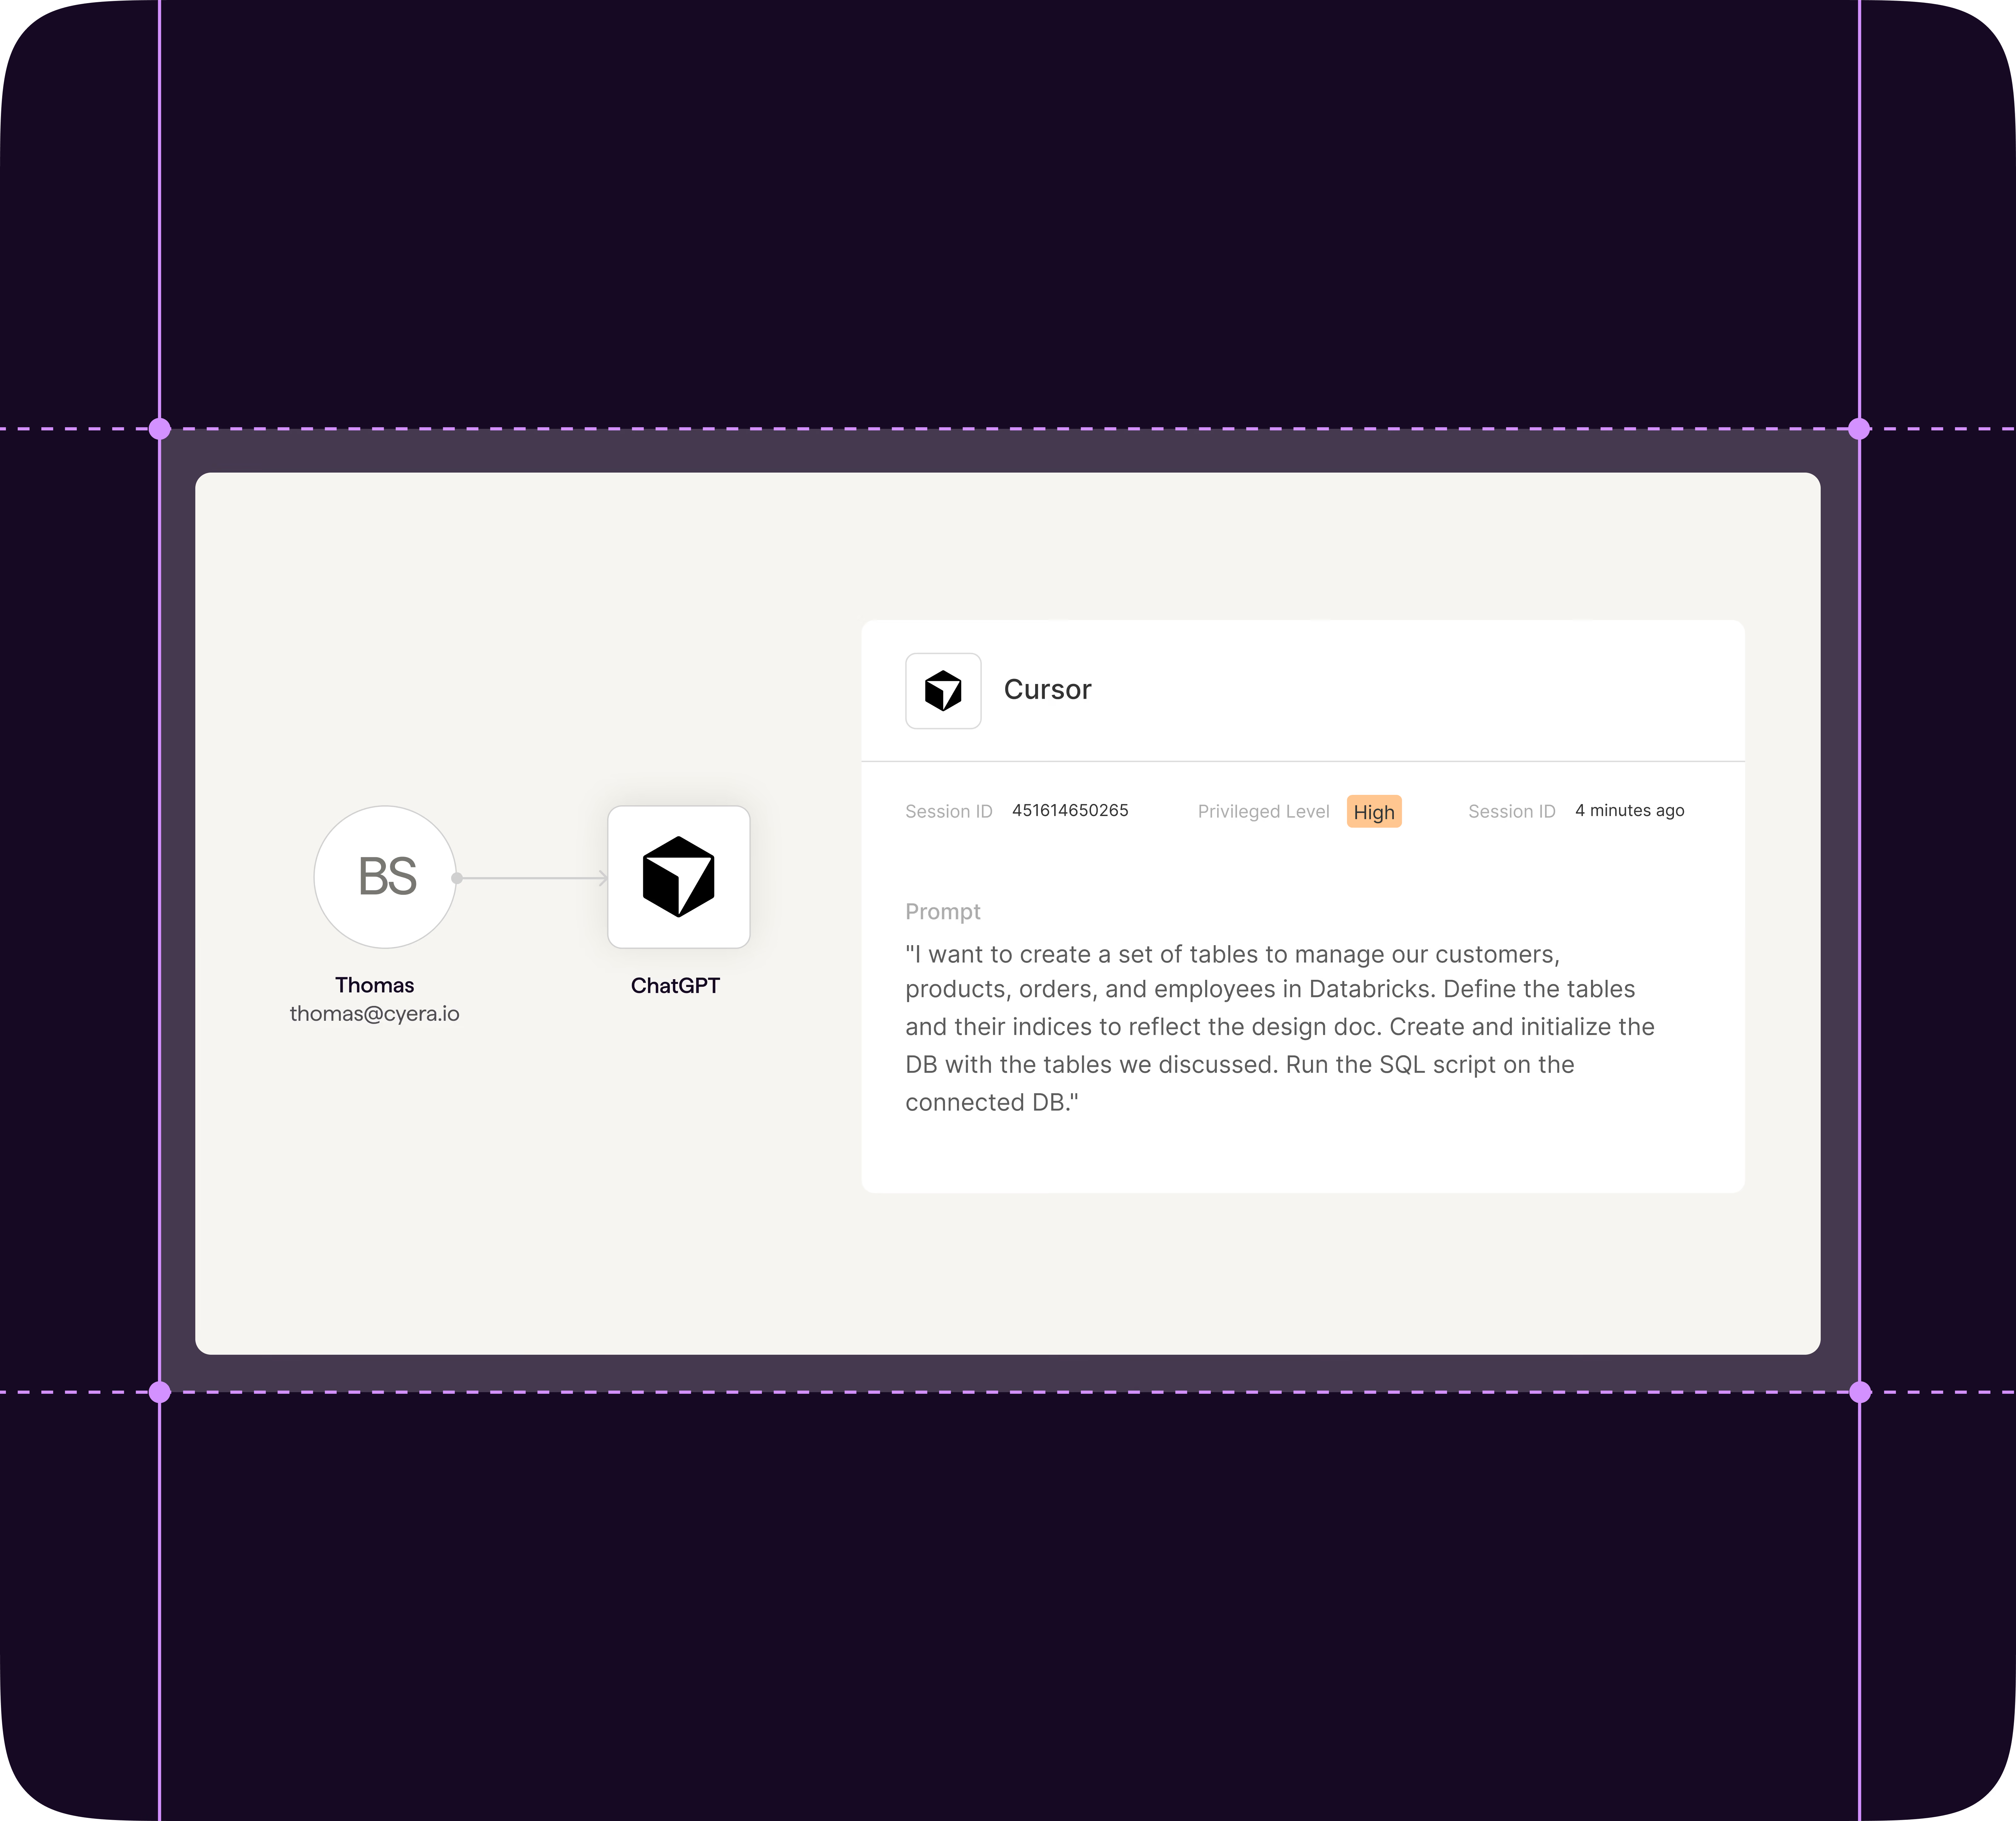
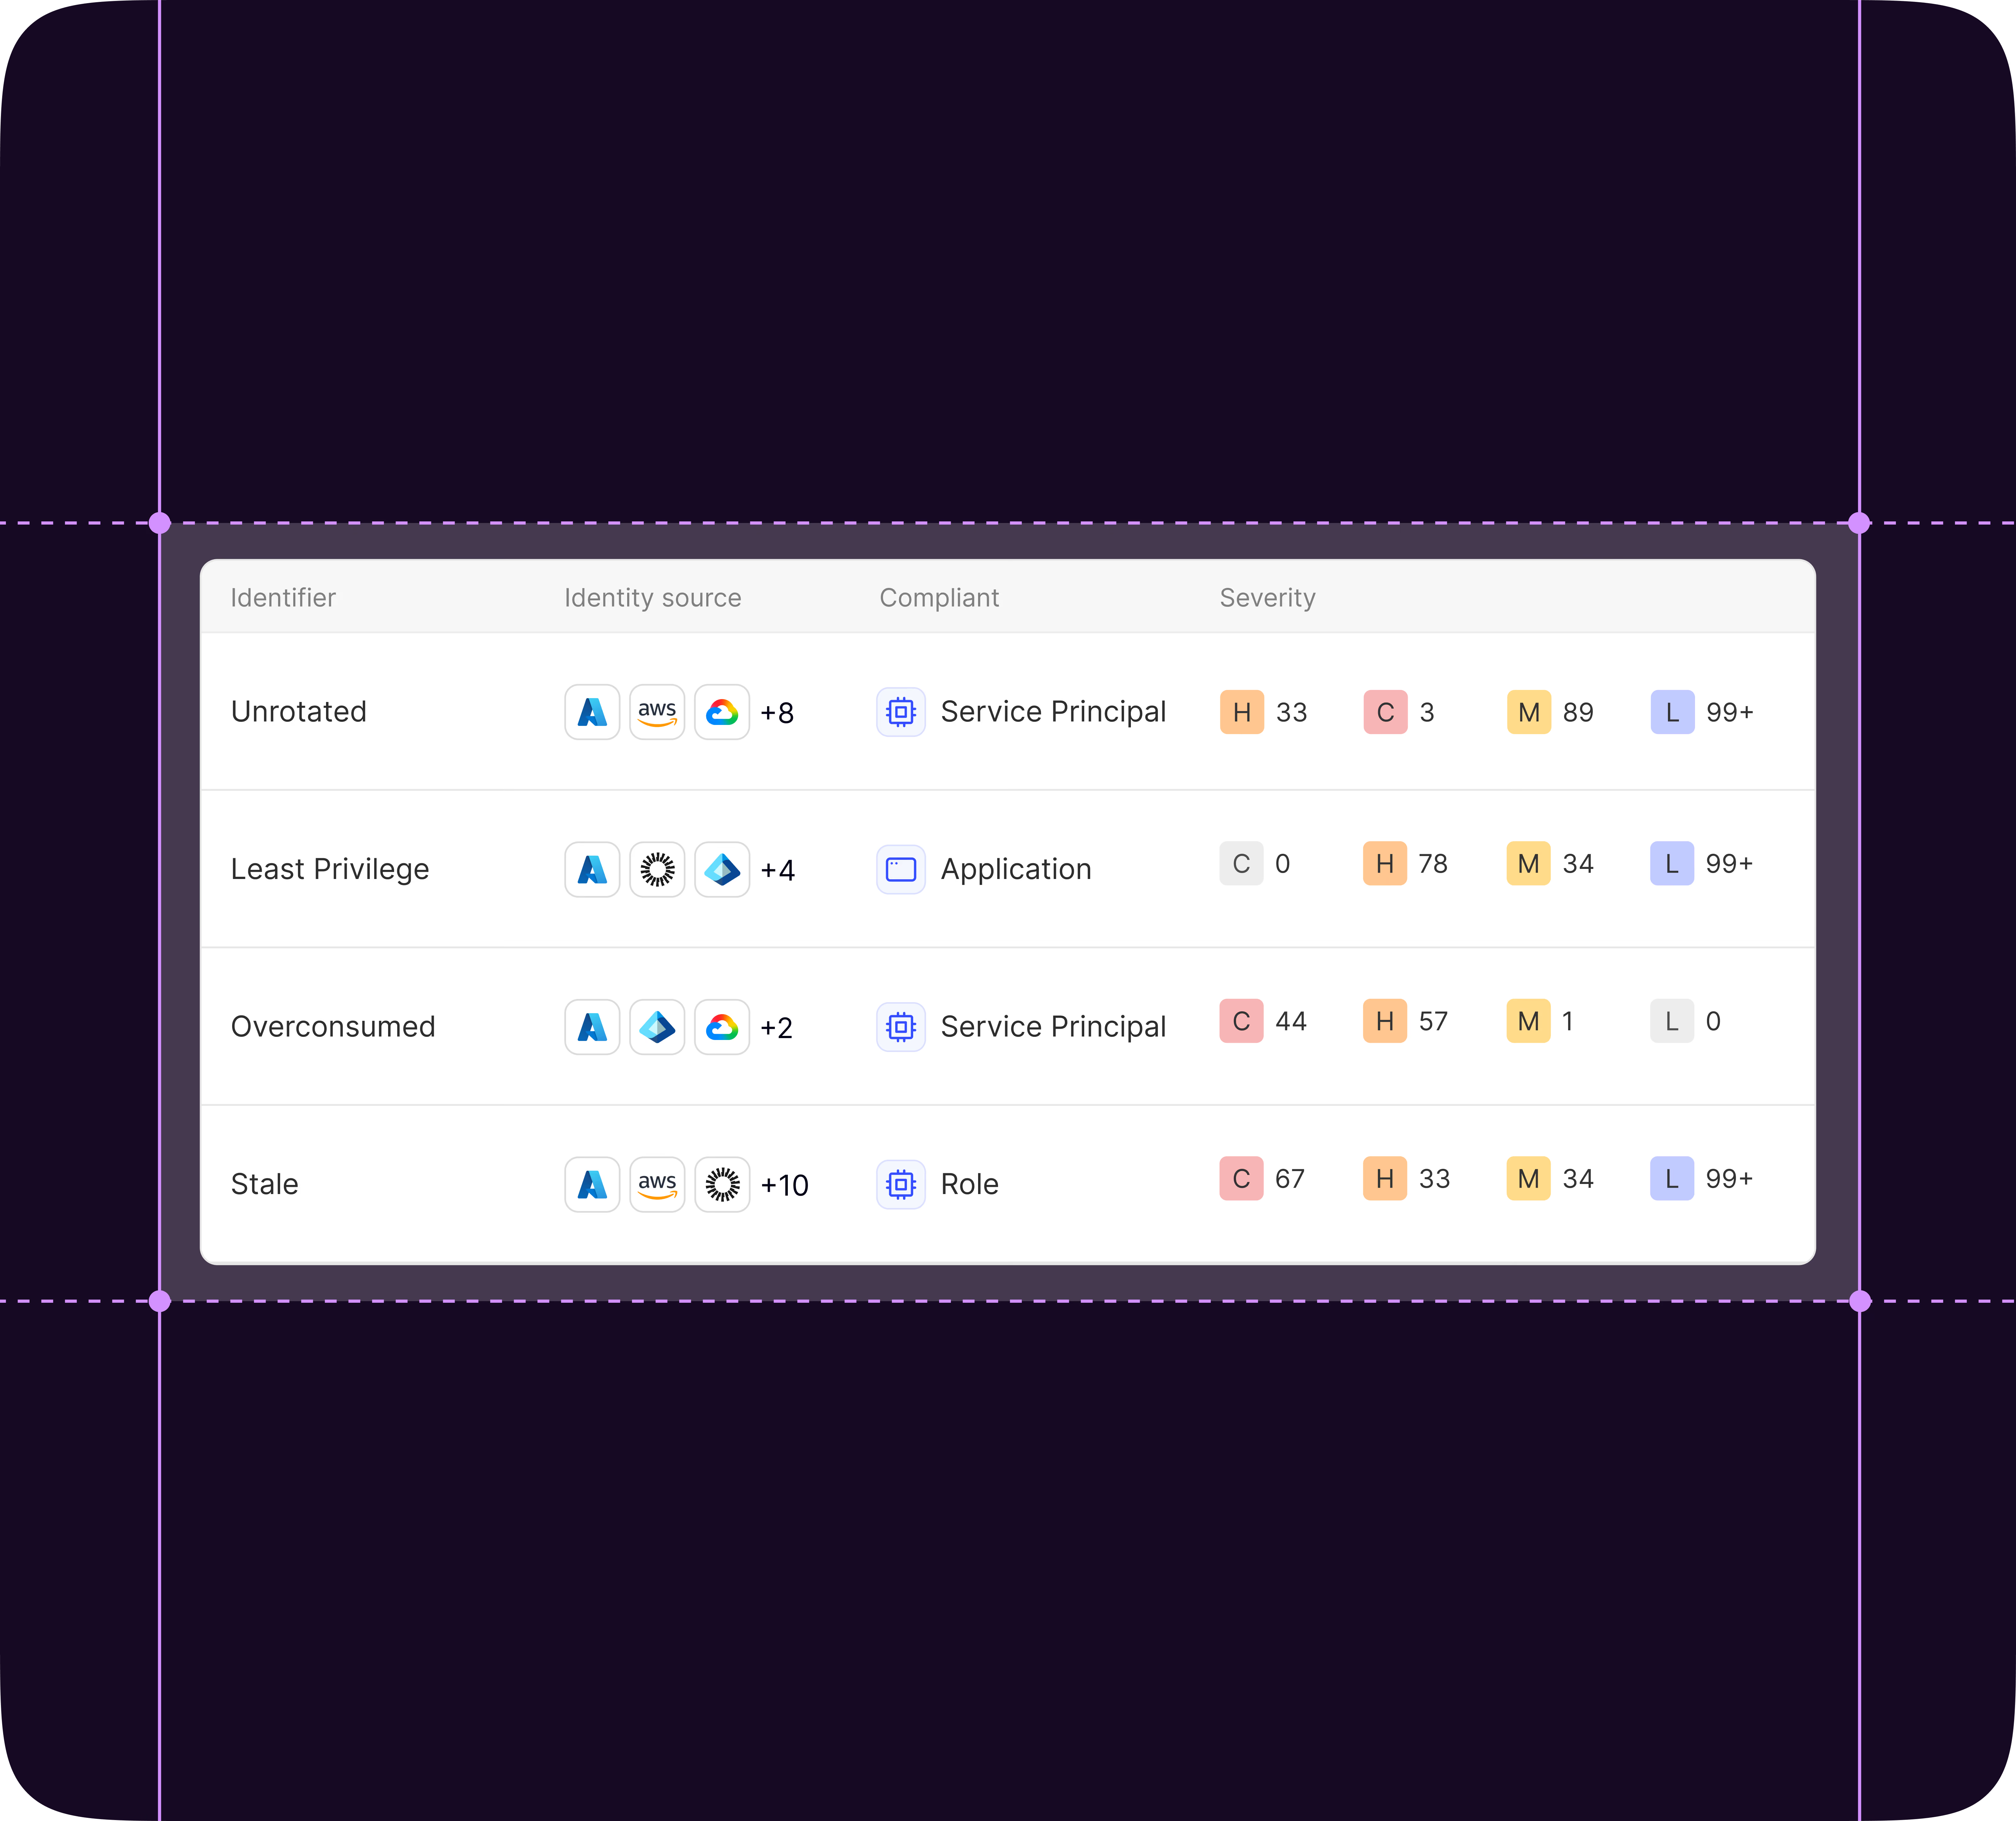
Connect in days. Enforce through
the stack you already own.
Connect through the control plane. Agentless API connectors deliver inventory, ownership, and data context in days. Enforcement then ties into the infrastructure you already run, from identity providers and cloud platforms to vaults and the gateway your AI agents connect through.


Complete security across your agentic estate
Ensure visibility, governance and protection for all AI and agentic tools in your organization


One platform to secure AI - from data to identity to action
At rest, in motion, and in use.
The most intelligent data security control plane
One AI brain to reduce all DLP noise and toil
See every non-human identity. Govern what it can reach.
Secure everything agents can see and do
Get data security at scale, without lifting a finger
Protect your data in minutes
FAQ
A non-human identity (NHI) is how software accesses systems and data. Service accounts, service principals, cloud roles, OAuth apps and managed identities are NHIs, and AI agents run on them. They authenticate with API keys, tokens and certificates, not a person’s login. They outnumber human identities by at least 10 to 1: 2026 research puts the average near 45 to 1, and above 100 to 1 in cloud-native environments (CSA, 2026).
Cyera Identity discovers, governs and secures non-human identities and the AI agents that run on them. It finds every NHI across clouds, on-prem Active Directory, SaaS, CI/CD and vaults, assigns each one an owner, and flags what puts you at risk: stale, overprivileged, unrotated or exposed identities, leaked secrets and identity threats. It manages the full lifecycle: provisioning, rotation, attestation and decommissioning. For AI agents, it grants intent-aware, just-in-time access.
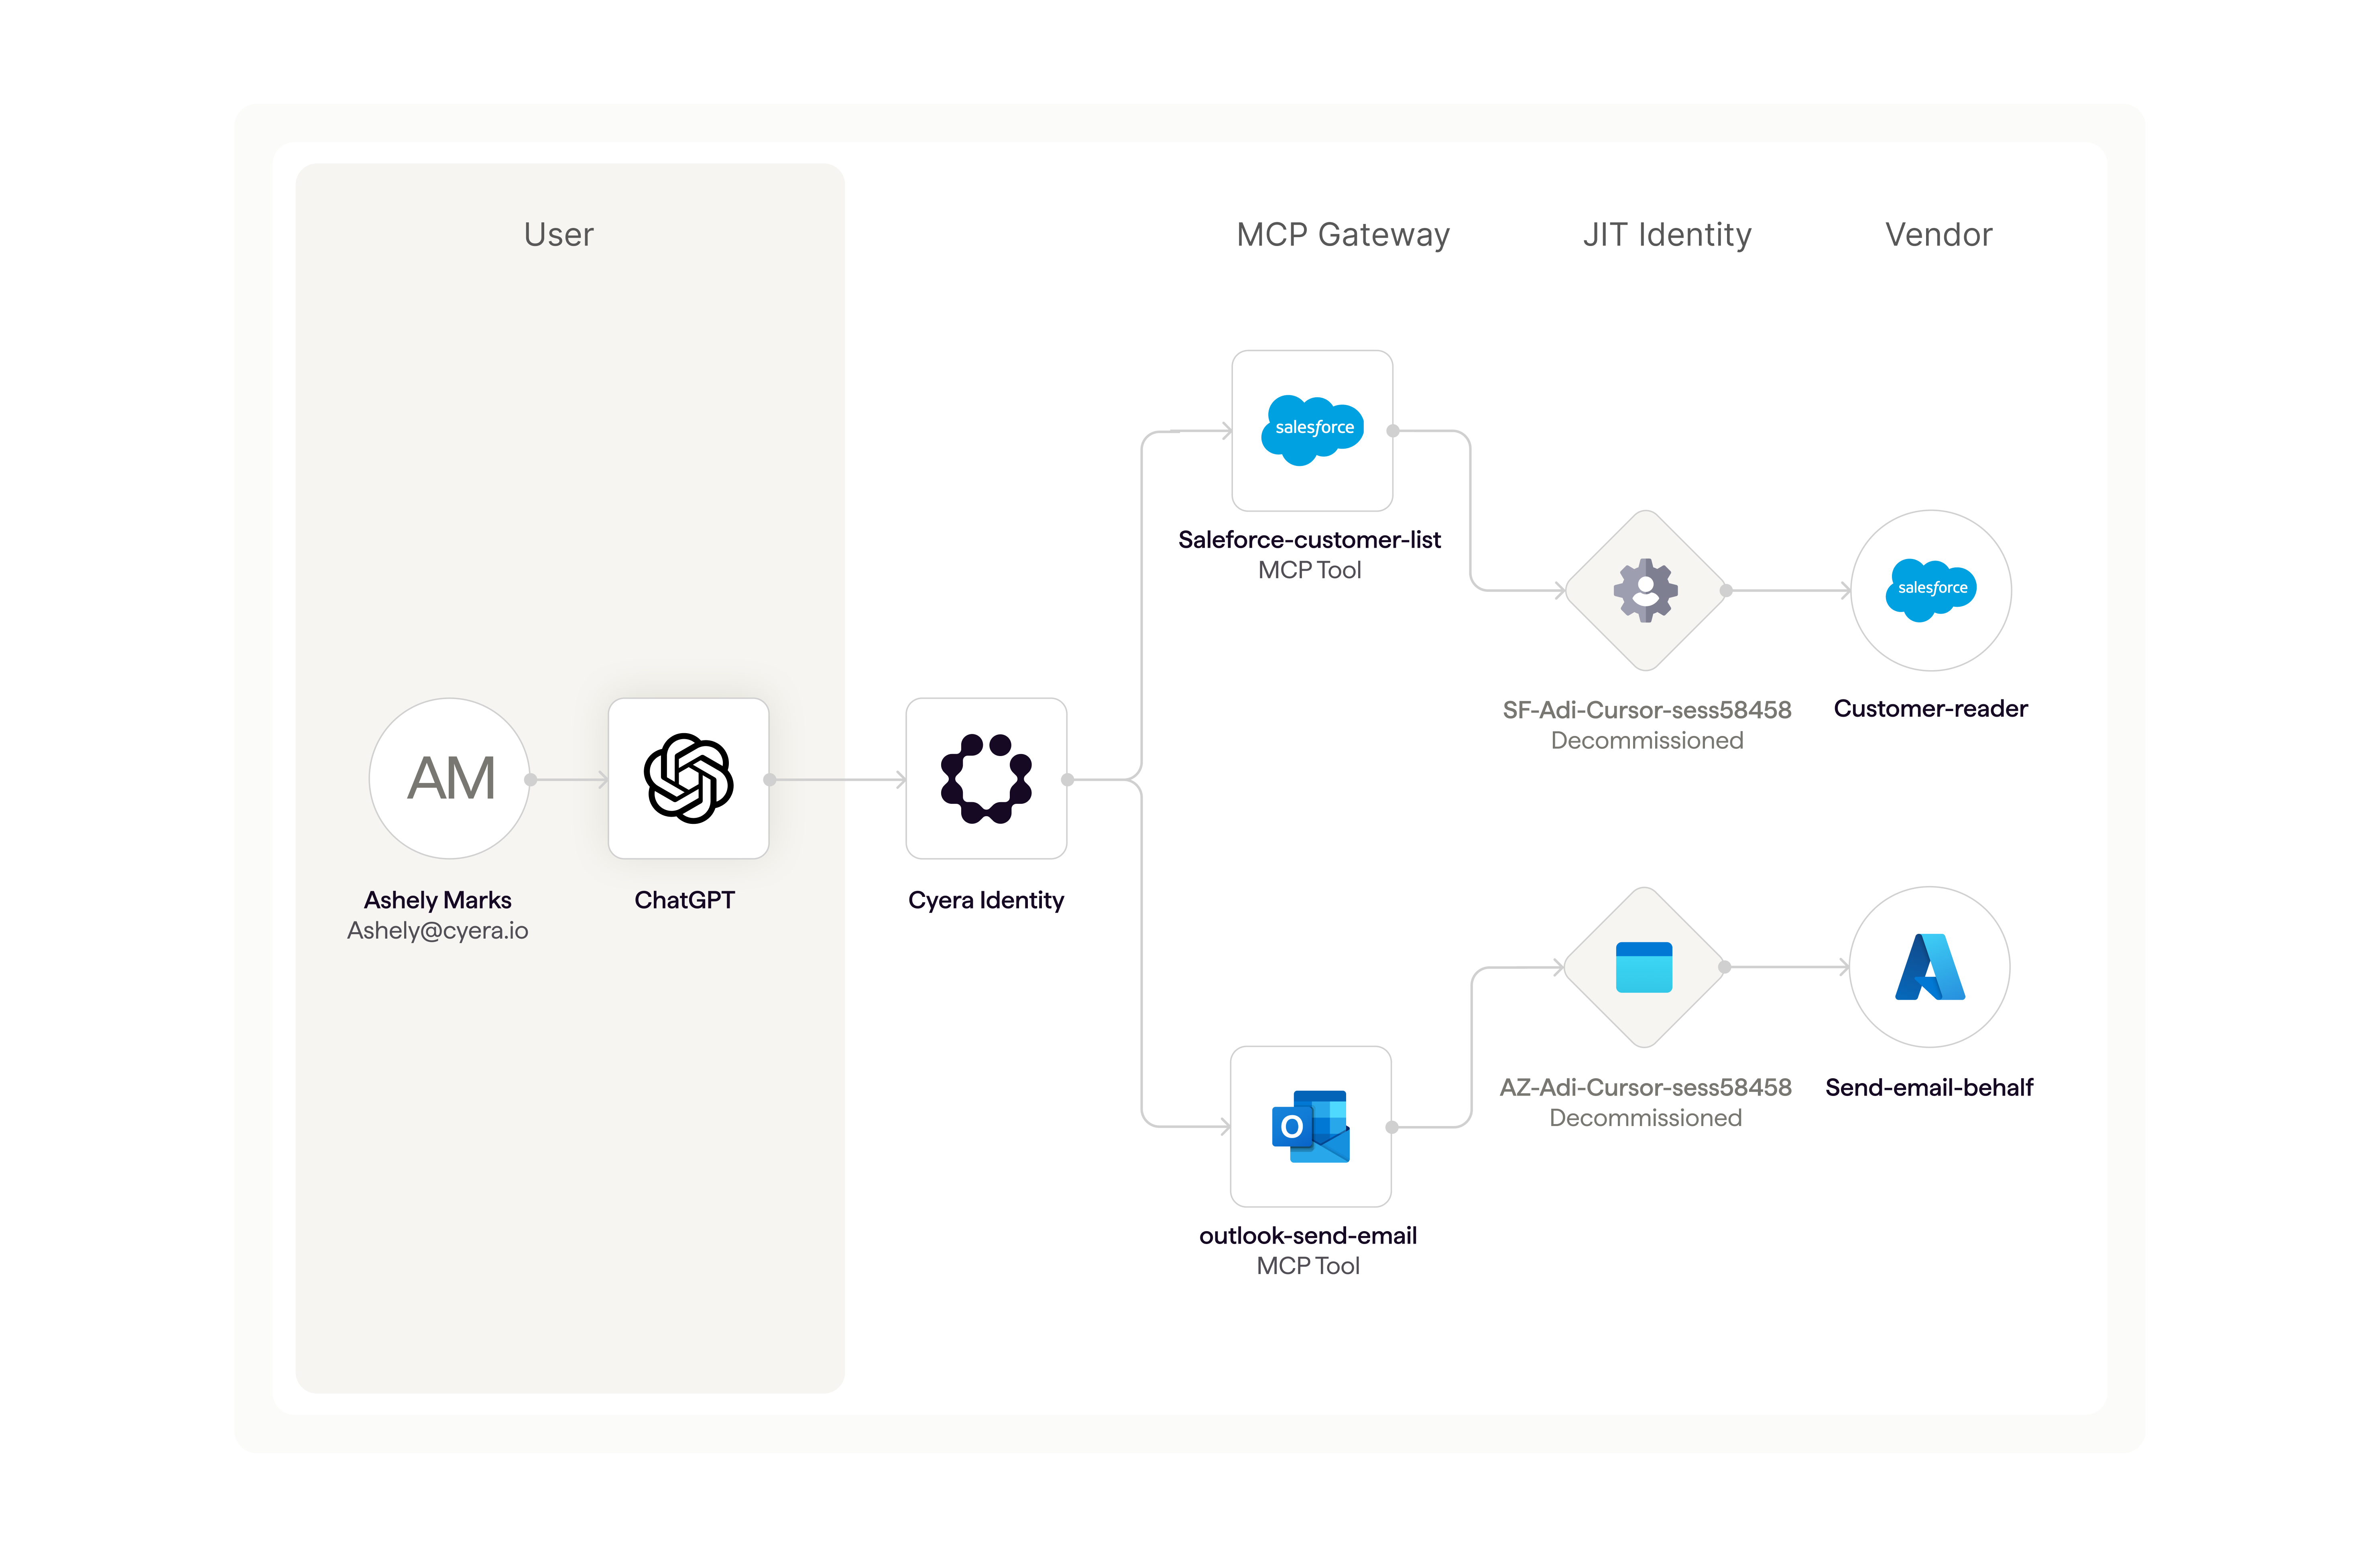
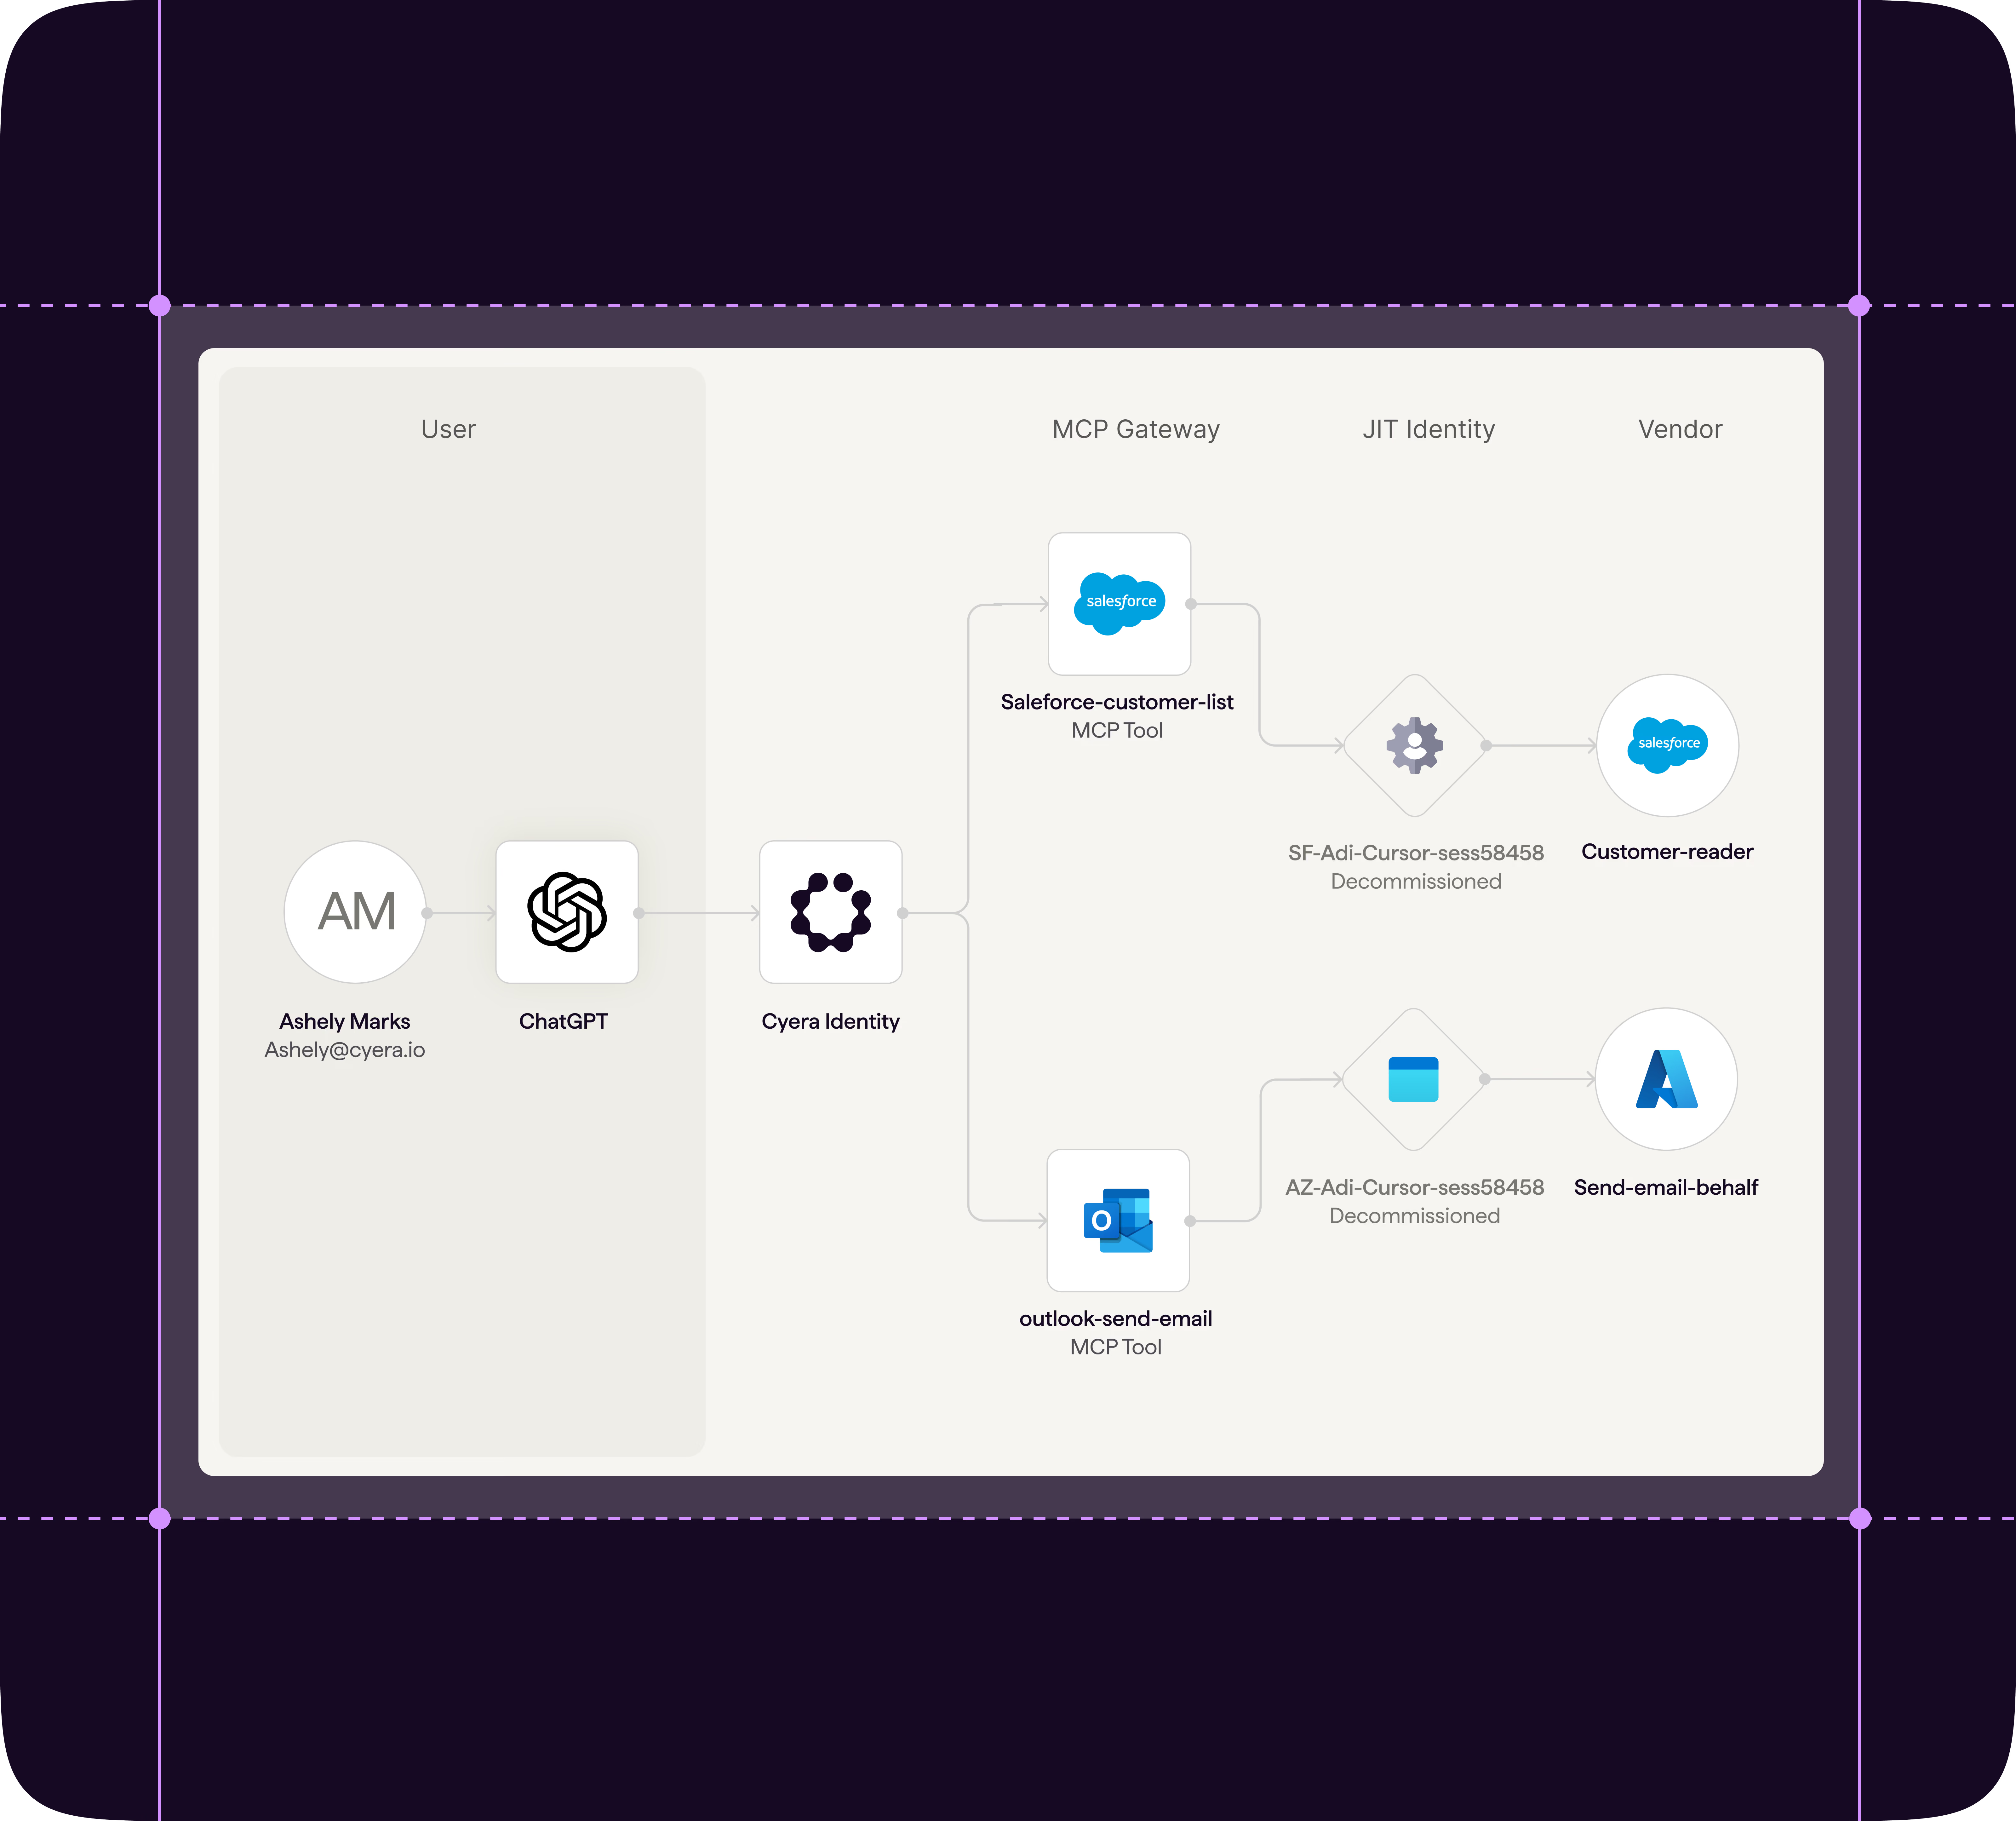
Agents act through non-human identities, so Cyera Identity secures both. It discovers the identities your agents run as and surfaces shadow AI. With intent-aware, just-in-time access, each request receives a short-lived identity scoped to the task and your policies, and Cyera Identity revokes it the moment the task ends.
They were built for different problems. IGA governs people. PAM protects the privileged accounts it already knows about. Most non-human identities sit outside both. Cyera Identity discovers them, shows who owns each one and what it can reach, and runs alongside the IGA and PAM you already own, including a view of which identities your PAM doesn’t manage yet.
No. Cyera Identity works with the vaults you already run. It maps secrets across them, PAM vaults included, and links each secret to the identities that use it, without storing a single secret value. It rotates cloud credentials into Azure Key Vault, AWS Secrets Manager, GCP Secret Manager, HashiCorp Vault and CyberArk, and retires the old secret only after usage confirms every consumer has moved to the new one.
An identity’s risk is defined by what it can reach. A stale service account with access to a test bucket is a cleanup task; the same account with access to customer payment data is a breach path. Without data context, both look the same.