Herausforderungen
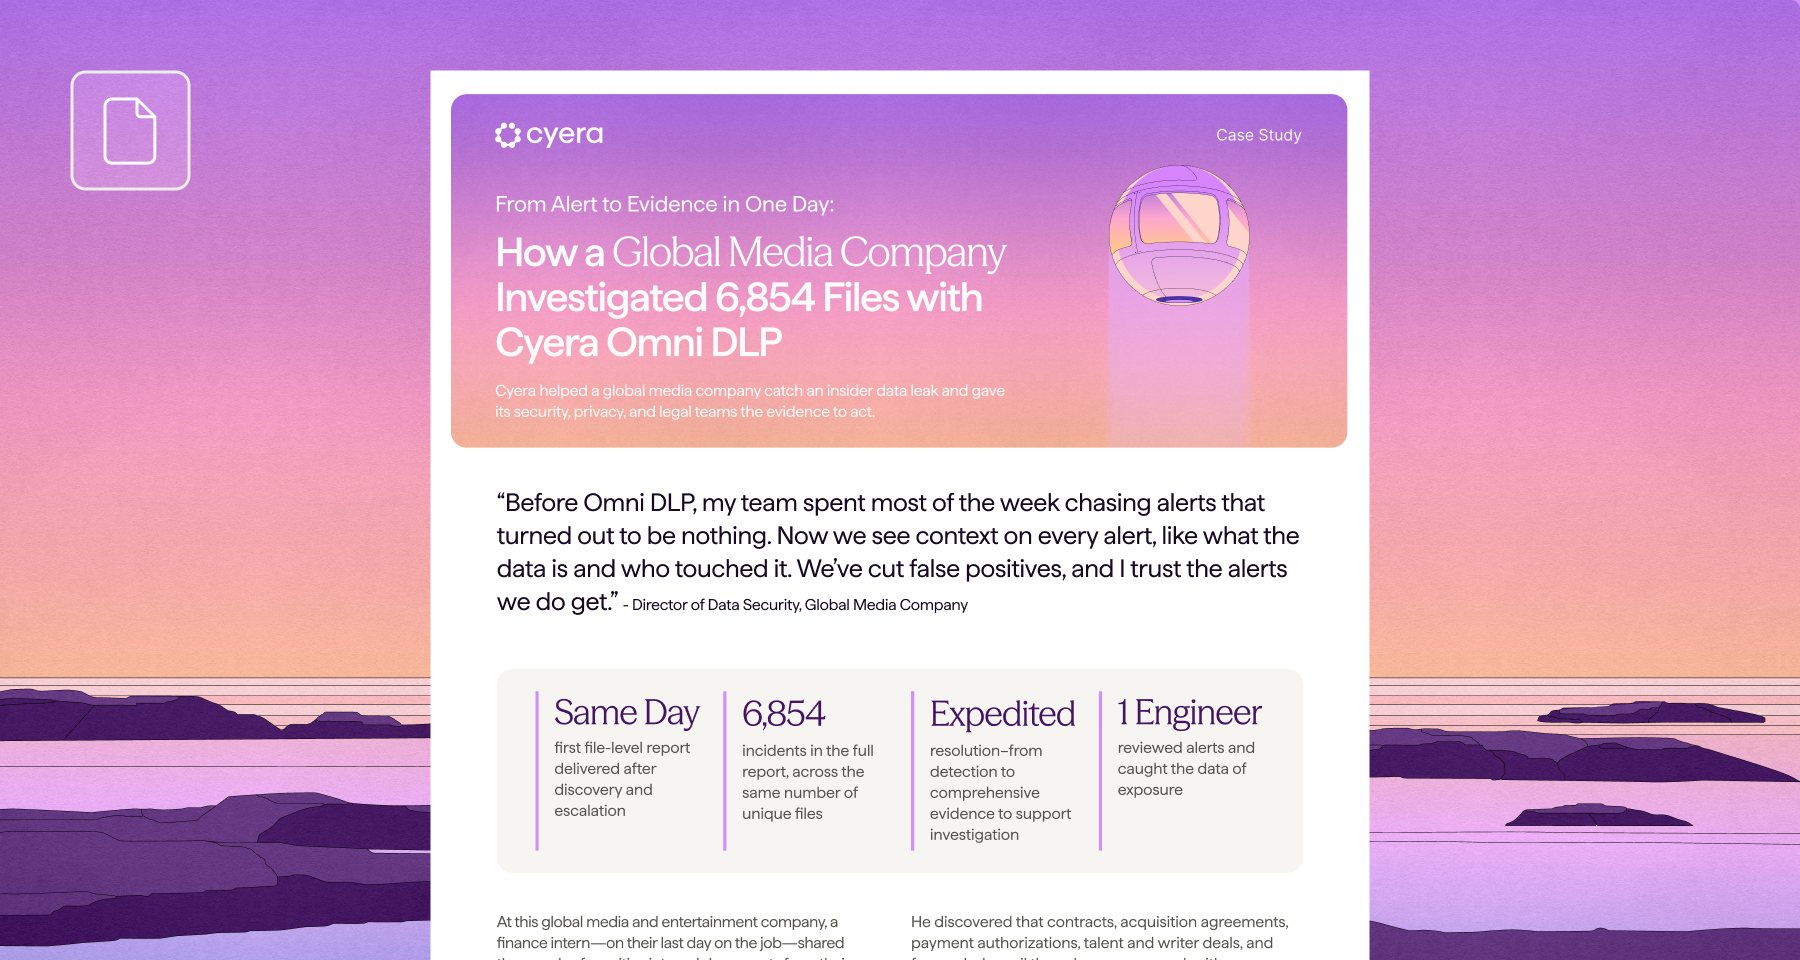
At a global media and entertainment company, a finance intern on their last day shared thousands of sensitive files from their corporate OneDrive to a personal external domain. They used a second destination in an apparent attempt to hide it. The files included contracts, acquisition agreements, payment authorizations, and talent and writer deals, many with PII and financial data. The activity was easy to miss because the files were OneDrive shares rather than email attachments, and the user had legitimate reasons to access many of the folders. The team needed to know what data had left, who was affected, what the user could access, and what they had done beforehand.
Lösung
The company’s data security engineer spotted the incident in the Omni DLP queue. Cyera’s AI-powered severity rating, using business context like identity, data sensitivity, and exposure conditions, flagged it as a real event. From there, the team combined three layers of Cyera: Omni DLP turned alerts into a file-level report, DSPM revealed what sensitive data was in each file, and Access Trail uncovered the user’s earlier behavior. The investigation ran on Cyera Omni DLP, DSPM, and Access Trail, in one unified console.
Ergebnisse
One engineer caught the incident, and the first file-level report was delivered the same day it was escalated. The full report covered 6,854 incidents across 6,854 unique files, which made clear that a single user was responsible. Cyera analysts walked the team through the findings in a formal Incident Materiality Assessment, and the security operations center, legal, and privacy teams used the evidence to act.