Cyera Identity
Securing access in the agentic enterprise.
Your AI program moves at the speed of your identity governance
+500%
growth in non-human identities across the Fortune 500, in six months.
40%
of enterprises will demote or decommission their AI agents because of governance gaps.
9/10
of agentic actions have no observable intent.
Context that drives action,
enforced at every point.
From non-human identity governance to real-time enforcement.
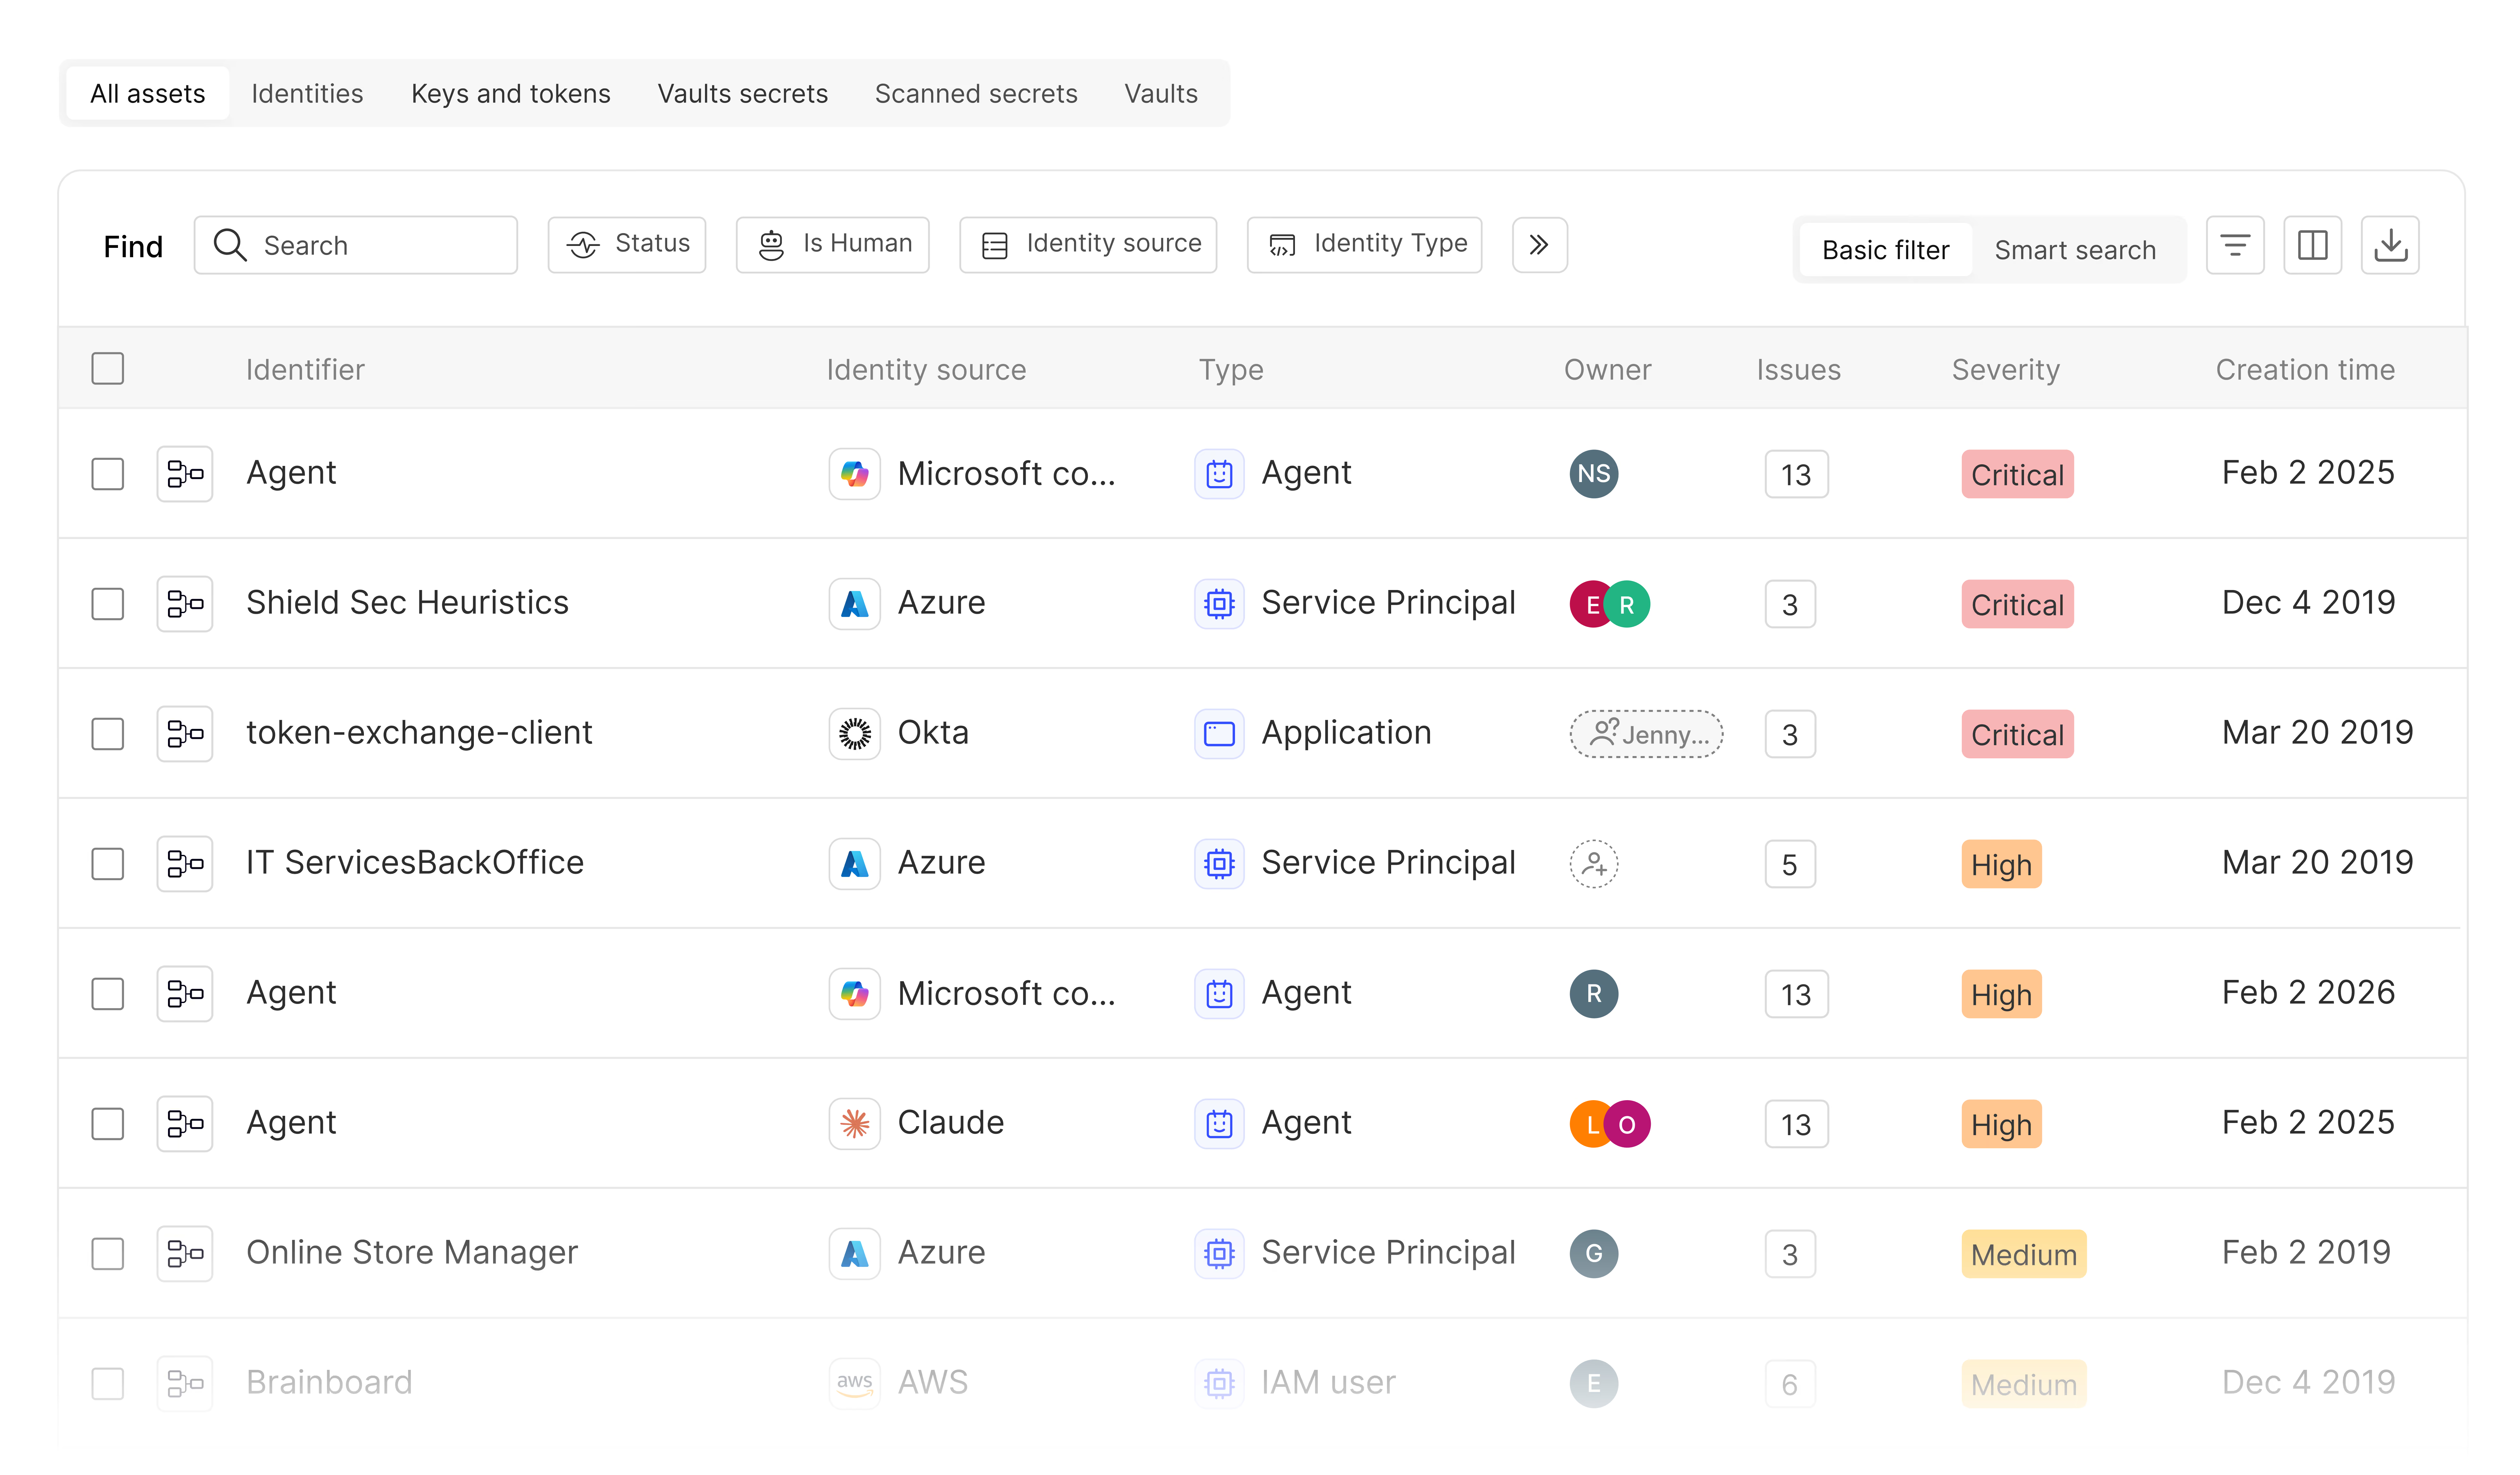
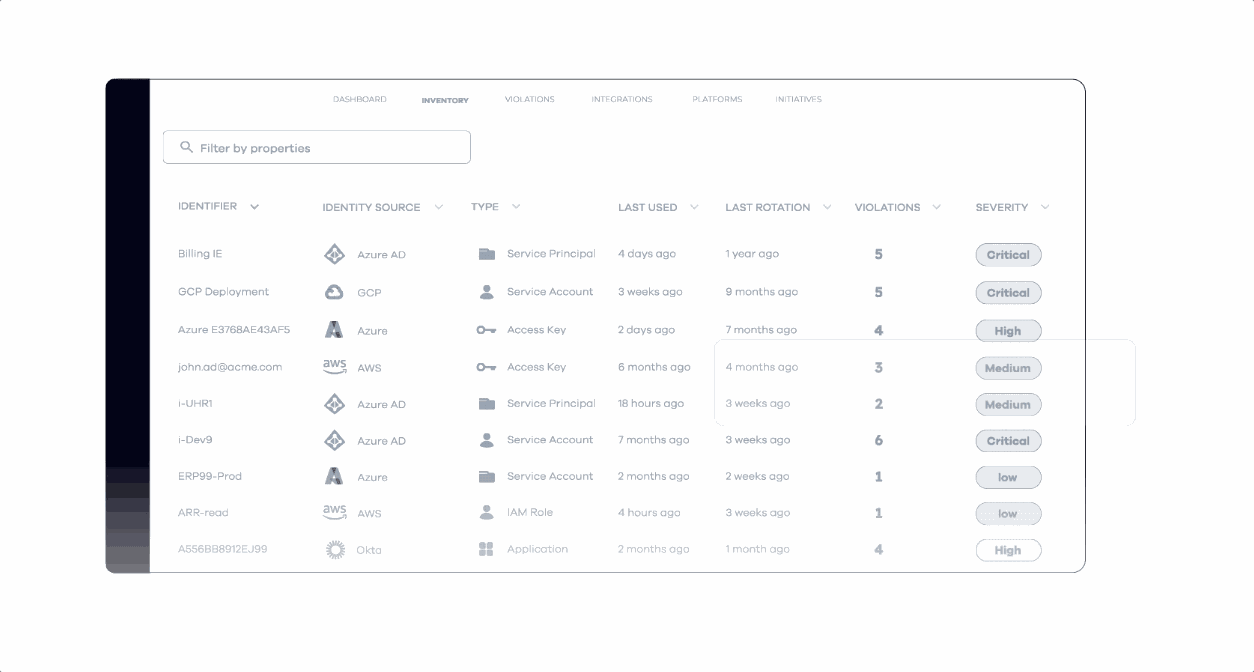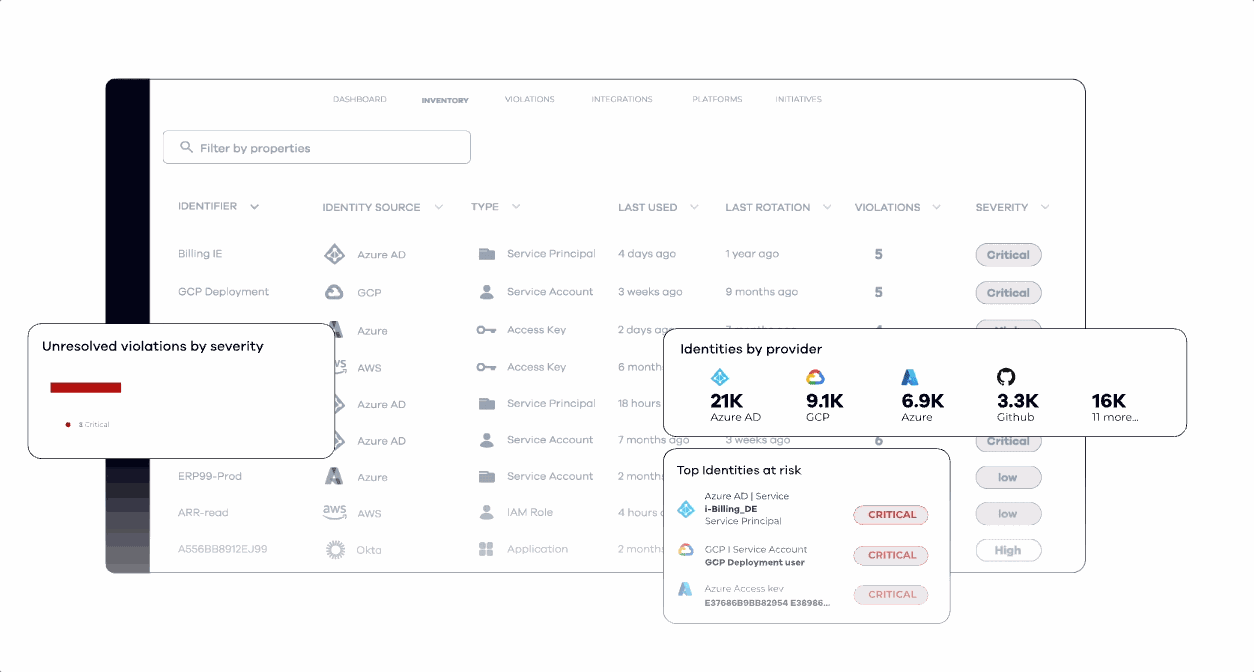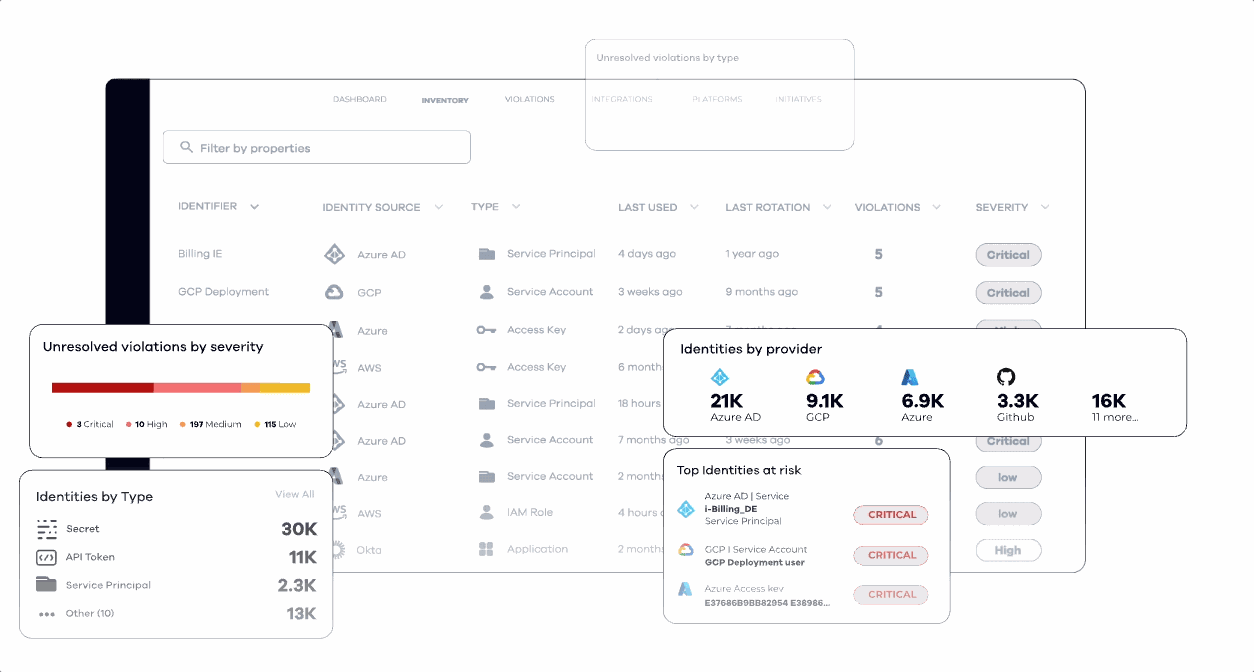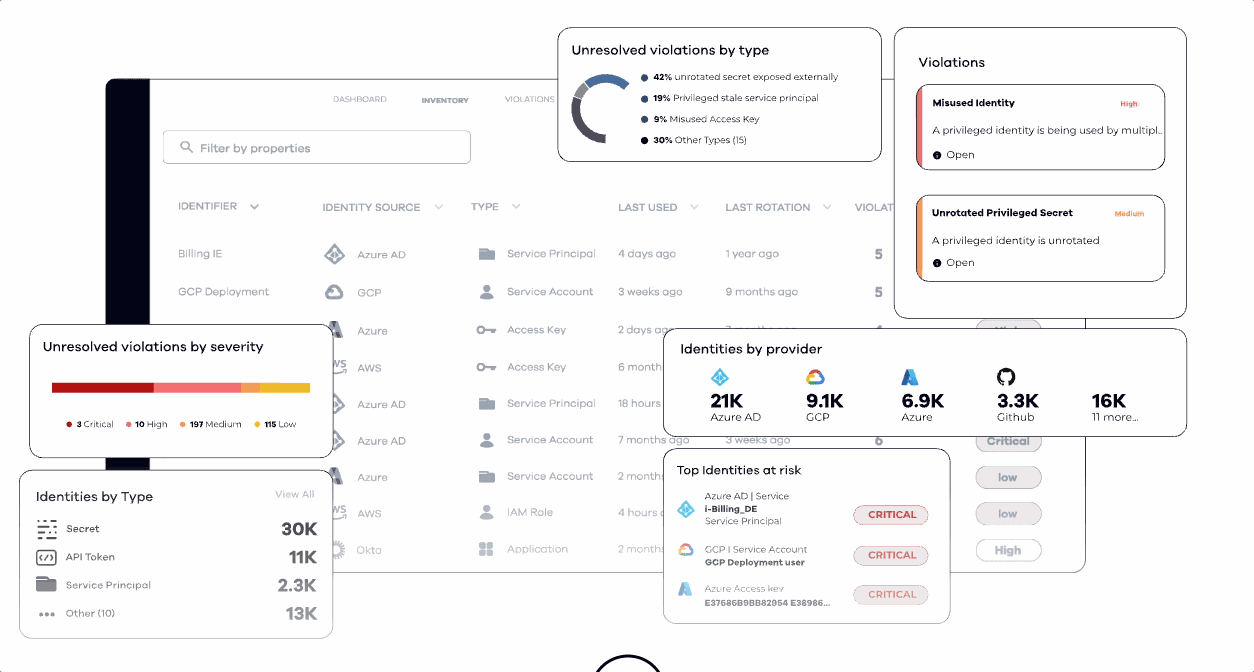
See every non-human identity and AI agent, and tie together usage, owner, risk, and the data it can reach. Govern every identity by policy, enforce agent access in real time, and hand your auditors the proof.
Lottie File version (below)
From non-human identity governance to real-time enforcement. Every AI agent, service account, and machine identity, controlled and enforced under a single policy and mapped to the data it reaches.
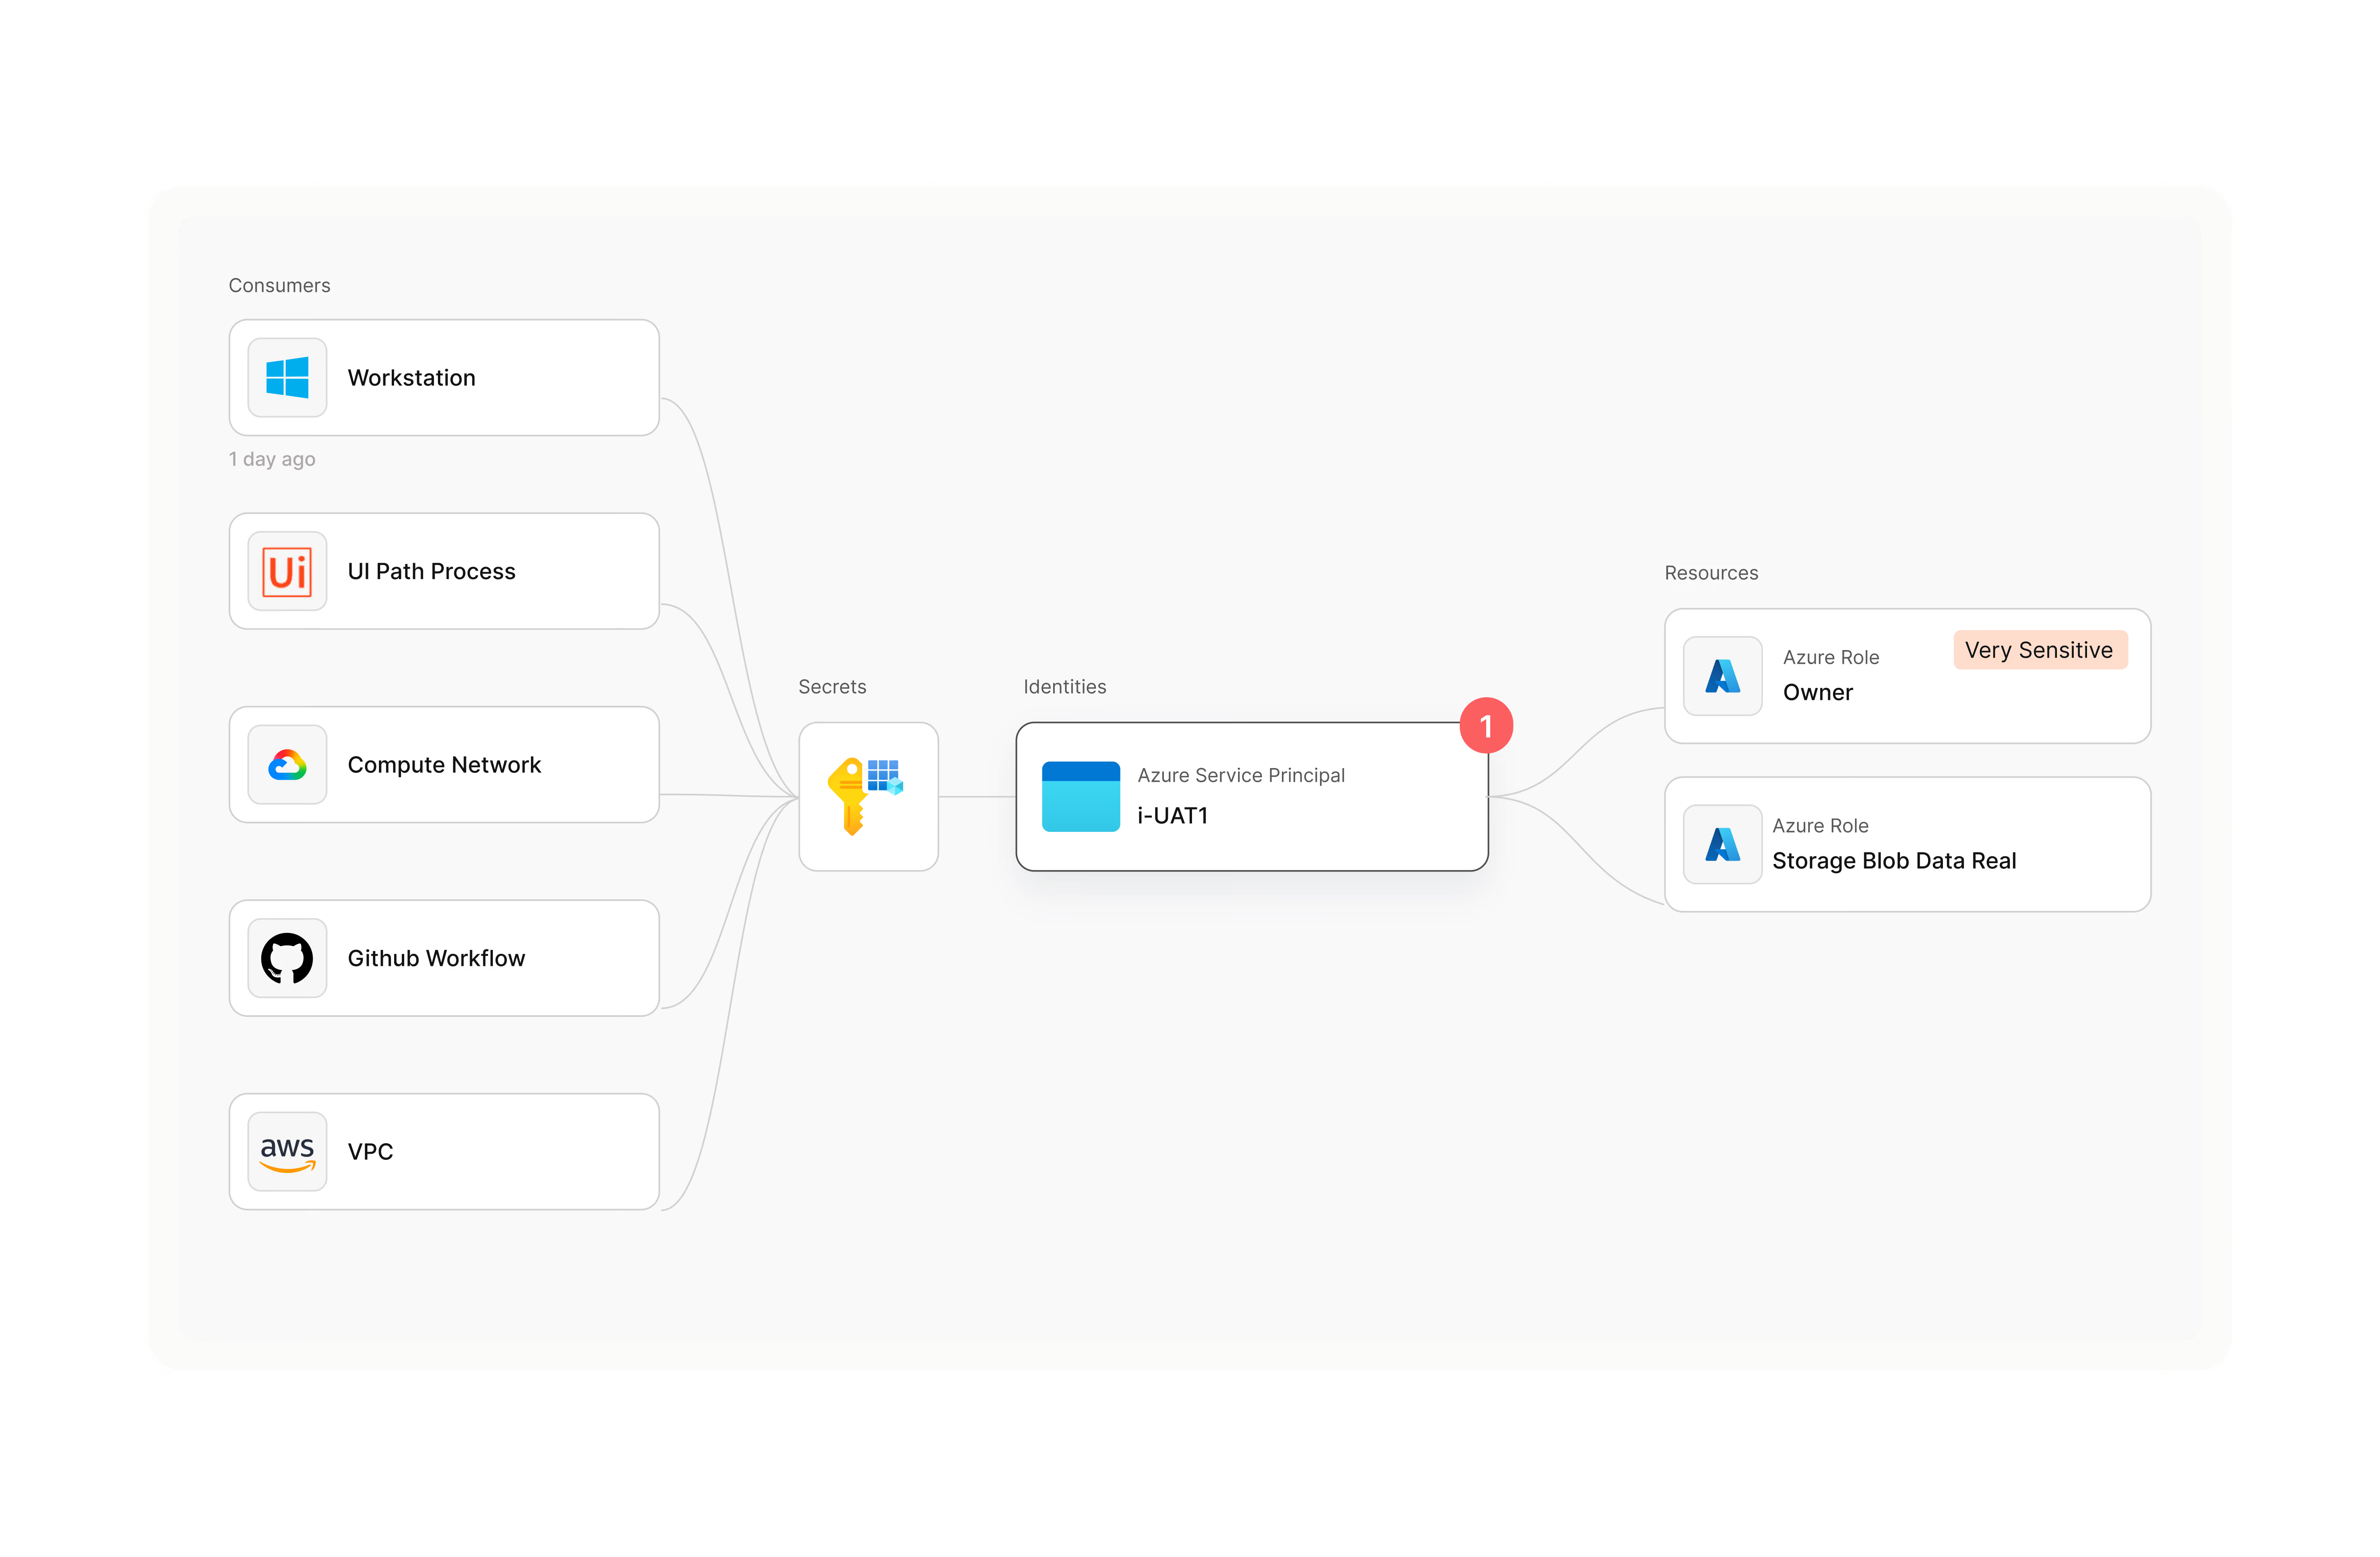
Know who uses every identity and what it can reach
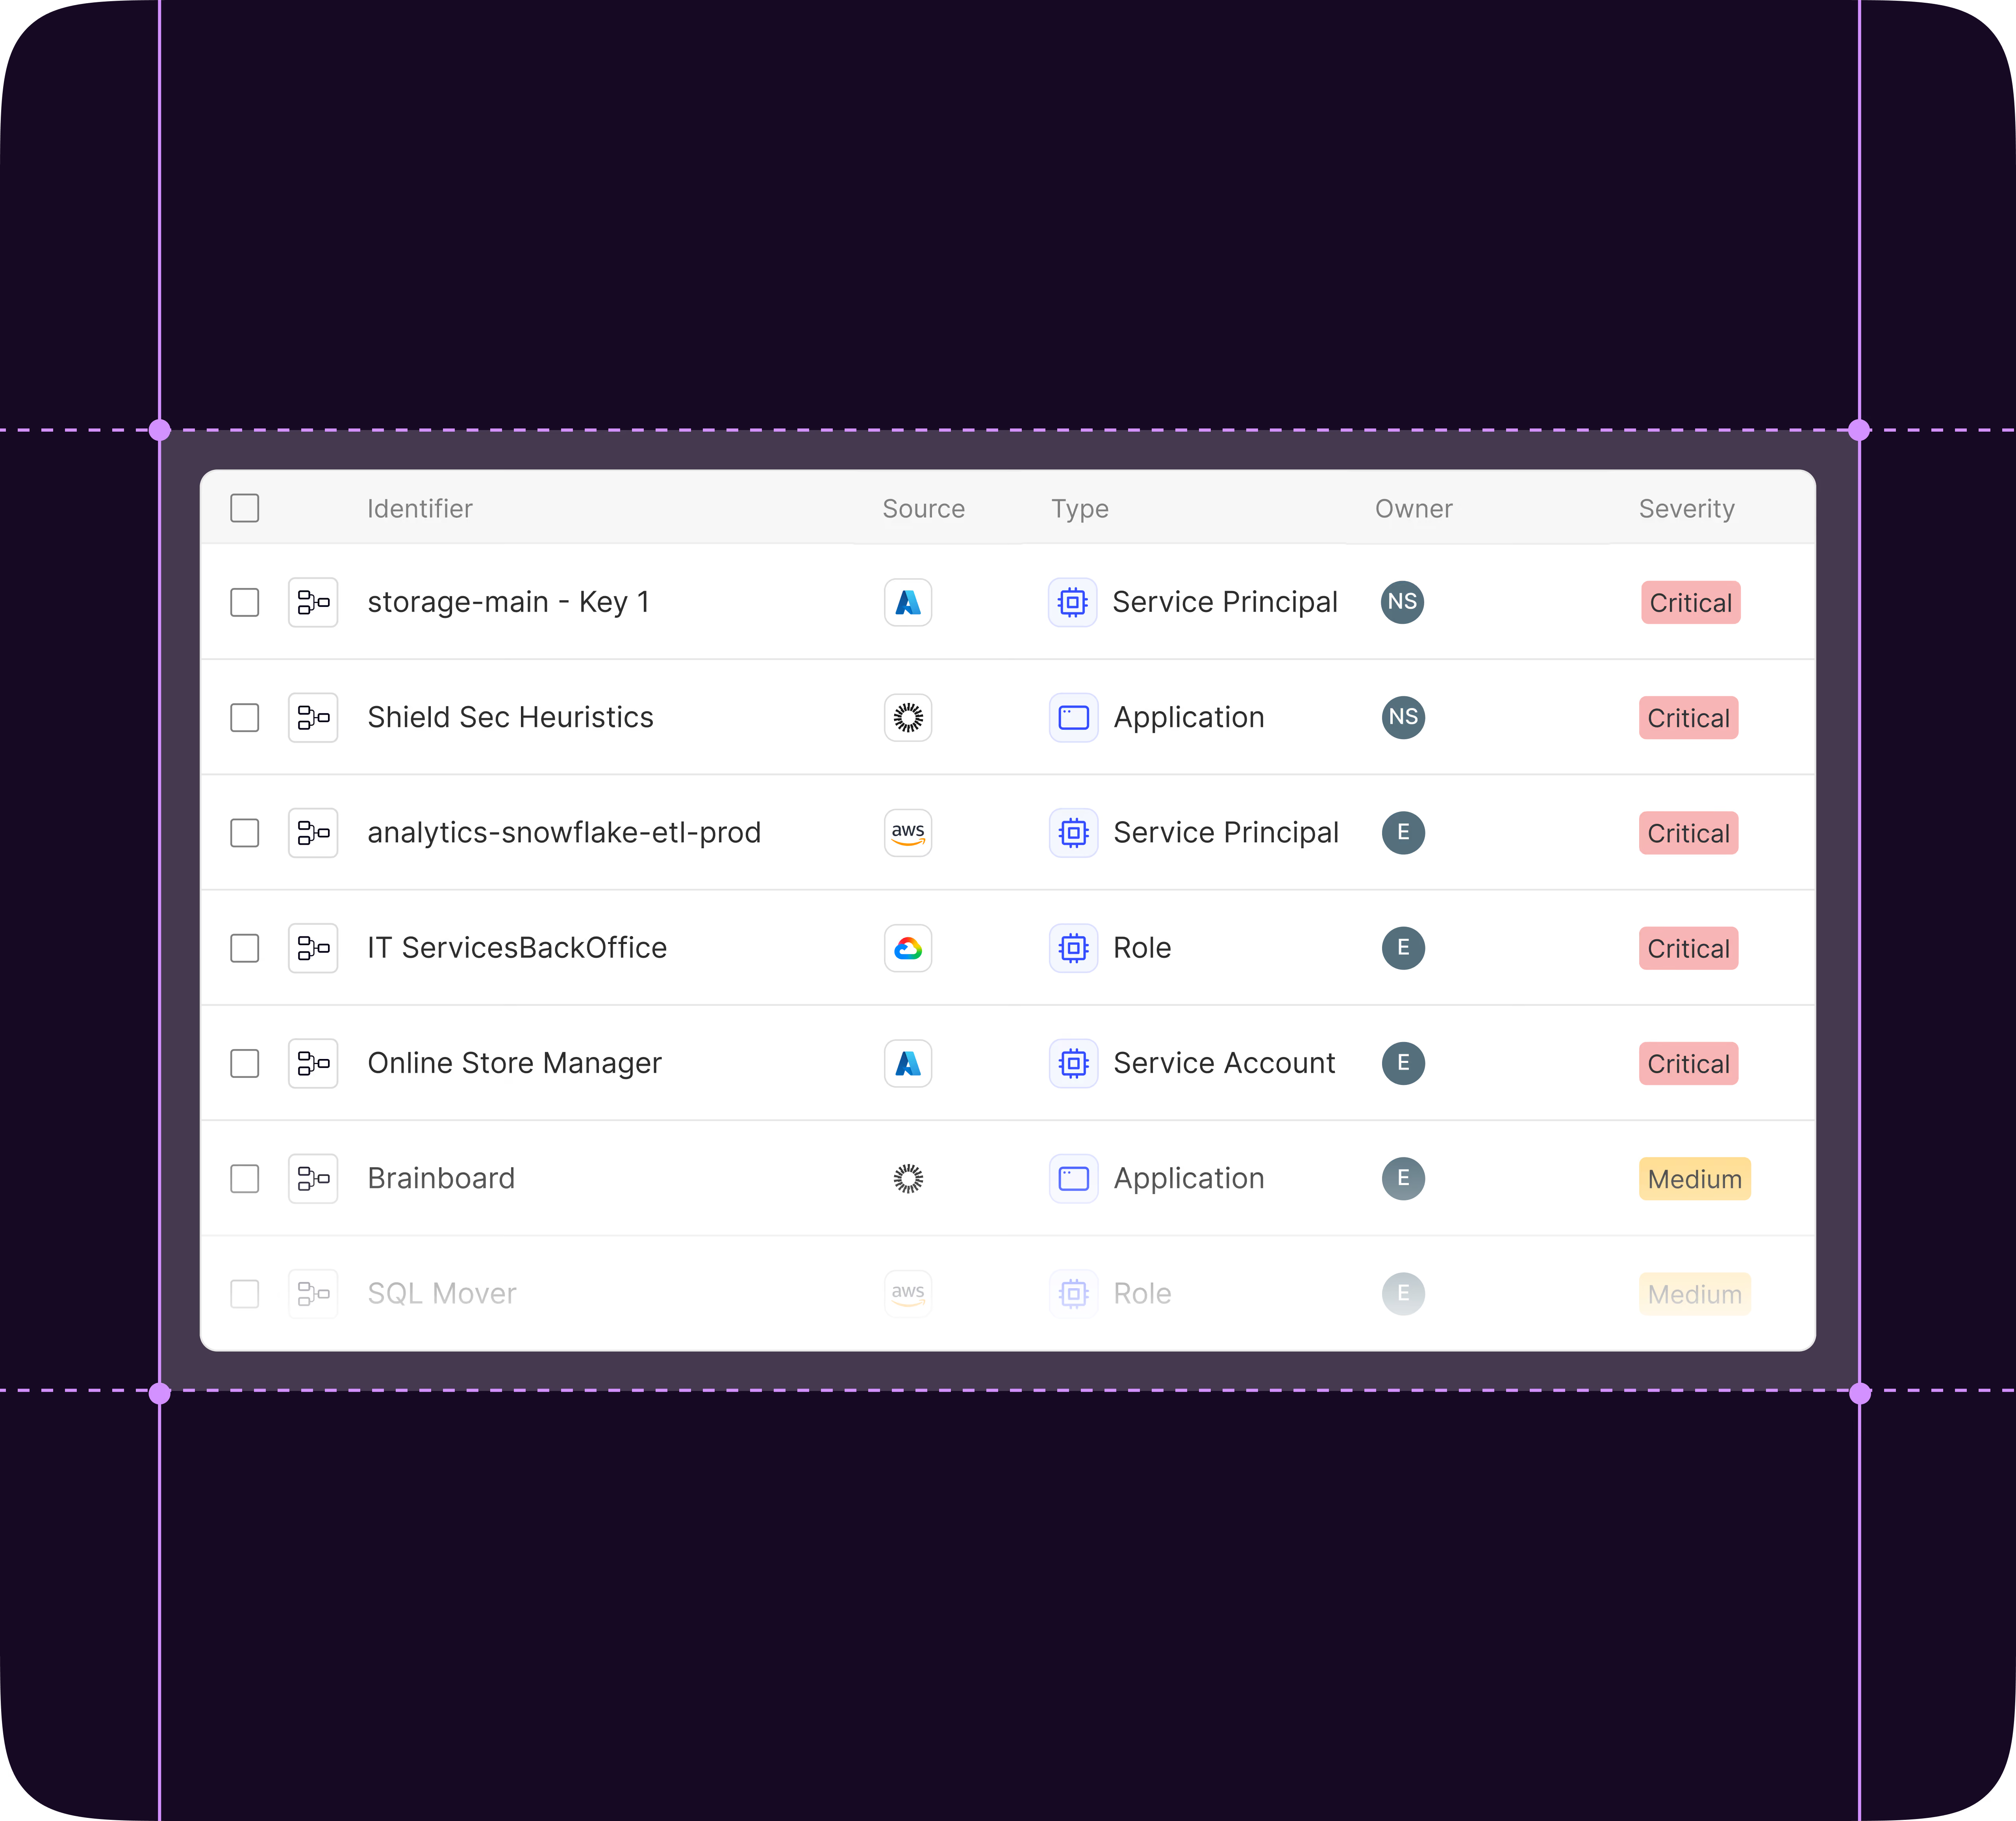
Inventory every service account, API key, token, and AI agent across cloud, SaaS, on-premises, and AI platforms, including shadow AI and MCP servers nobody approved. Understand each one by how it's really used: who or what relies on it, what it can access, how sensitive that data is, and who is accountable for it.
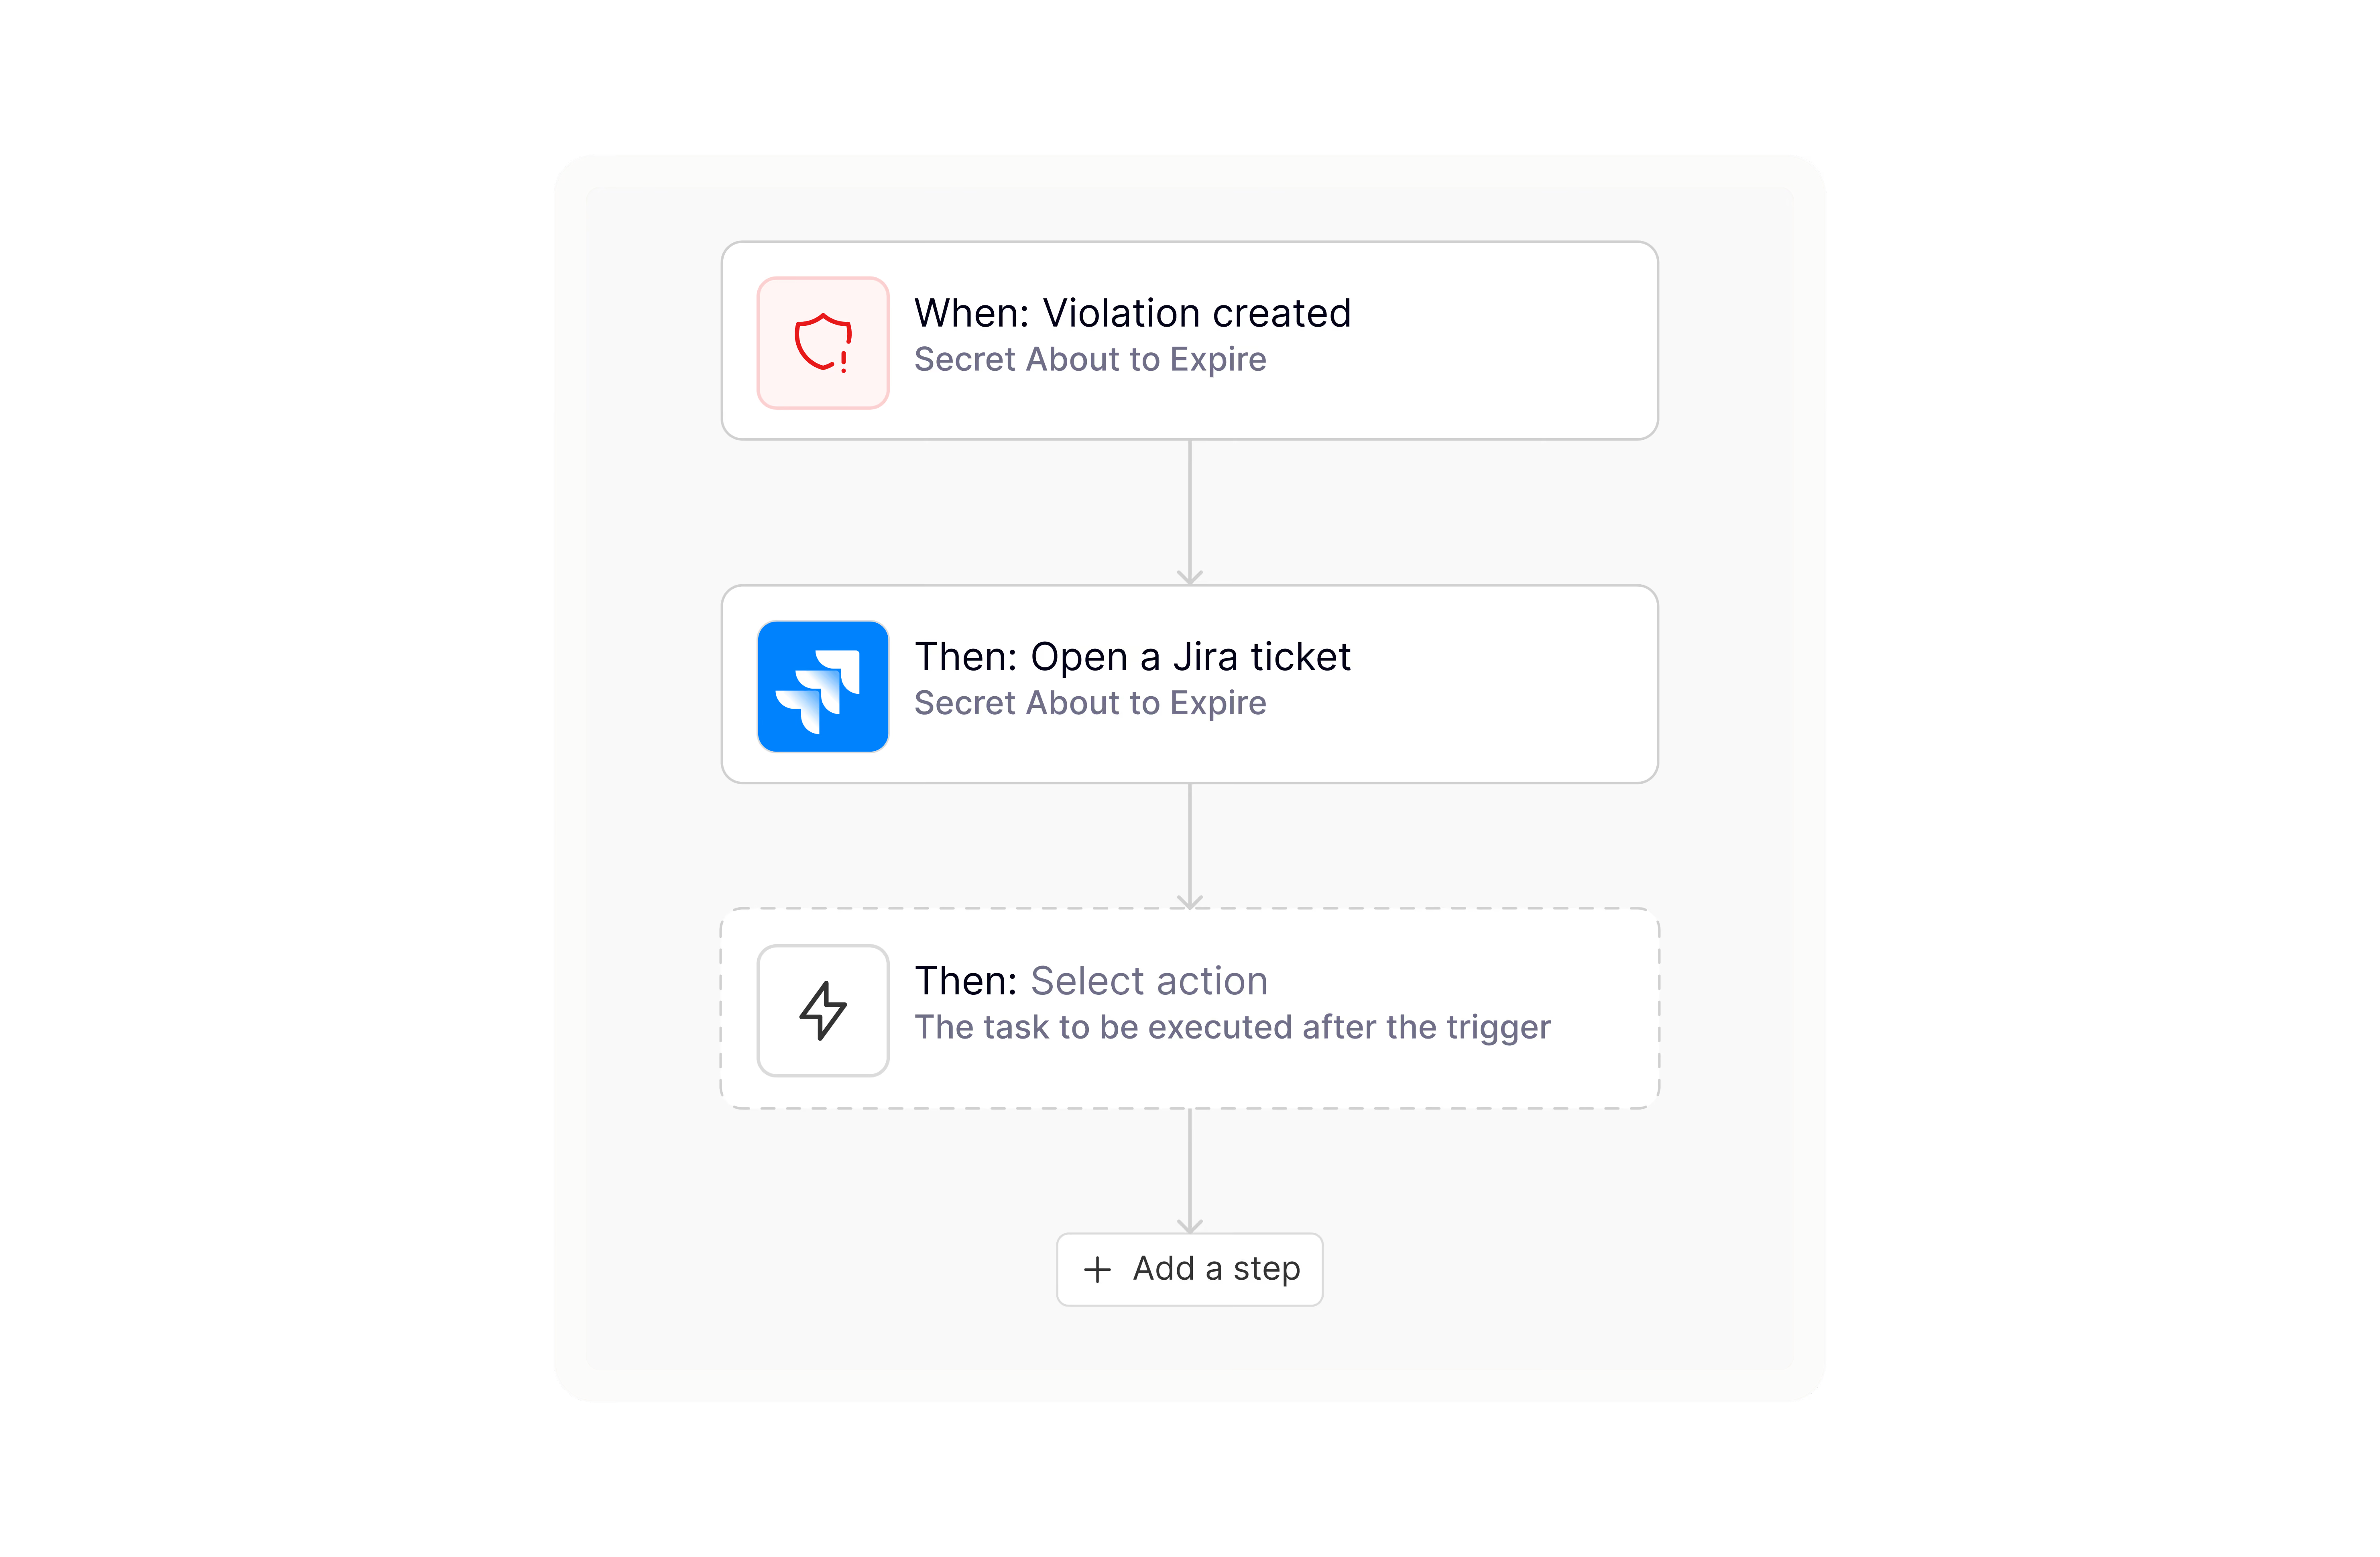
Manage every identity from creation to retirement
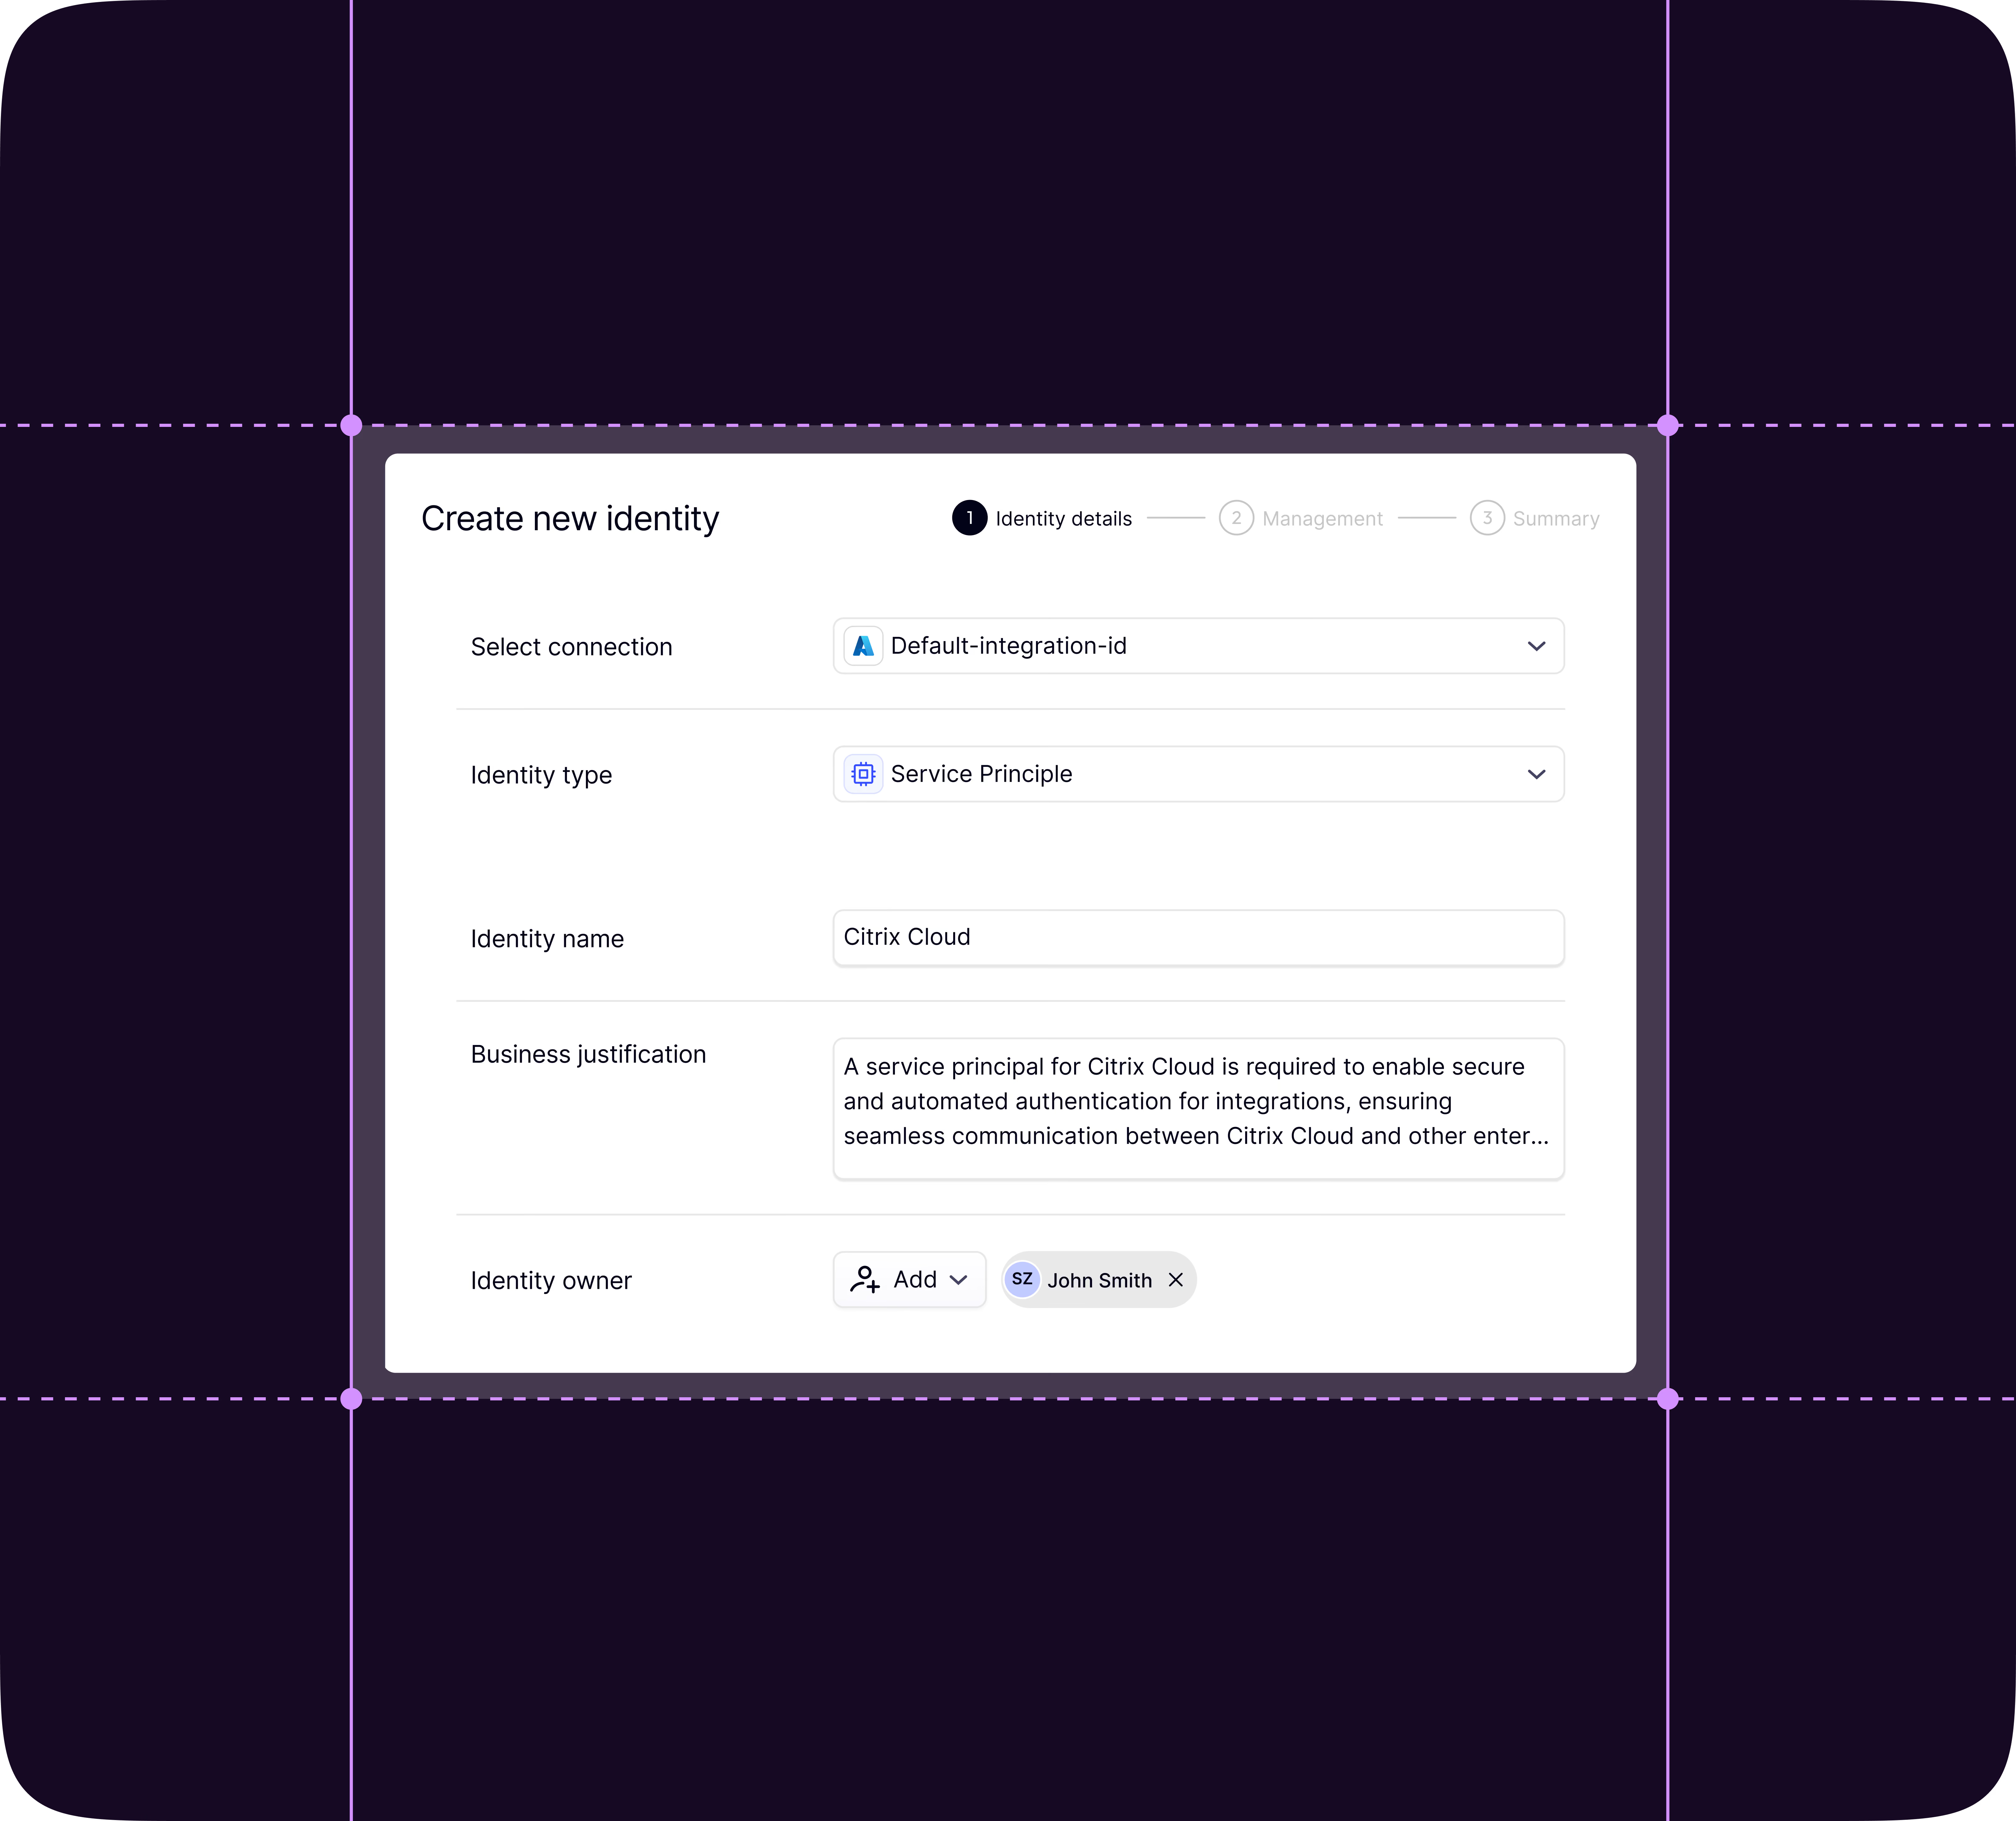
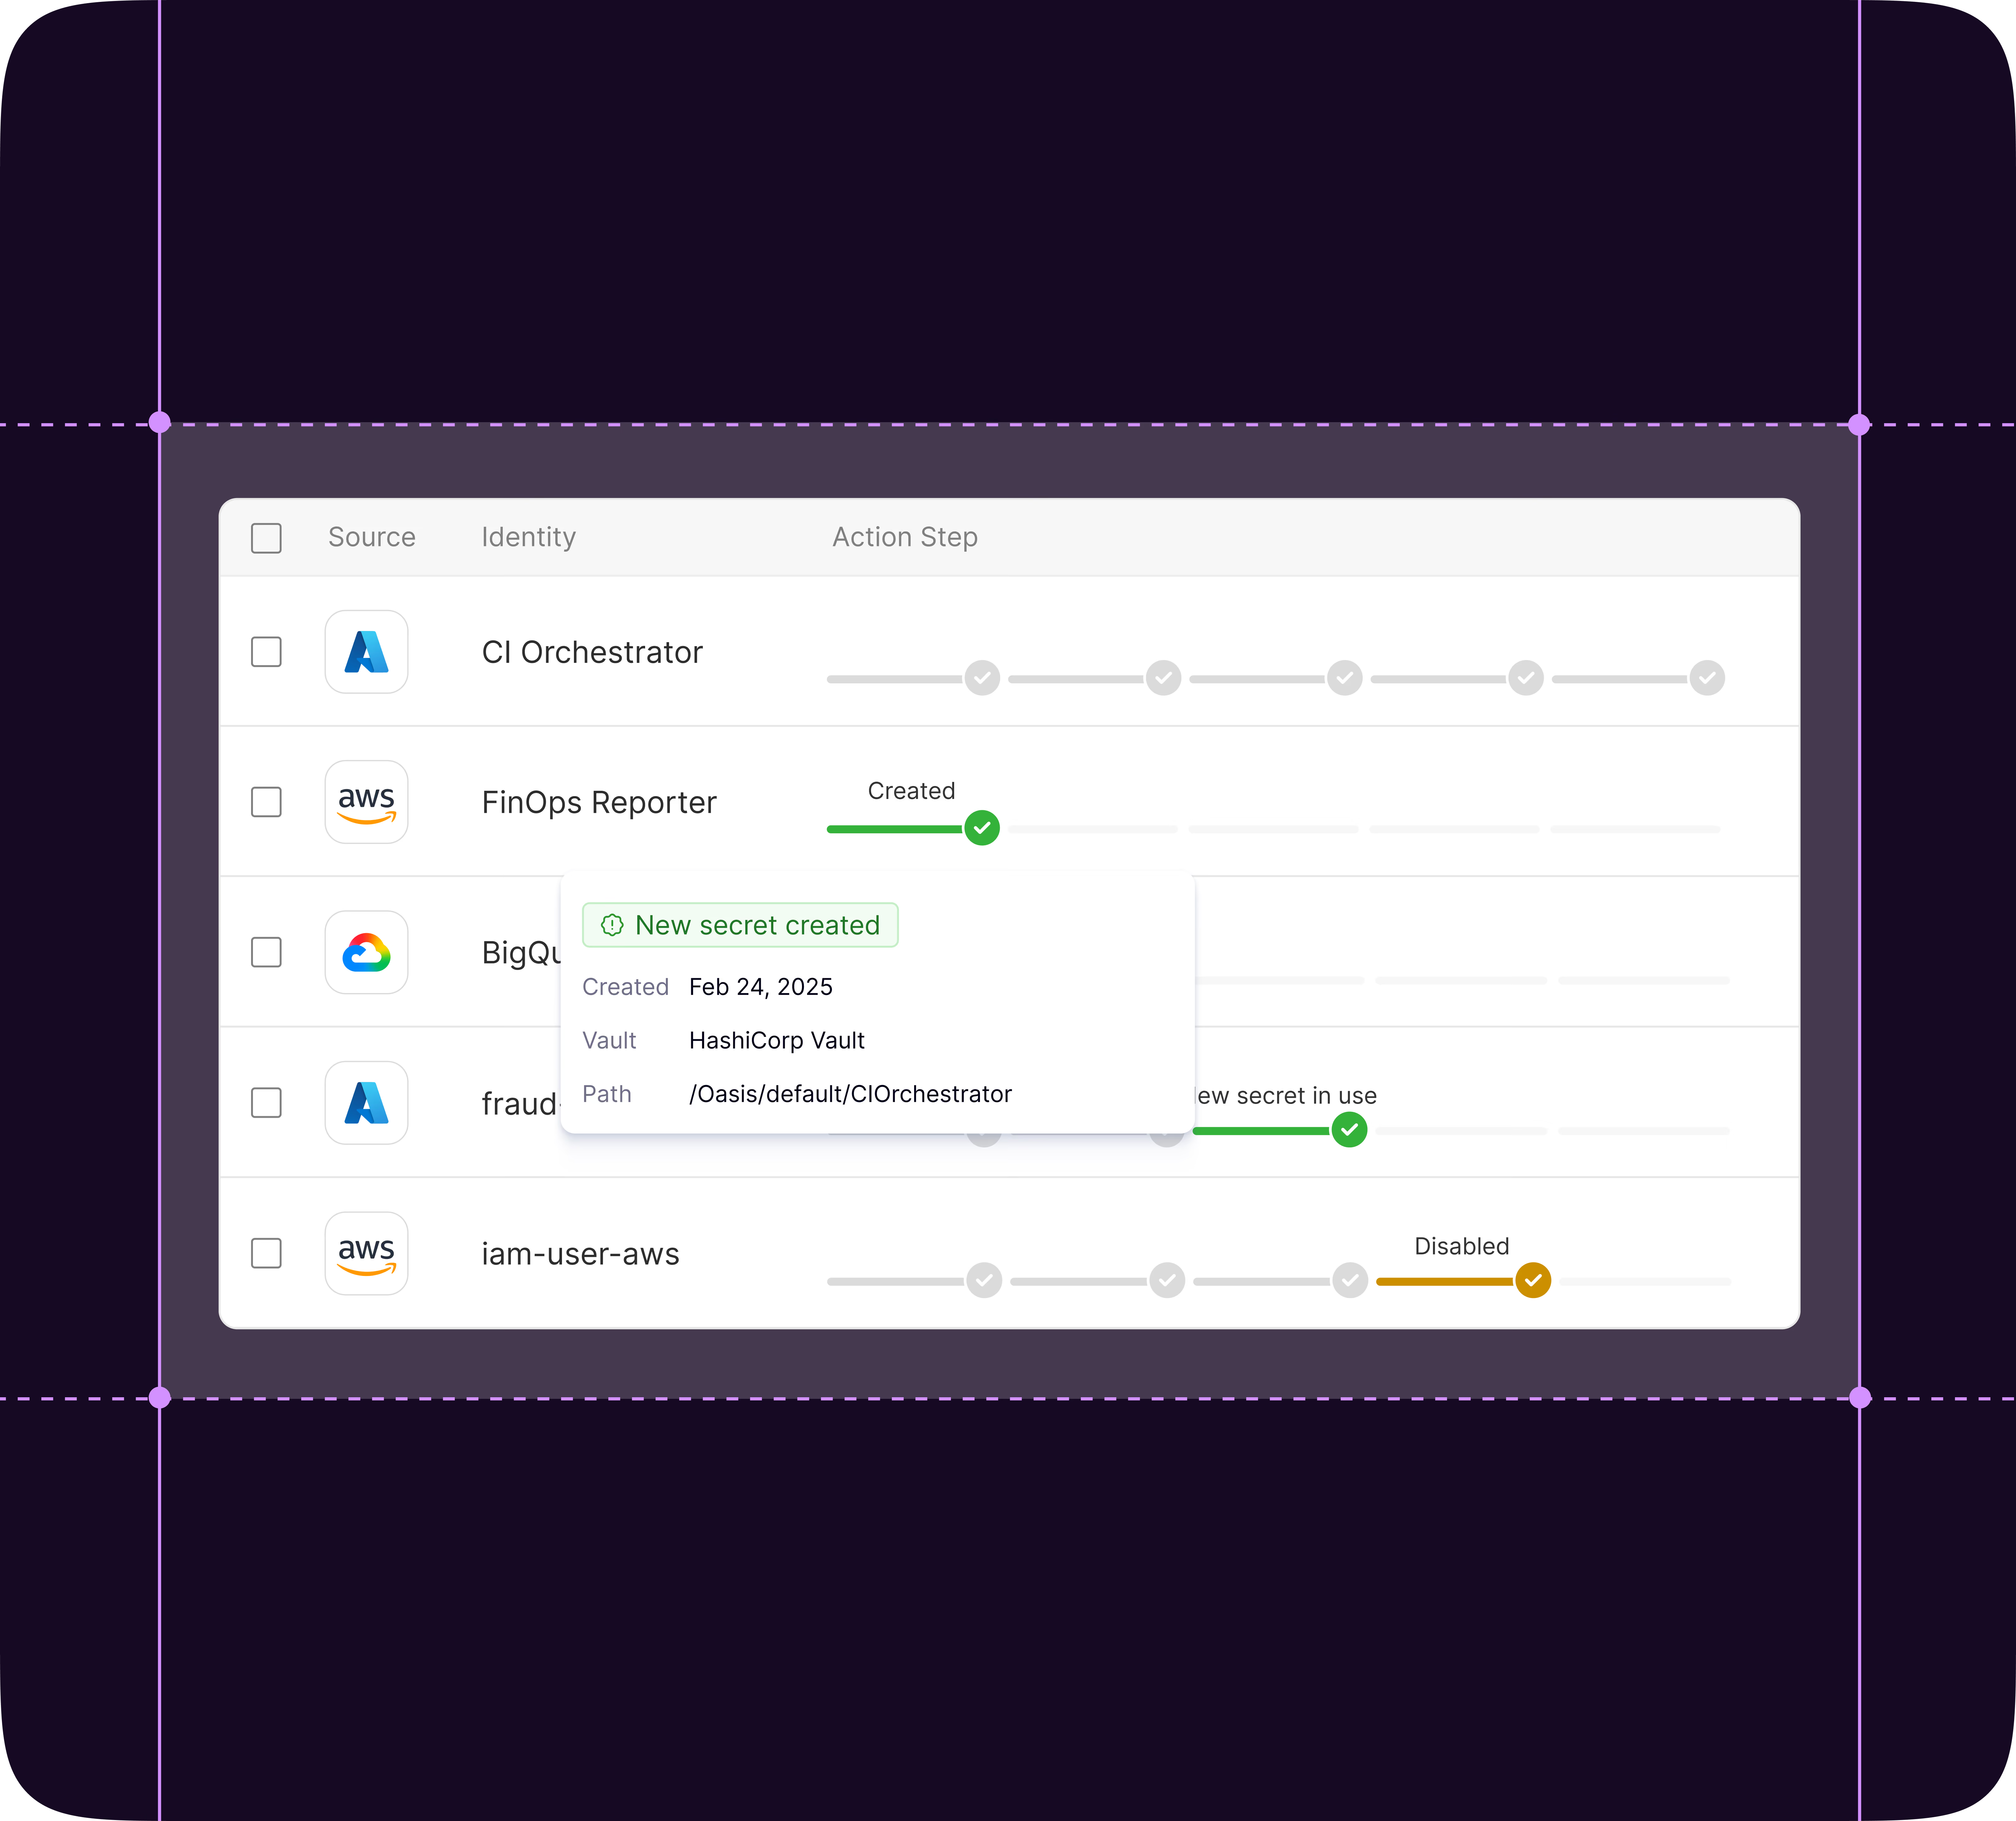
Define lifecycle policies once and apply them to every identity you govern: created with an owner and a purpose, rotated on schedule, re-certified by its owner, and retired when it's no longer used. Each step runs through the vaults and identity providers and tools you already have.
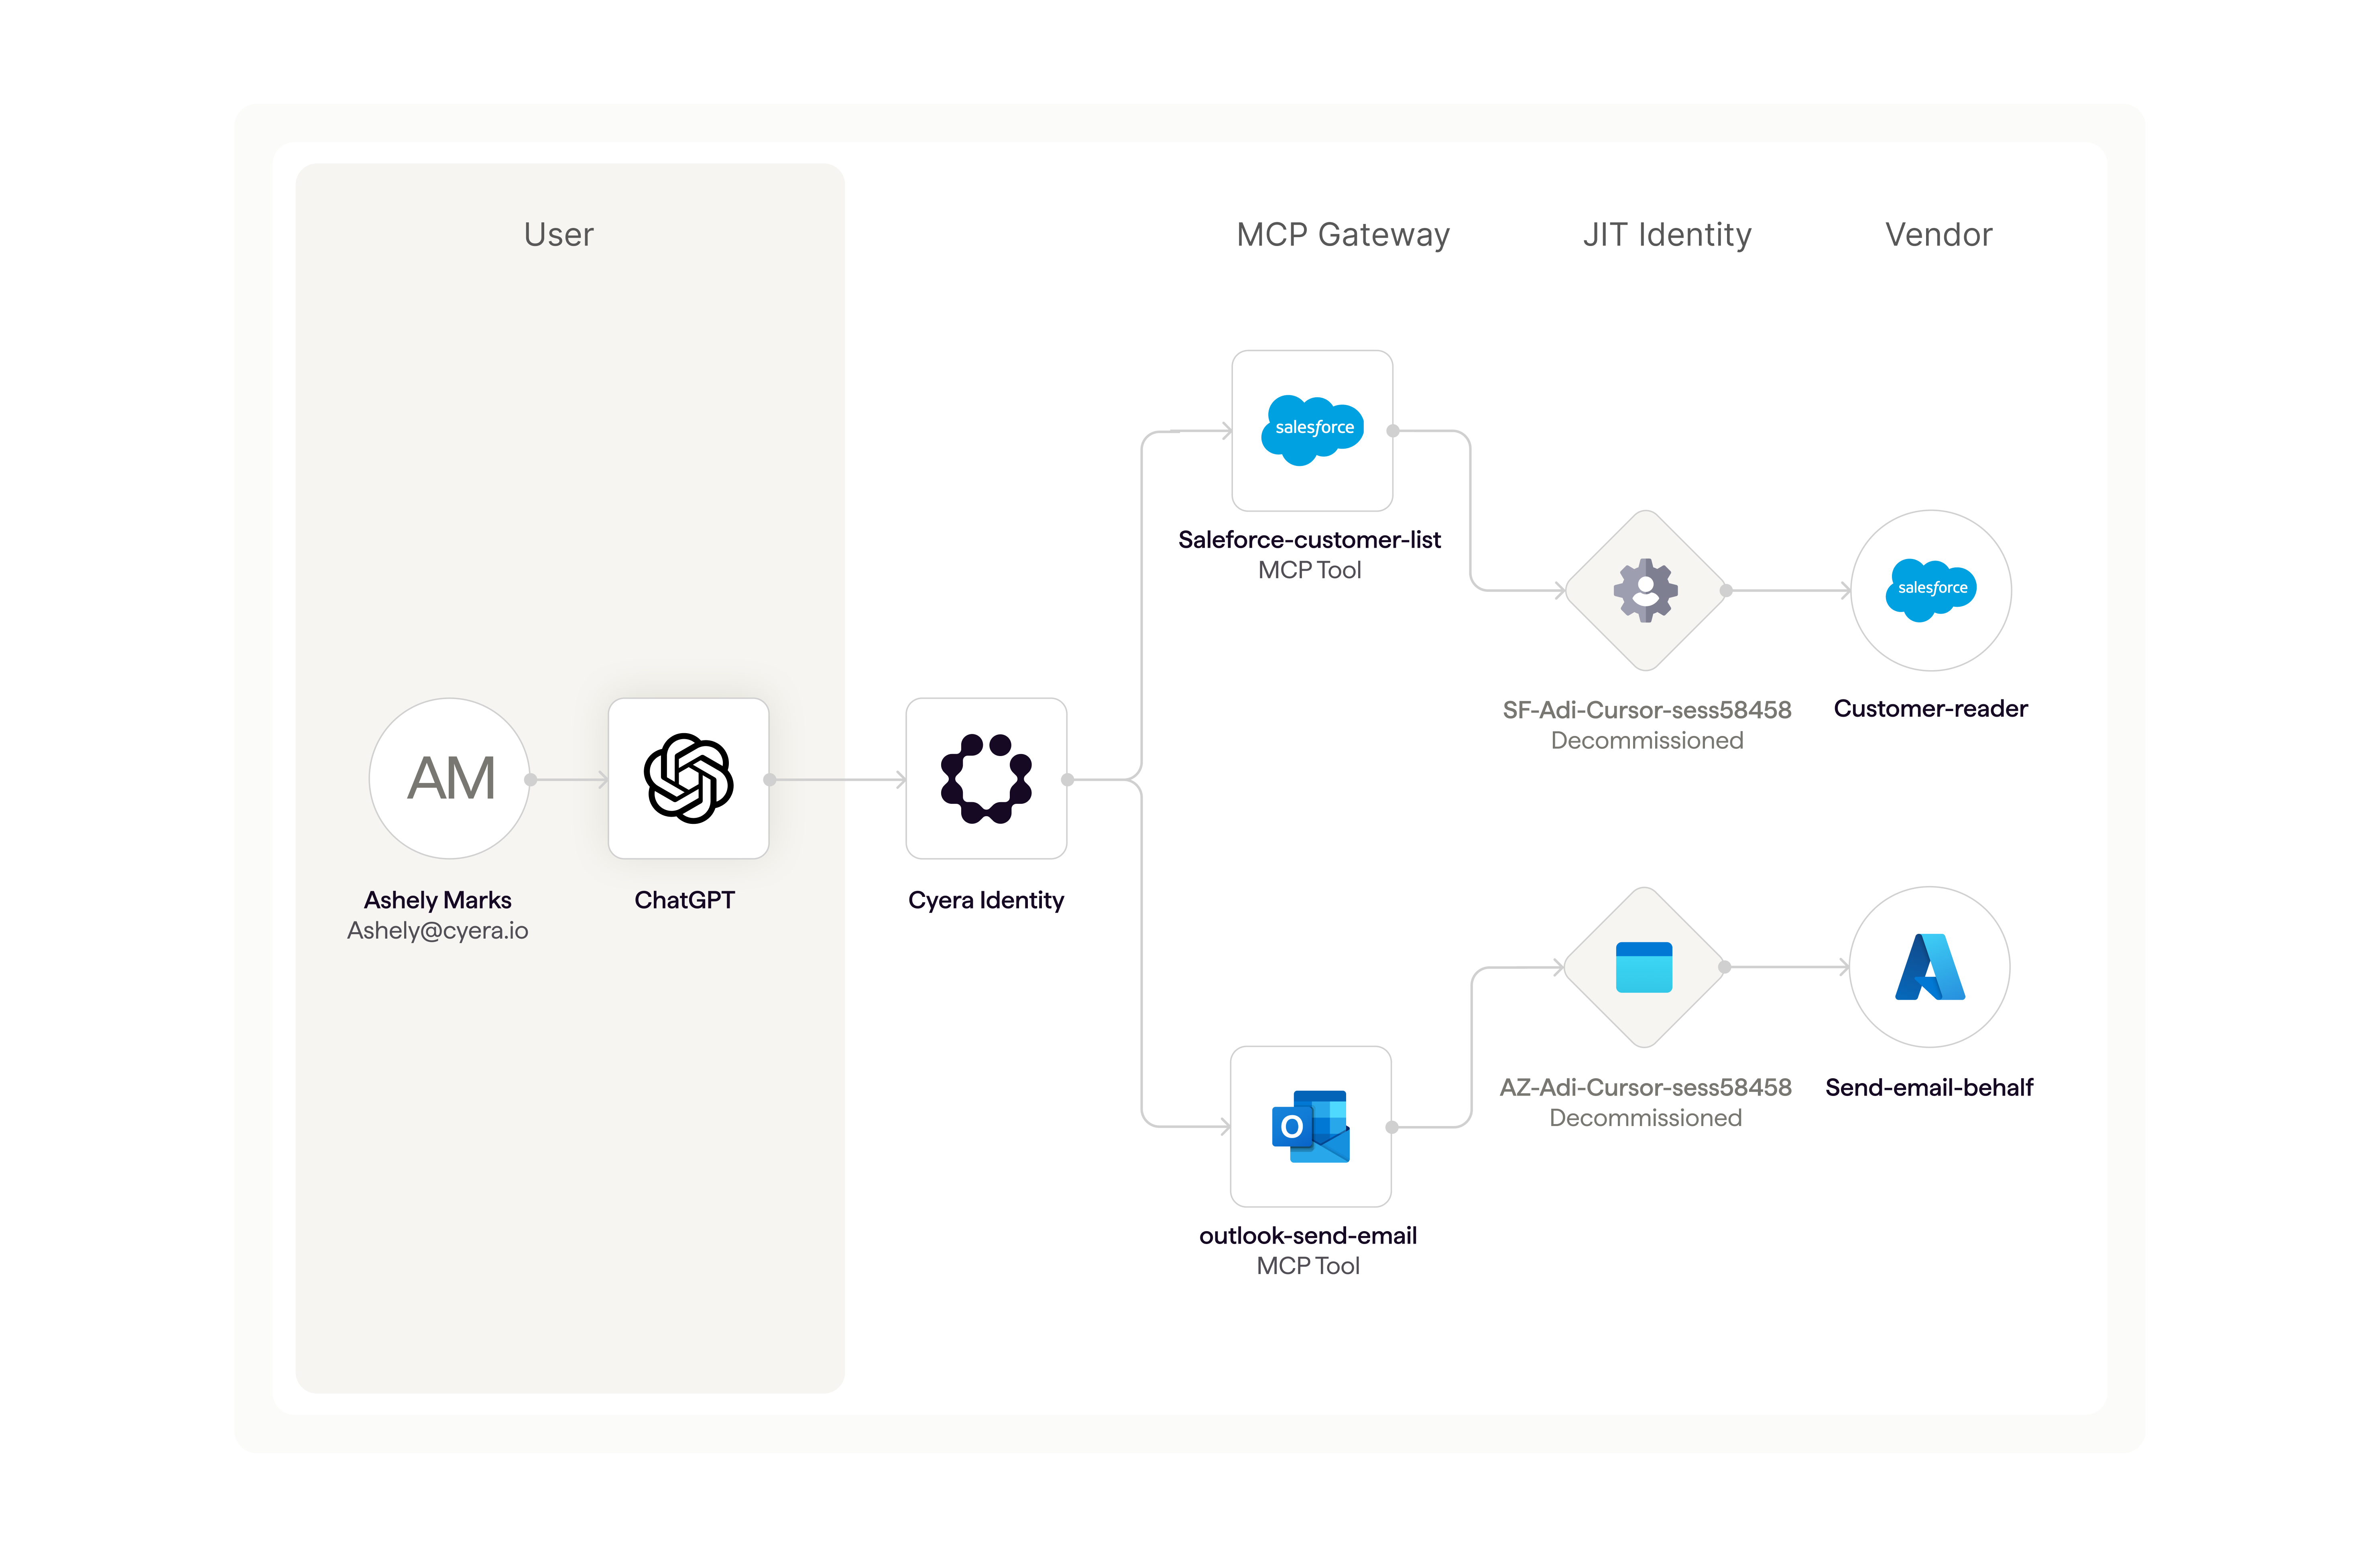
Give agents only the access each task needs
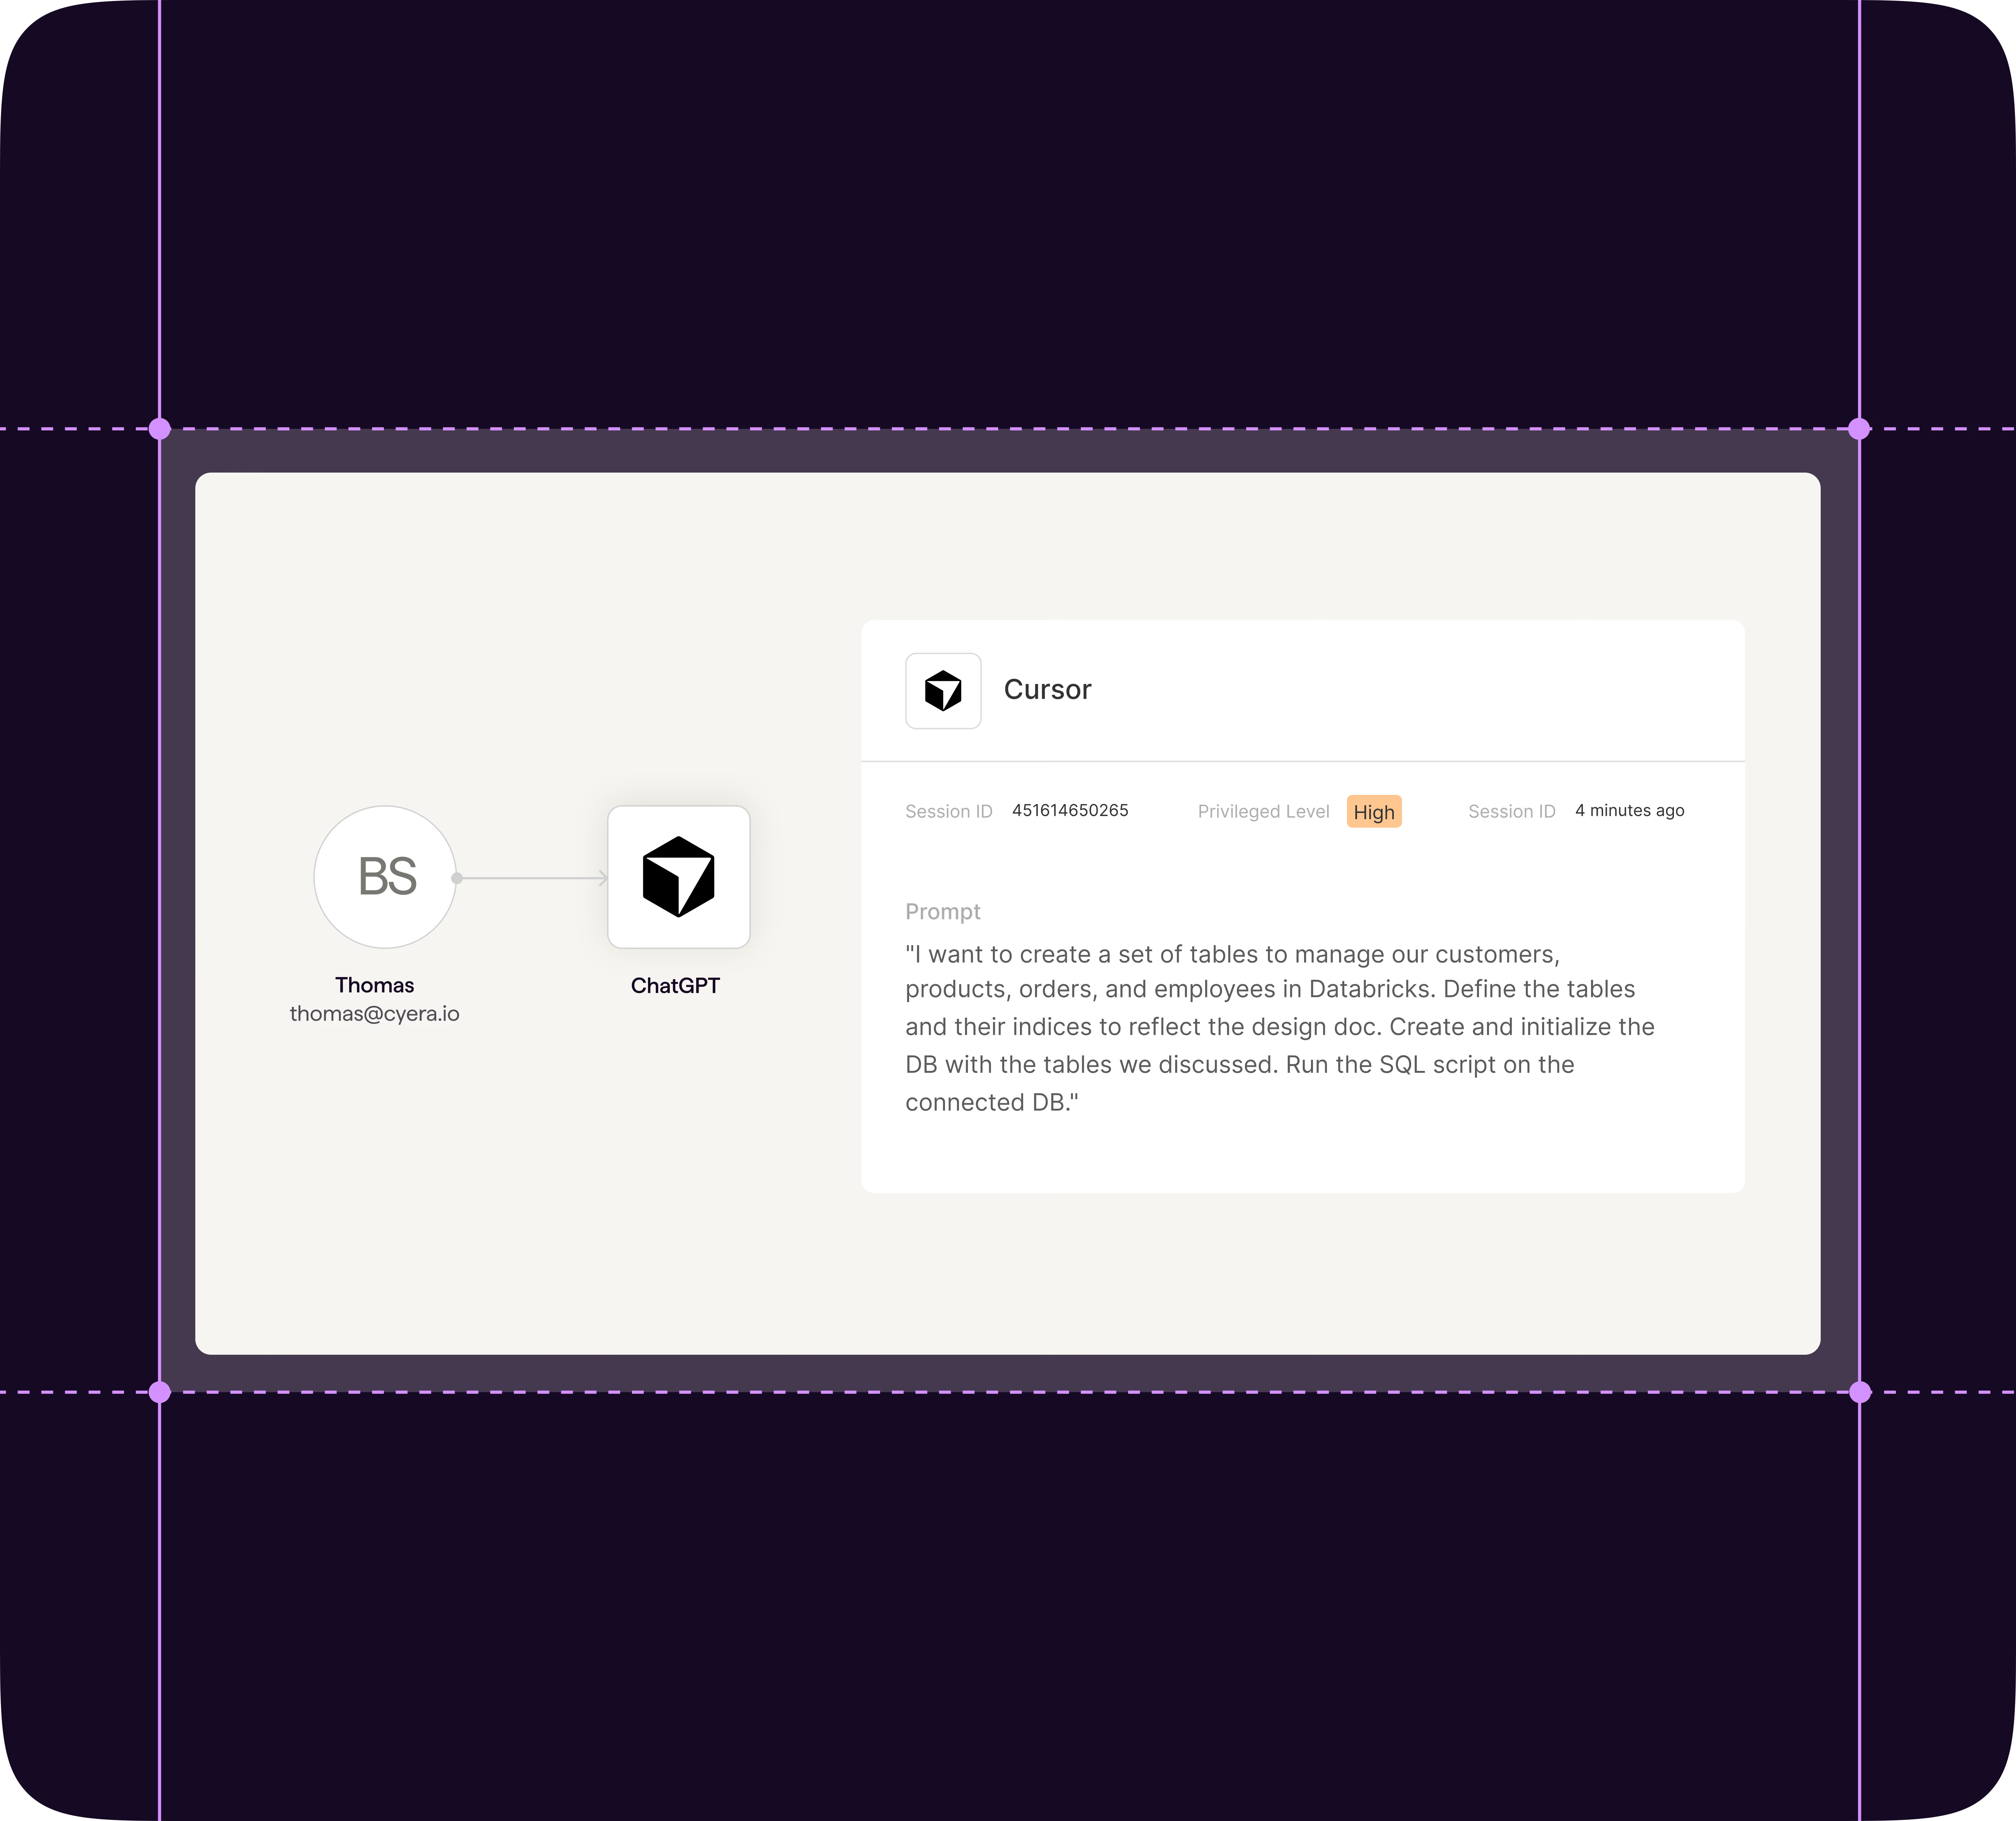
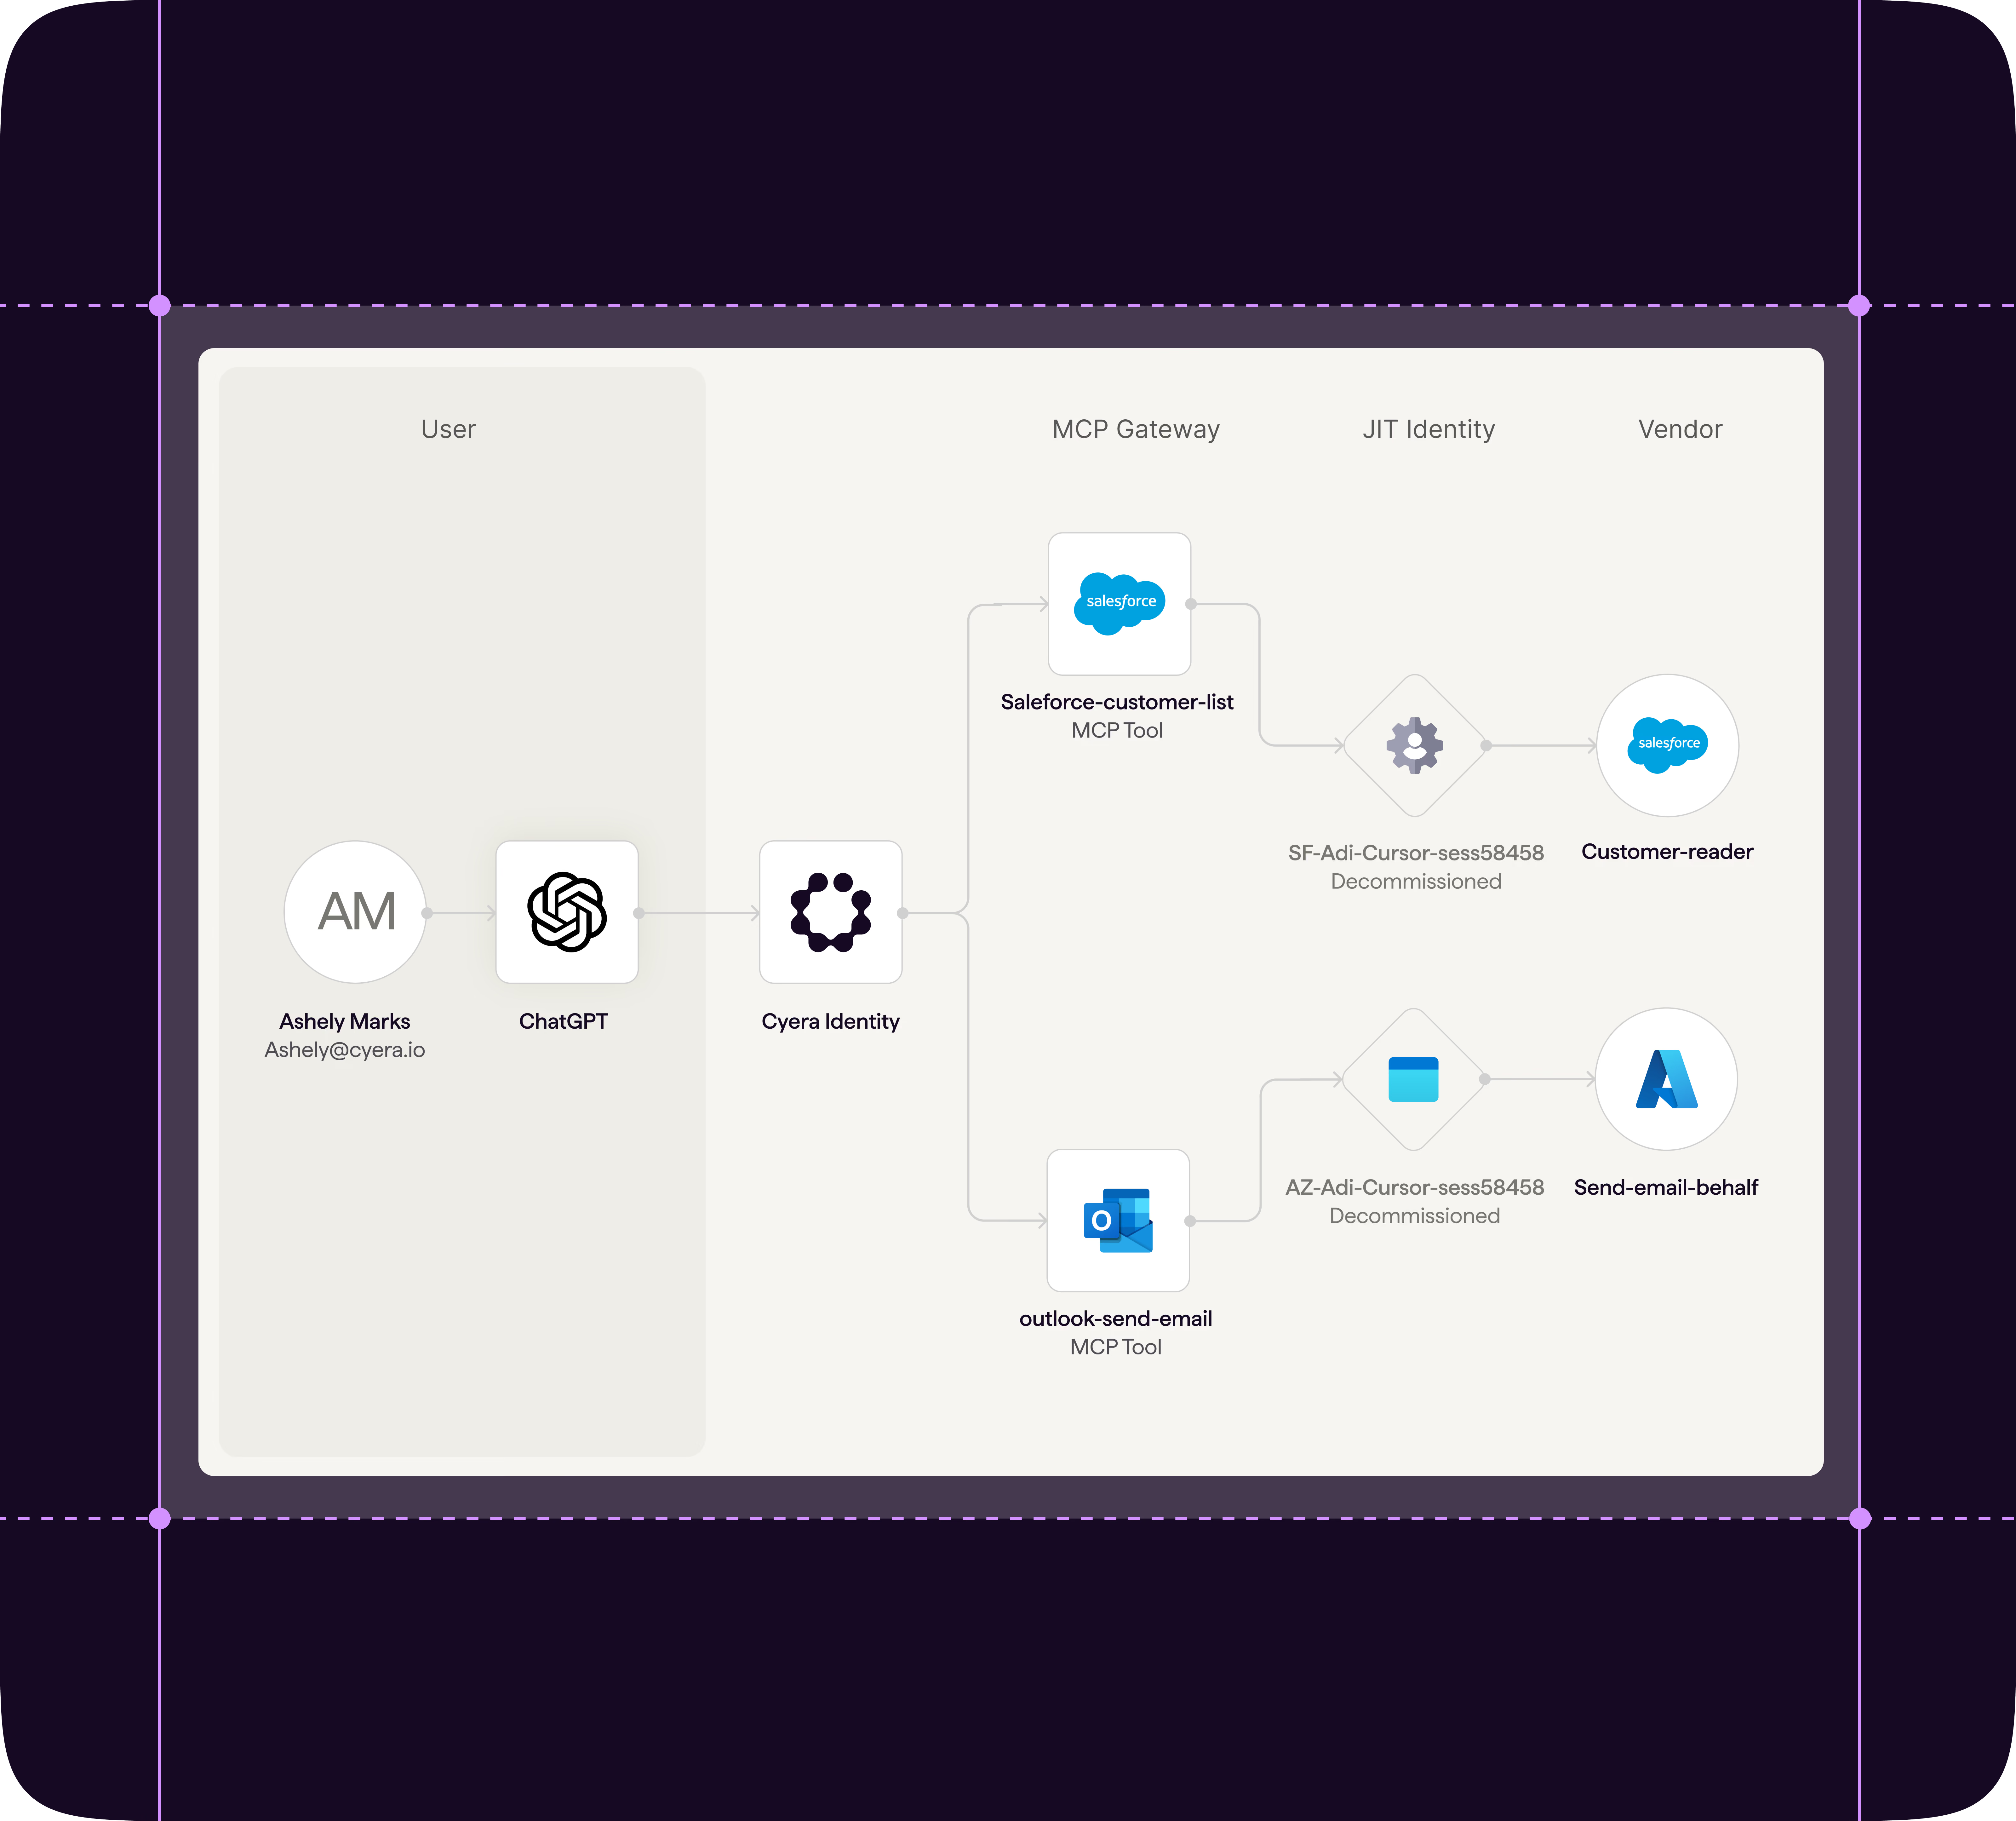
Evaluate every agent request against your access policies in real time, and grant a short-lived identity scoped to that task, with the user's approval. Access expires when the work is done. Every session is recorded, and any one can be stopped instantly.
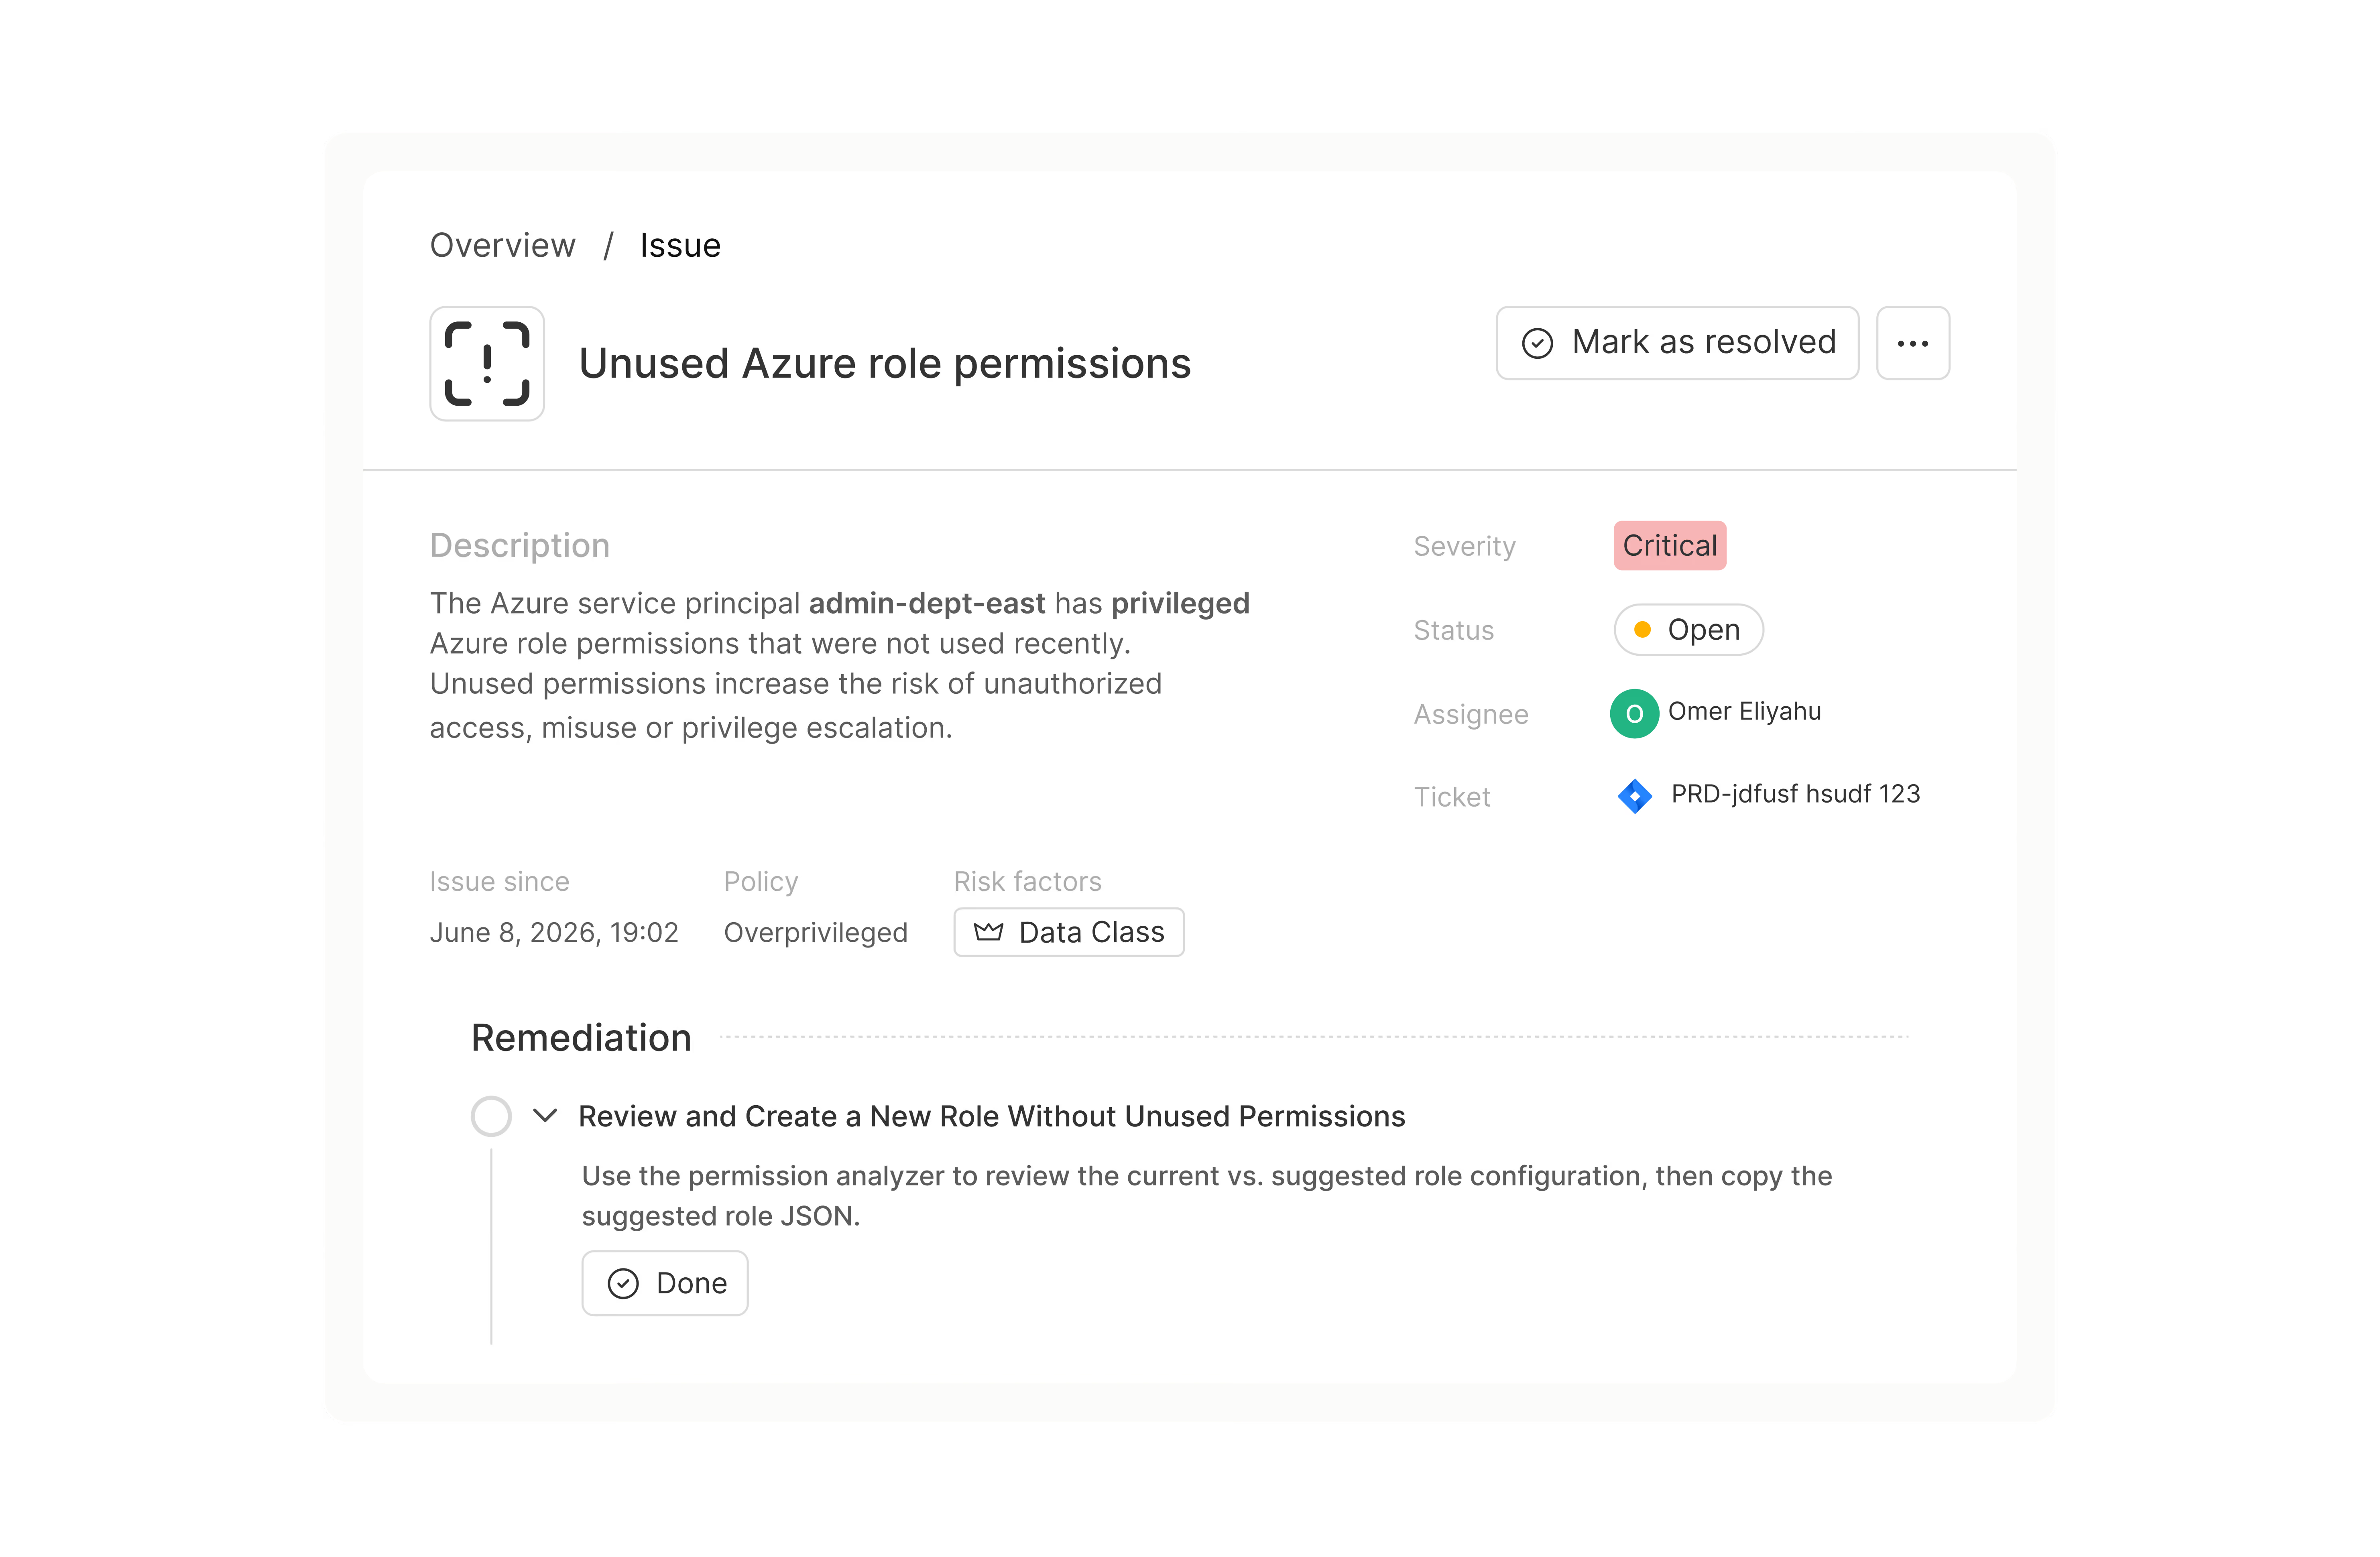
Fix identity risk without breaking production
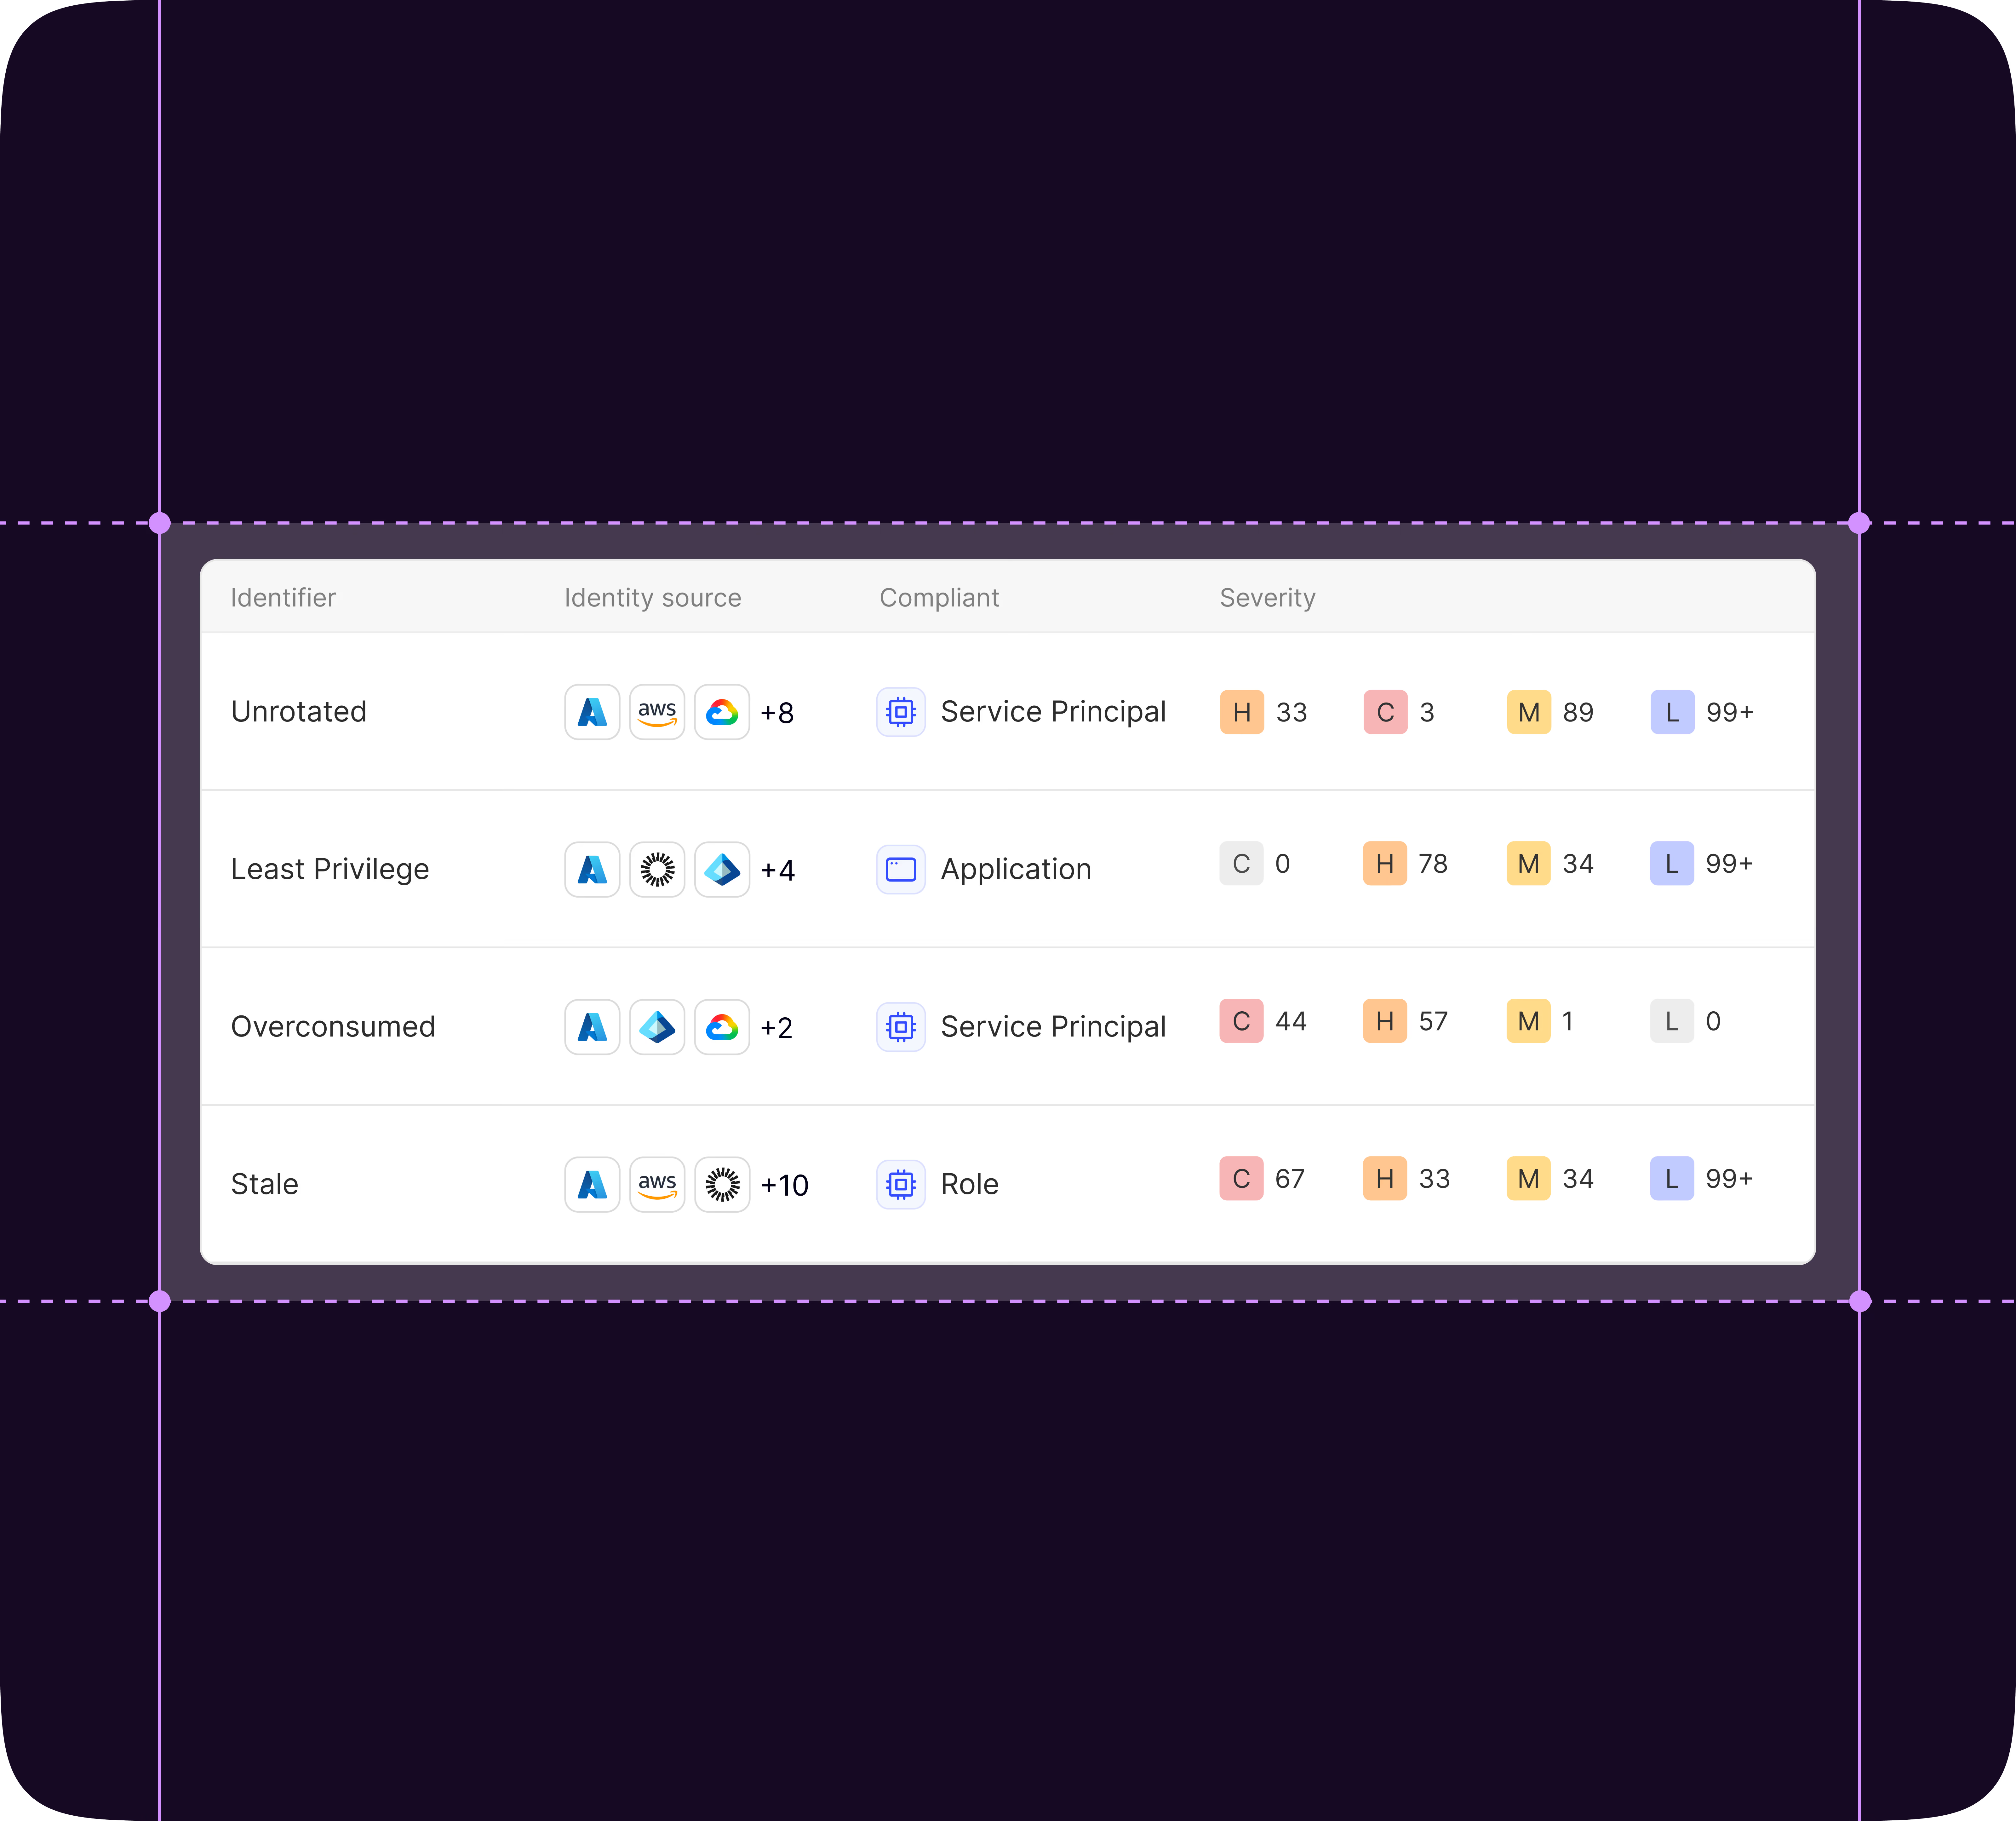
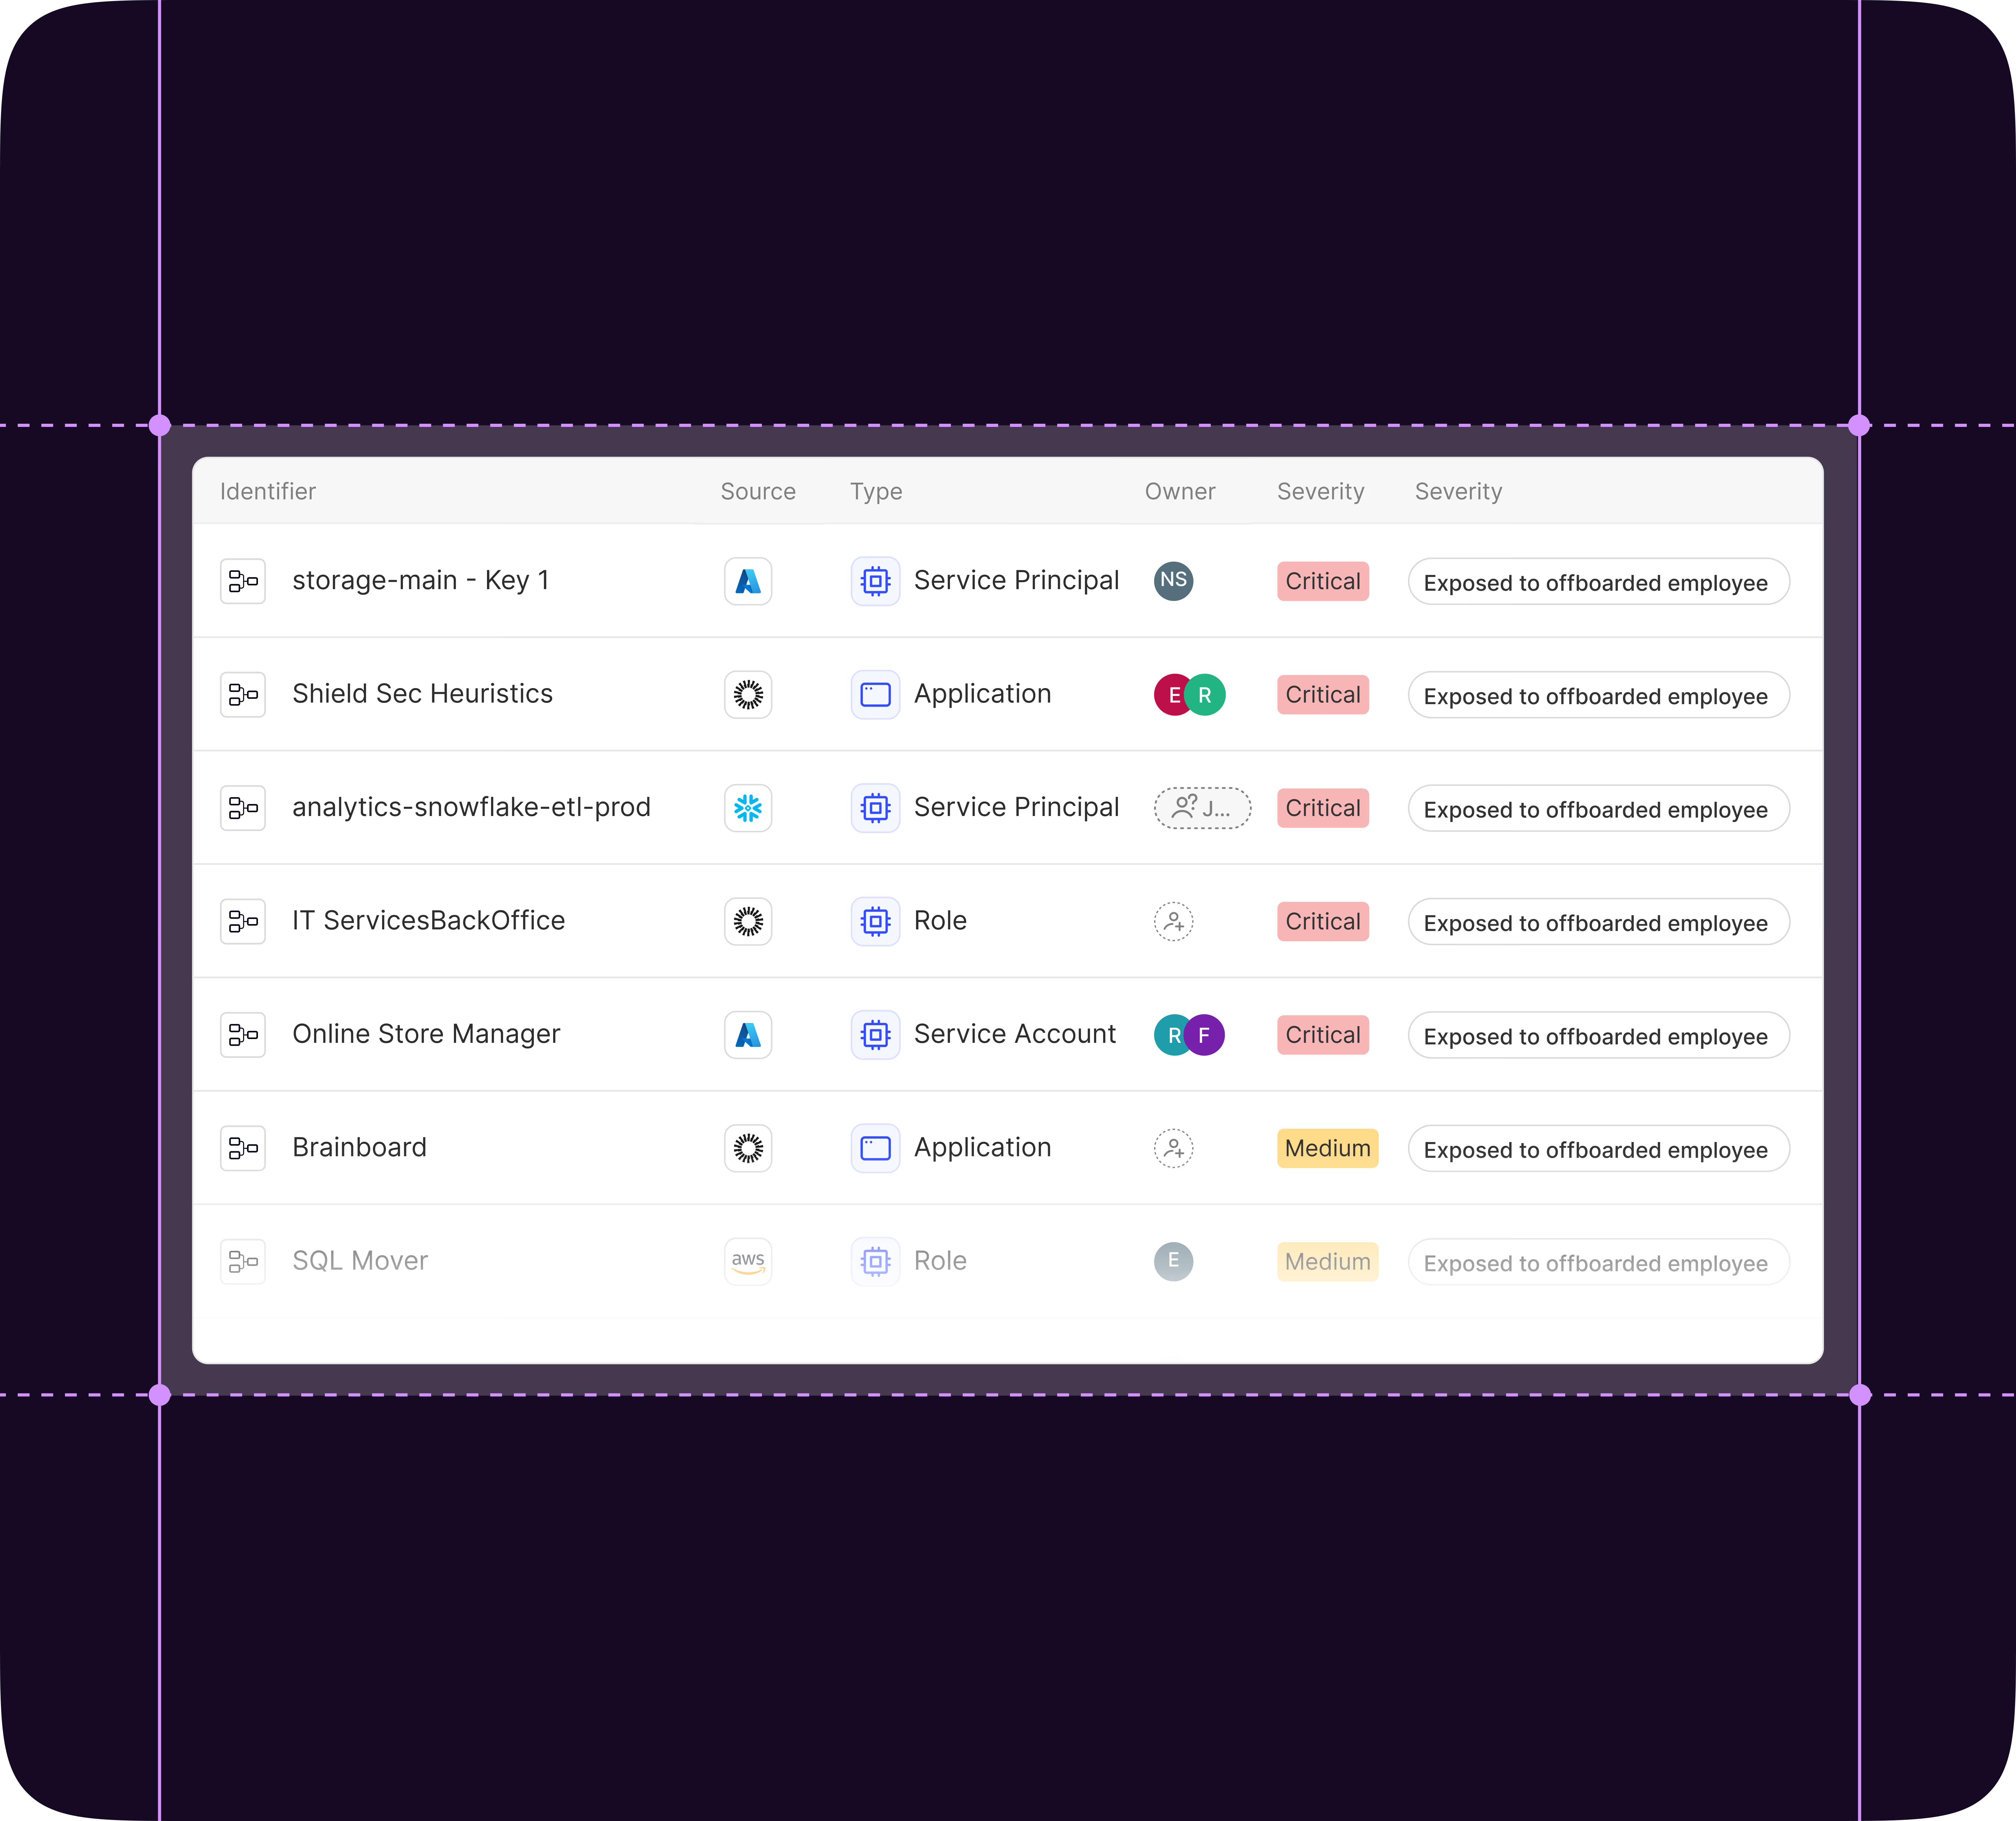
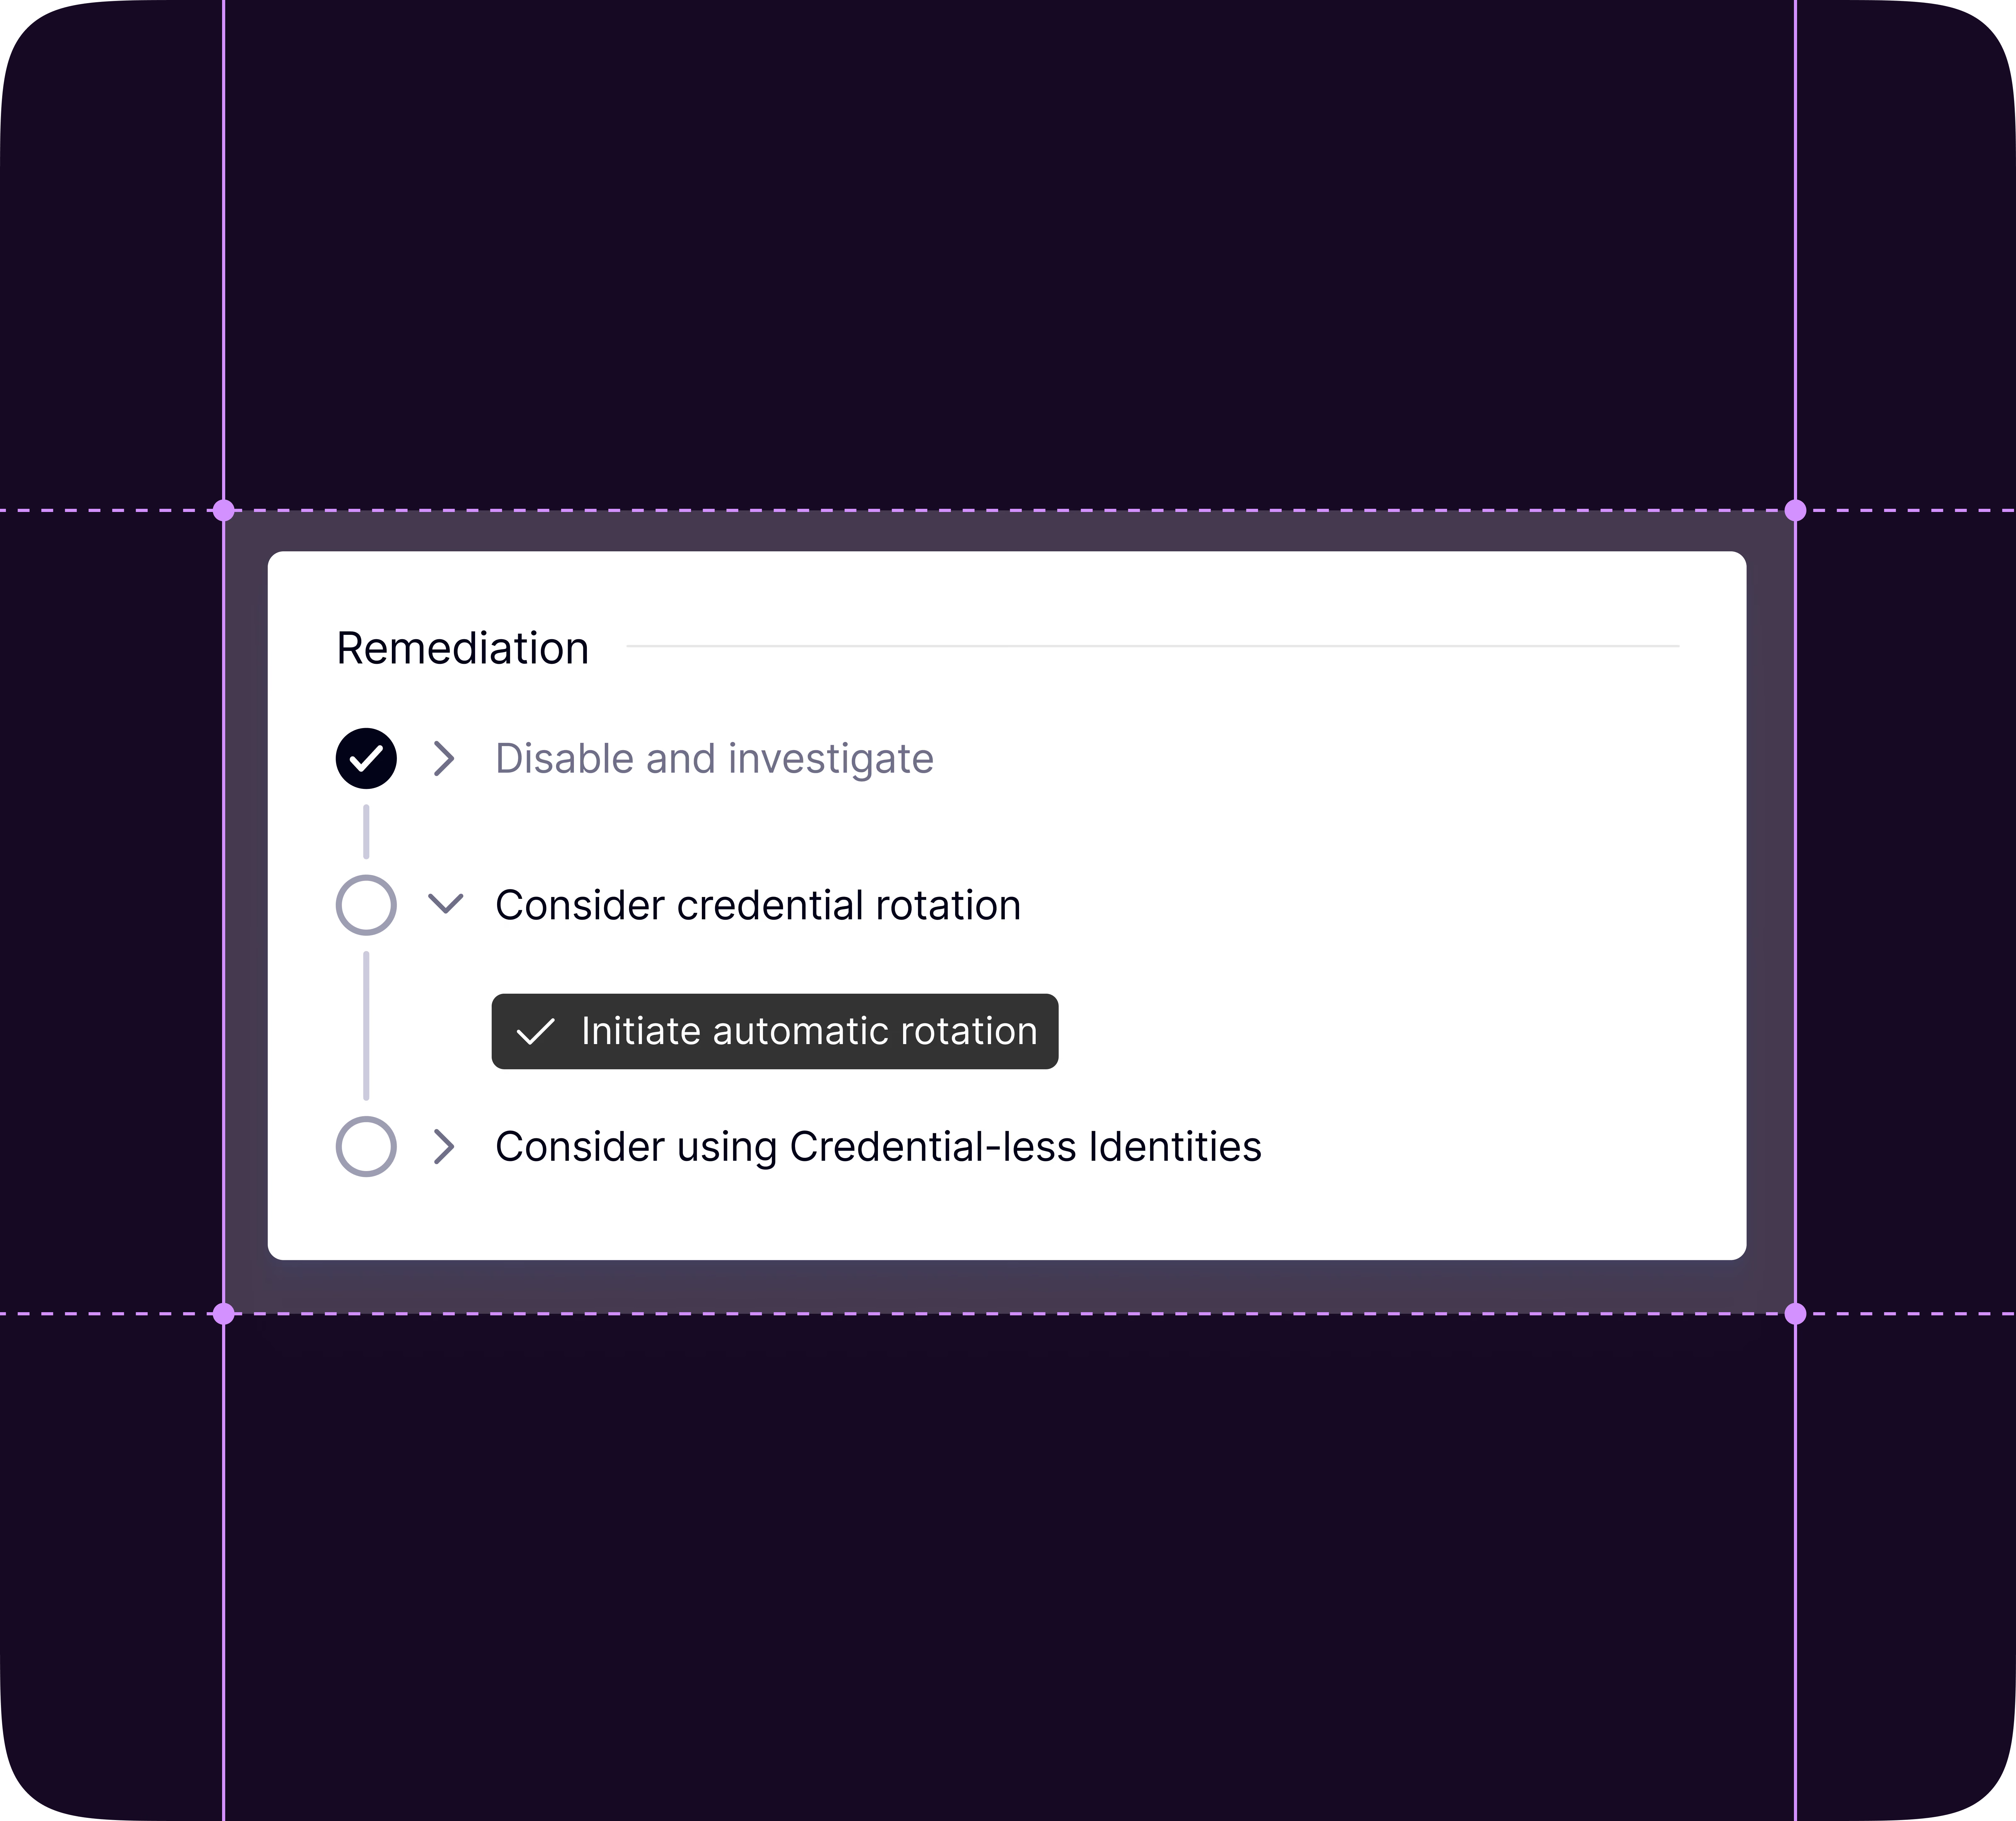
Evaluate every identity against your security policies and rank each gap by privilege, exposure, and the data at stake. Resolve issues with a guided step, a script, or one click, for one identity or hundreds, knowing what depends on it before anything changes. Disable first, restore if needed, and delete only after a grace period.
Govern non-human identities and
agentic access at scale
Connect in days. Enforce through
the stack you already own.
Connect through the control plane. Agentless API connectors deliver inventory, ownership, and data context in days. Enforcement then ties into the infrastructure you already run, from identity providers and cloud platforms to vaults and the gateway your AI agents connect through.


Complete security across your agentic estate
Ensure visibility, governance and protection for all AI and agentic tools in your organization


One platform to secure AI - from data to identity to action
At rest, in motion, and in use.
The most intelligent data security control plane
One AI brain to reduce all DLP noise and toil
See every non-human identity. Govern what it can reach.
Secure everything agents can see and do
Hands-free data risk reduction and continuous compliance
End-to-end management of the Cyera platform
Expert-led data breach response support
Protect your data in minutes
FAQs
A non-human identity is how software proves who it is. Service accounts, service principals, cloud roles, and AI agents all use one to access systems and data, signing in with credentials like API keys, tokens, or certificates instead of a person logging in. On average, they outnumber human identities 80 to 1.
They were built for different problems. IGA governs the people in your organization, and PAM protects the privileged accounts it has been told about. Most non-human identities fall outside both. Cyera Identity finds them, shows who uses each one and what data it reaches, and governs it alongside the tools you already run.
No. It makes the vaults you already run more useful. Cyera Identity sees the secrets across all of them, PAM vaults included, shows who uses each one, and rotates them into your cloud vaults or HashiCorp Vault without breaking what depends on them, and without ever storing them. One Fortune 500 logistics company cut rotation effort by 35%.
The same way it secures every other non-human identity, because that's what an agent is. It finds the agents in your environment, the identities they run on, and any shadow AI. When an agent needs access, it gets a short-lived identity scoped to its intent and your policies, removed when the work is done.
Cyera uses an AI-native classification engine that adapts to each environment, identifying both common sensitive data and data unique to your business. This approach eliminates traditional blind spots and delivers 95%+ precision without manual rules or ongoing tuning.