
Agents in Microsoft environments act on sensitive data every day, whether a Copilot Studio agent is turning customer financial data into a report and saving it to a personal OneDrive, or an HR assistant is trying to email restricted records outside the company. An agent can reach everything it has access to in seconds, where a person touches about 4% of it, and by the time an action shows up in a log, it’s too late.
At Microsoft Ignite, Cyera is announcing its work with Microsoft to contribute Cyera Agent Guardian findings through Microsoft Sentinel to enrich dynamic agent risk for supported agents. Microsoft Agent 365 is the observability platform for AI, giving organizations a shared view of their AI estate to help them manage, govern, secure, and understand the business value of AI, with Microsoft Entra Agent ID as the identity anchor. Agent Guardian adds protection grounded in what agents actually do; it inspects every tool call at runtime, recognizes when an action involves sensitive data, enforces policy inline, and can quarantine a compromised agent.
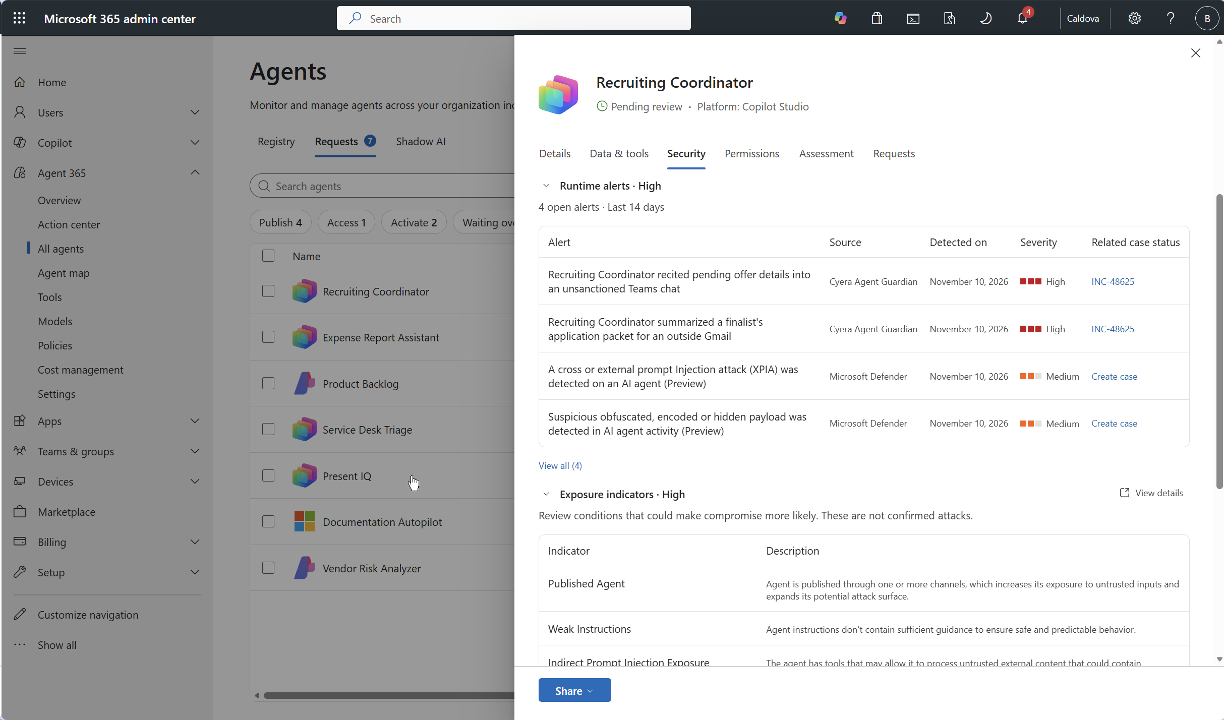
The integration connects the two. Through Microsoft Sentinel, Agent Guardian alerts feed Agent 365 with runtime evidence for supported agents, including whether an action involved sensitive data, who was acting through the agent, and which policy it violated. Each alert is correlated with the relevant agent and keeps Cyera as the detecting source. Microsoft combines it with its own runtime alerts to calculate a single dynamic agent risk level per agent, which surfaces in the Microsoft 365 admin center (Agent 365), Microsoft Defender, Microsoft Entra, and Microsoft Purview.
“Microsoft Agent 365 helps leaders turn AI observability into informed decisions about how they manage, govern, and secure agents and understand their business value. Our work with Cyera will add data-aware runtime evidence for supported agents alongside Microsoft’s native security signals, helping customers understand how agents interact with sensitive data and prioritize investigations.”
Ray Smith, Corporate Vice President, Agent 365 Product, Microsoft.
What the Agent Actually Did With the Data
Knowing what an agent could do is the first step, but Agent Guardian tells you what it did. Each alert Cyera sends to Sentinel describes a specific action and carries four things Agent 365 can use:
• What happened. The action itself, such as an agent saving a customer workbook to a personal OneDrive or emailing records outside the company.
• Whether sensitive data was involved, and how severe. The data the action touched, classified by sensitivity, and the severity of the impact.
• Who was behind it. The agent, including Microsoft Entra Agent ID where applicable, and the person acting through it with their role.
• Which policy it violated, and why. The Cyera policy, its severity, and Cy’s plain-language triage assessment.
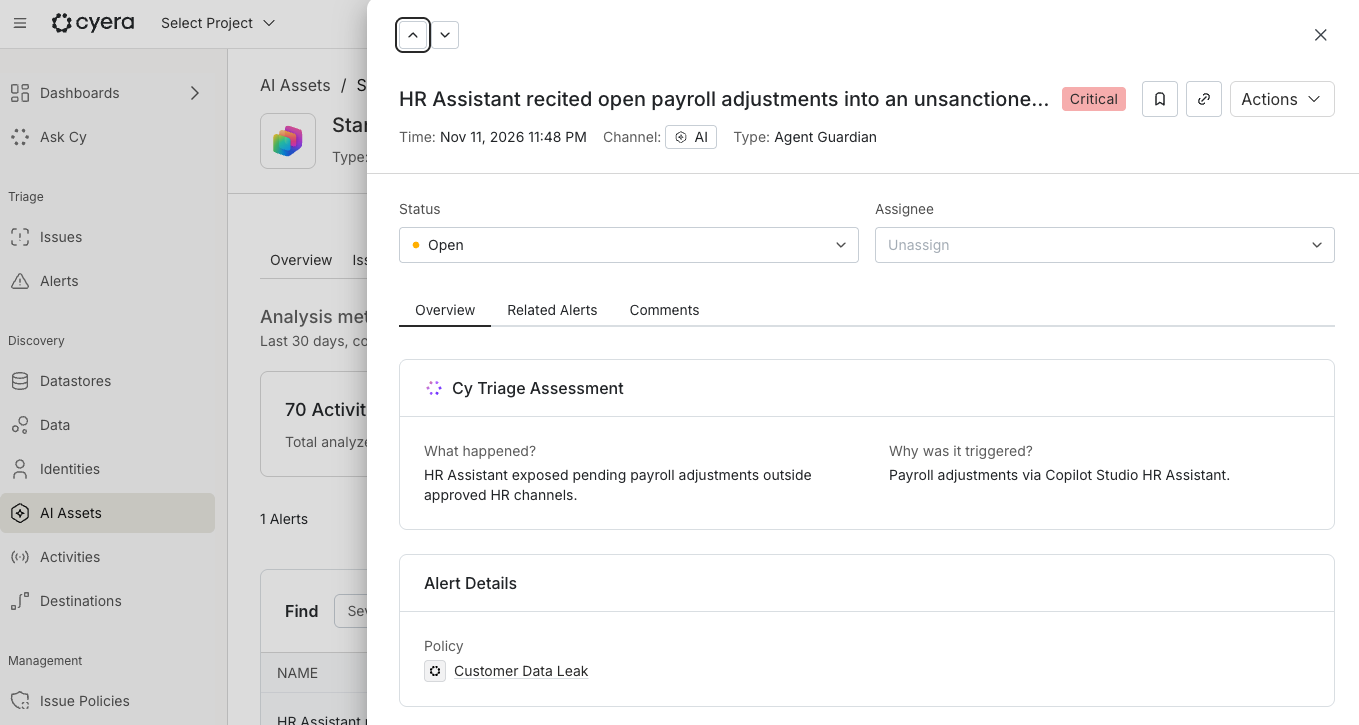
Each alert is a finding about an action, not a snapshot of configuration. Below, a Copilot Studio HR Assistant exposes pending payroll adjustments outside approved HR channels, which violates the Customer Data Leak policy.
How It Works
Take an HR Assistant that tries to email restricted HR records externally. Agent Guardian recognizes the records and enforces policy on that one action. The supported finding can flow through Microsoft Sentinel, retain attribution to Cyera, and be correlated with the agent to inform Microsoft-calculated dynamic agent risk and investigation.
Cyera’s detections are policy-driven and based on runtime activity. When an action through an agent triggers a policy, such as Customer Data Leak, Agent Guardian takes the alert, transforms it into a schema that Microsoft can use to quickly interpret the alert, and pushes it to your Microsoft Sentinel environment.
Each event follows a structured schema: event fields (EventType and SignalCategory, which marks these as RuntimeRisk signals), detection fields (AlertName, DetectionId, RuleName, ThreatCategory), and entity fields that identify the agent (EntityType, EntityId, EntityName, IdentityType). Cyera’s original severity and status are preserved in EventOriginalSeverity and AlertOriginalStatus.

The Benefits
- A higher-fidelity view of how agents are used. For agents Cyera monitors, Cyera adds runtime context on severity and data sensitivity, enriching Microsoft’s assessment alongside the native runtime alerts and posture risks it already tracks.
- Faster triage in tools you already use. Analysts can investigate supported Cyera alerts in Microsoft Defender XDR through Microsoft Sentinel ingestion, alert generation, and correlation workflows. Each alert enriches Microsoft-calculated dynamic agent risk with what happened, which policy fired, and who was involved.
- Defensible decisions. Every alert names the action, the person, the policy, and Cyera’s reasoning, so security leaders can pair Microsoft-calculated agent risk with Cyera’s agent context to see what’s at stake and decide which investigations come first.
Get In Early
Private preview is open to a limited number of Cyera customers. Reach out to your Cyera account team to request access for your tenant.
Not a customer yet? Book a demo to see Agent Guardian in action.
Learn more about the Cyera and Microsoft partnership.

Get your AI Security Assessment