Integration at a glance
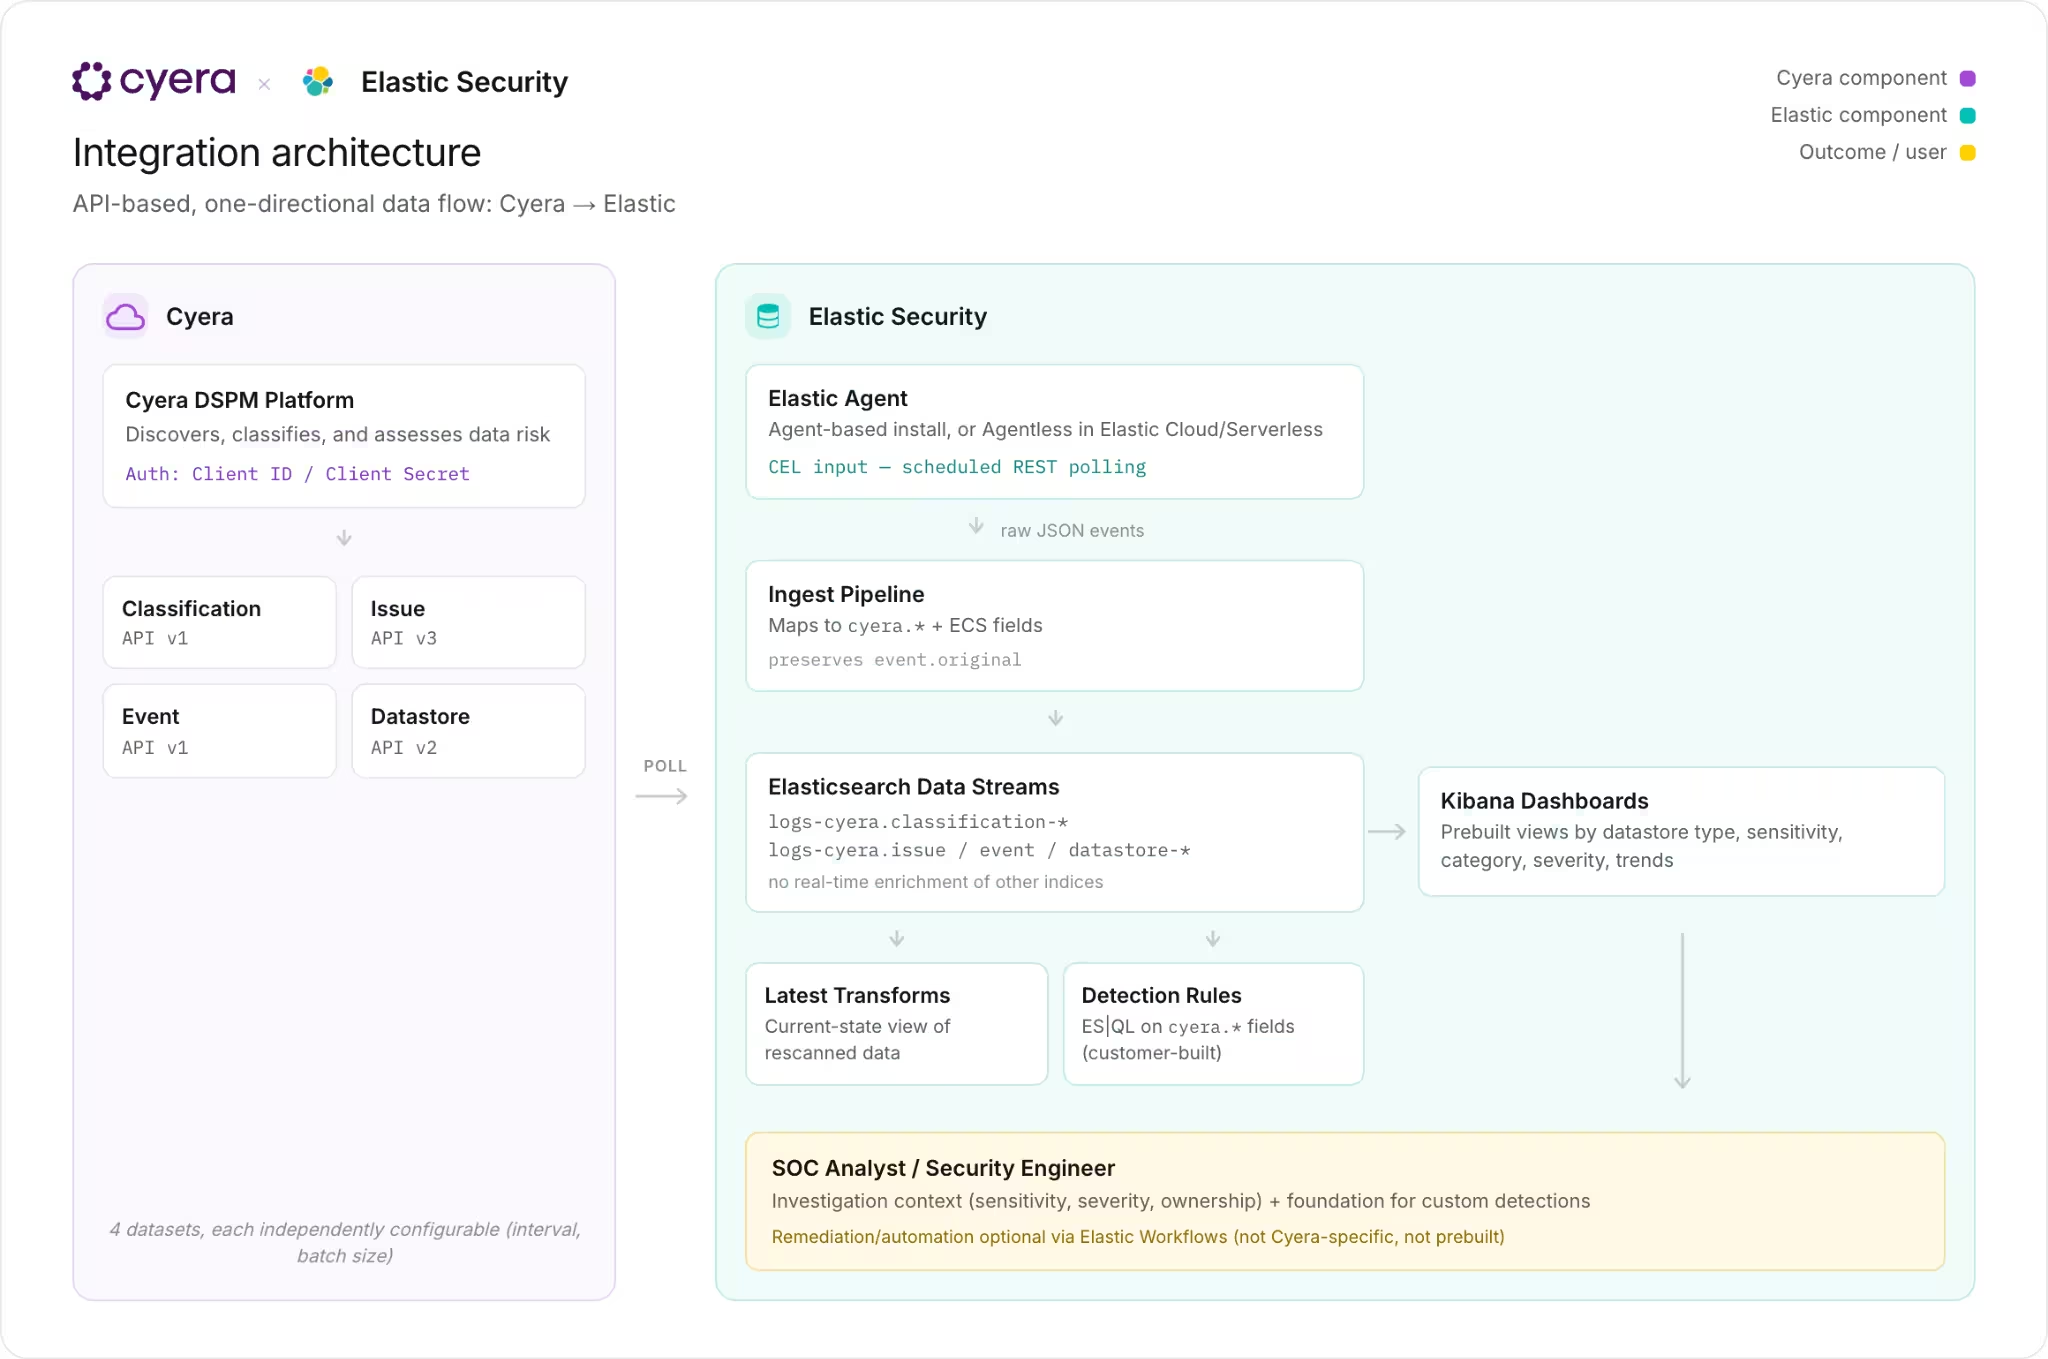

Security operations teams typically investigate SIEM and XDR alerts in isolation, with little or no visibility into the data those alerts affect. While security telemetry identifies suspicious activity, it rarely includes the context or overall risk of the data. As a result, analysts often spend valuable time determining whether an alert involves critical or regulated data, making it difficult to accurately prioritize incidents and build risk-aware detections.

By integrating Cyera with Elastic Security, data context is brought directly into the investigation workflow. Analysts can immediately see the sensitivity, severity, and ownership of the affected data within Elastic, enabling faster investigations and more accurate prioritization driven by actual data risk rather than security events alone.
Benefits of the Integration

How It Works

About Elastic
Elastic Security is an agentic security operations platform that unifies SIEM (Security Information and Event Management) and XDR (Extended Detection and Response) into a single platform, detecting, preventing, and responding to cyber threats across an environment in near real time. By combining prevention, detection, and response capabilities, Elastic Security helps organizations reduce their security risk.